Capabilities & Products

Defensive Cyber Capabilities & Systems

An uncompromising suite of defensive cyber operations, sovereign platforms, and zero-trust engineering tailored to your organization's highest-risk vectors, backed by 19+ years of military cyber heritage.

PROPRIETARY SOFTWARE // DEVELOPED BY CYBERNETICKS
GryphOpsv1.0 ENTERPRISE

Unified Security Operations Platform

Born from 19+ years of joint military defense operations, GryphOps delivers the definitive operational breakthrough: simultaneous, in-depth analysis of both network wire traffic and host system logs in one unified tool. One sovereign platform that secures your entire Cyber Arena.

CORE BREAKTHROUGH // THE CYBER ARENA
UNIFIED HOST + NETWORK LOG FUSION

Analyze Both Network & Host Logs in One Tool: Complete Cyber Arena Coverage

The single biggest benefit of GryphOps is eliminating the visibility chasm between wire packet flows and endpoint logs. Instead of operating fragmented tools for network capture and endpoint agents, GryphOps unifies live wire packet flows and deep host event logs into a singular, high-performance analytical plane. Correlate a wire-level connection anomaly directly to the responsible host process tree, binary signature, and user session in real time. One tool that takes care of your entire Cyber Arena.

WIRE SPECTRUM

Proprietary Network Sensor

Autonomous wire packet capture daemons, TAP/SPAN/eBPF ingestion & socket telemetry.

  • Proprietary GryphOps Network Sensor daemons (TAP/SPAN/eBPF)
  • Snort 3 signature matching & YARA hex stream inspection
  • Mutual mTLS streaming directly to Gryphon Engine port 4203
HOST SPECTRUM

Proprietary Host Agent

Parent/child process trees, Windows Security events, Linux auditd & file integrity.

  • Proprietary GryphOps Host Agent for Linux & Windows
  • Deterministic process lineage (PPID → PID → binary hash)
  • Continuous file integrity monitoring (FIM) & memory guards
BIGGEST BENEFIT

In-Depth Arena Analysis

Total cross-domain correlation: zero blind spots across your entire cyber footprint.

  • Deterministic packet-to-PID causal attribution
  • Isolation Forest ML scoring across wire & host vectors
  • Zero swivel-chair analysis: 1 pane of glass, 0 blind spots
⚡
Wire-to-Host Causal AttributionWhen an anomalous outbound socket burst occurs, GryphOps instantly identifies the responsible parent executable binary, PID, and user account without lag.
📊
TimescaleDB Dual-Spectrum HypertablesCombines host audit logs and eBPF network packets into a singular time-series database with columnar ZSTD disk compression and accelerated time-series indexing.
🎯
Unified MITRE ATT&CK ContextMaps lateral network movement (T1021) directly to host process injection (T1055) and credential harvesting (T1003) on a continuous tactical timeline.
🔒
Sovereign & Air-Gappable ArchitectureZero cloud lock-in. Deploys inside DoD enclaves, classified SCIFs, or sovereign Kubernetes clusters without leaking a single byte of telemetry externally.
BUILT-IN PROPRIETARY SENSORS // ZERO THIRD-PARTY AGENTS

Comes Standard With Its Own Proprietary Network Sensor & Host Agent

GryphOps is a completely self-contained cyber defense ecosystem. Unlike legacy SIEMs and monitoring platforms that require expensive third-party agent licensing, brittle integrations, or external forwarders, GryphOps comes standard with its own proprietary Network Sensor and Host Agent engineered from the ground up for high-throughput sovereign cyber operations.

PROPRIETARY NETWORK TELEMETRY
GryphOps Network Sensor

Autonomous wire capture daemon deployable on TAP, SPAN, mirror ports, or Kubernetes node interfaces. Encapsulates wire packets and streams directly to Gryphon Engine port 4203 over mTLS.

Promiscuous TAP / SPANeBPF Packet CaptureSnort 3 & Suricata PipelinesmTLS Port 4203 Ingestion
PROPRIETARY ENDPOINT TELEMETRY
GryphOps Host Agent

Low-footprint endpoint monitoring daemon for Linux and Windows systems. Concurrently streams kernel audit syscalls, deterministic process ancestry, binary hashes, and open socket bindings.

Linux auditd & eBPFWindows Security 4624/4688Deterministic Process TreesFile Integrity (FIM)
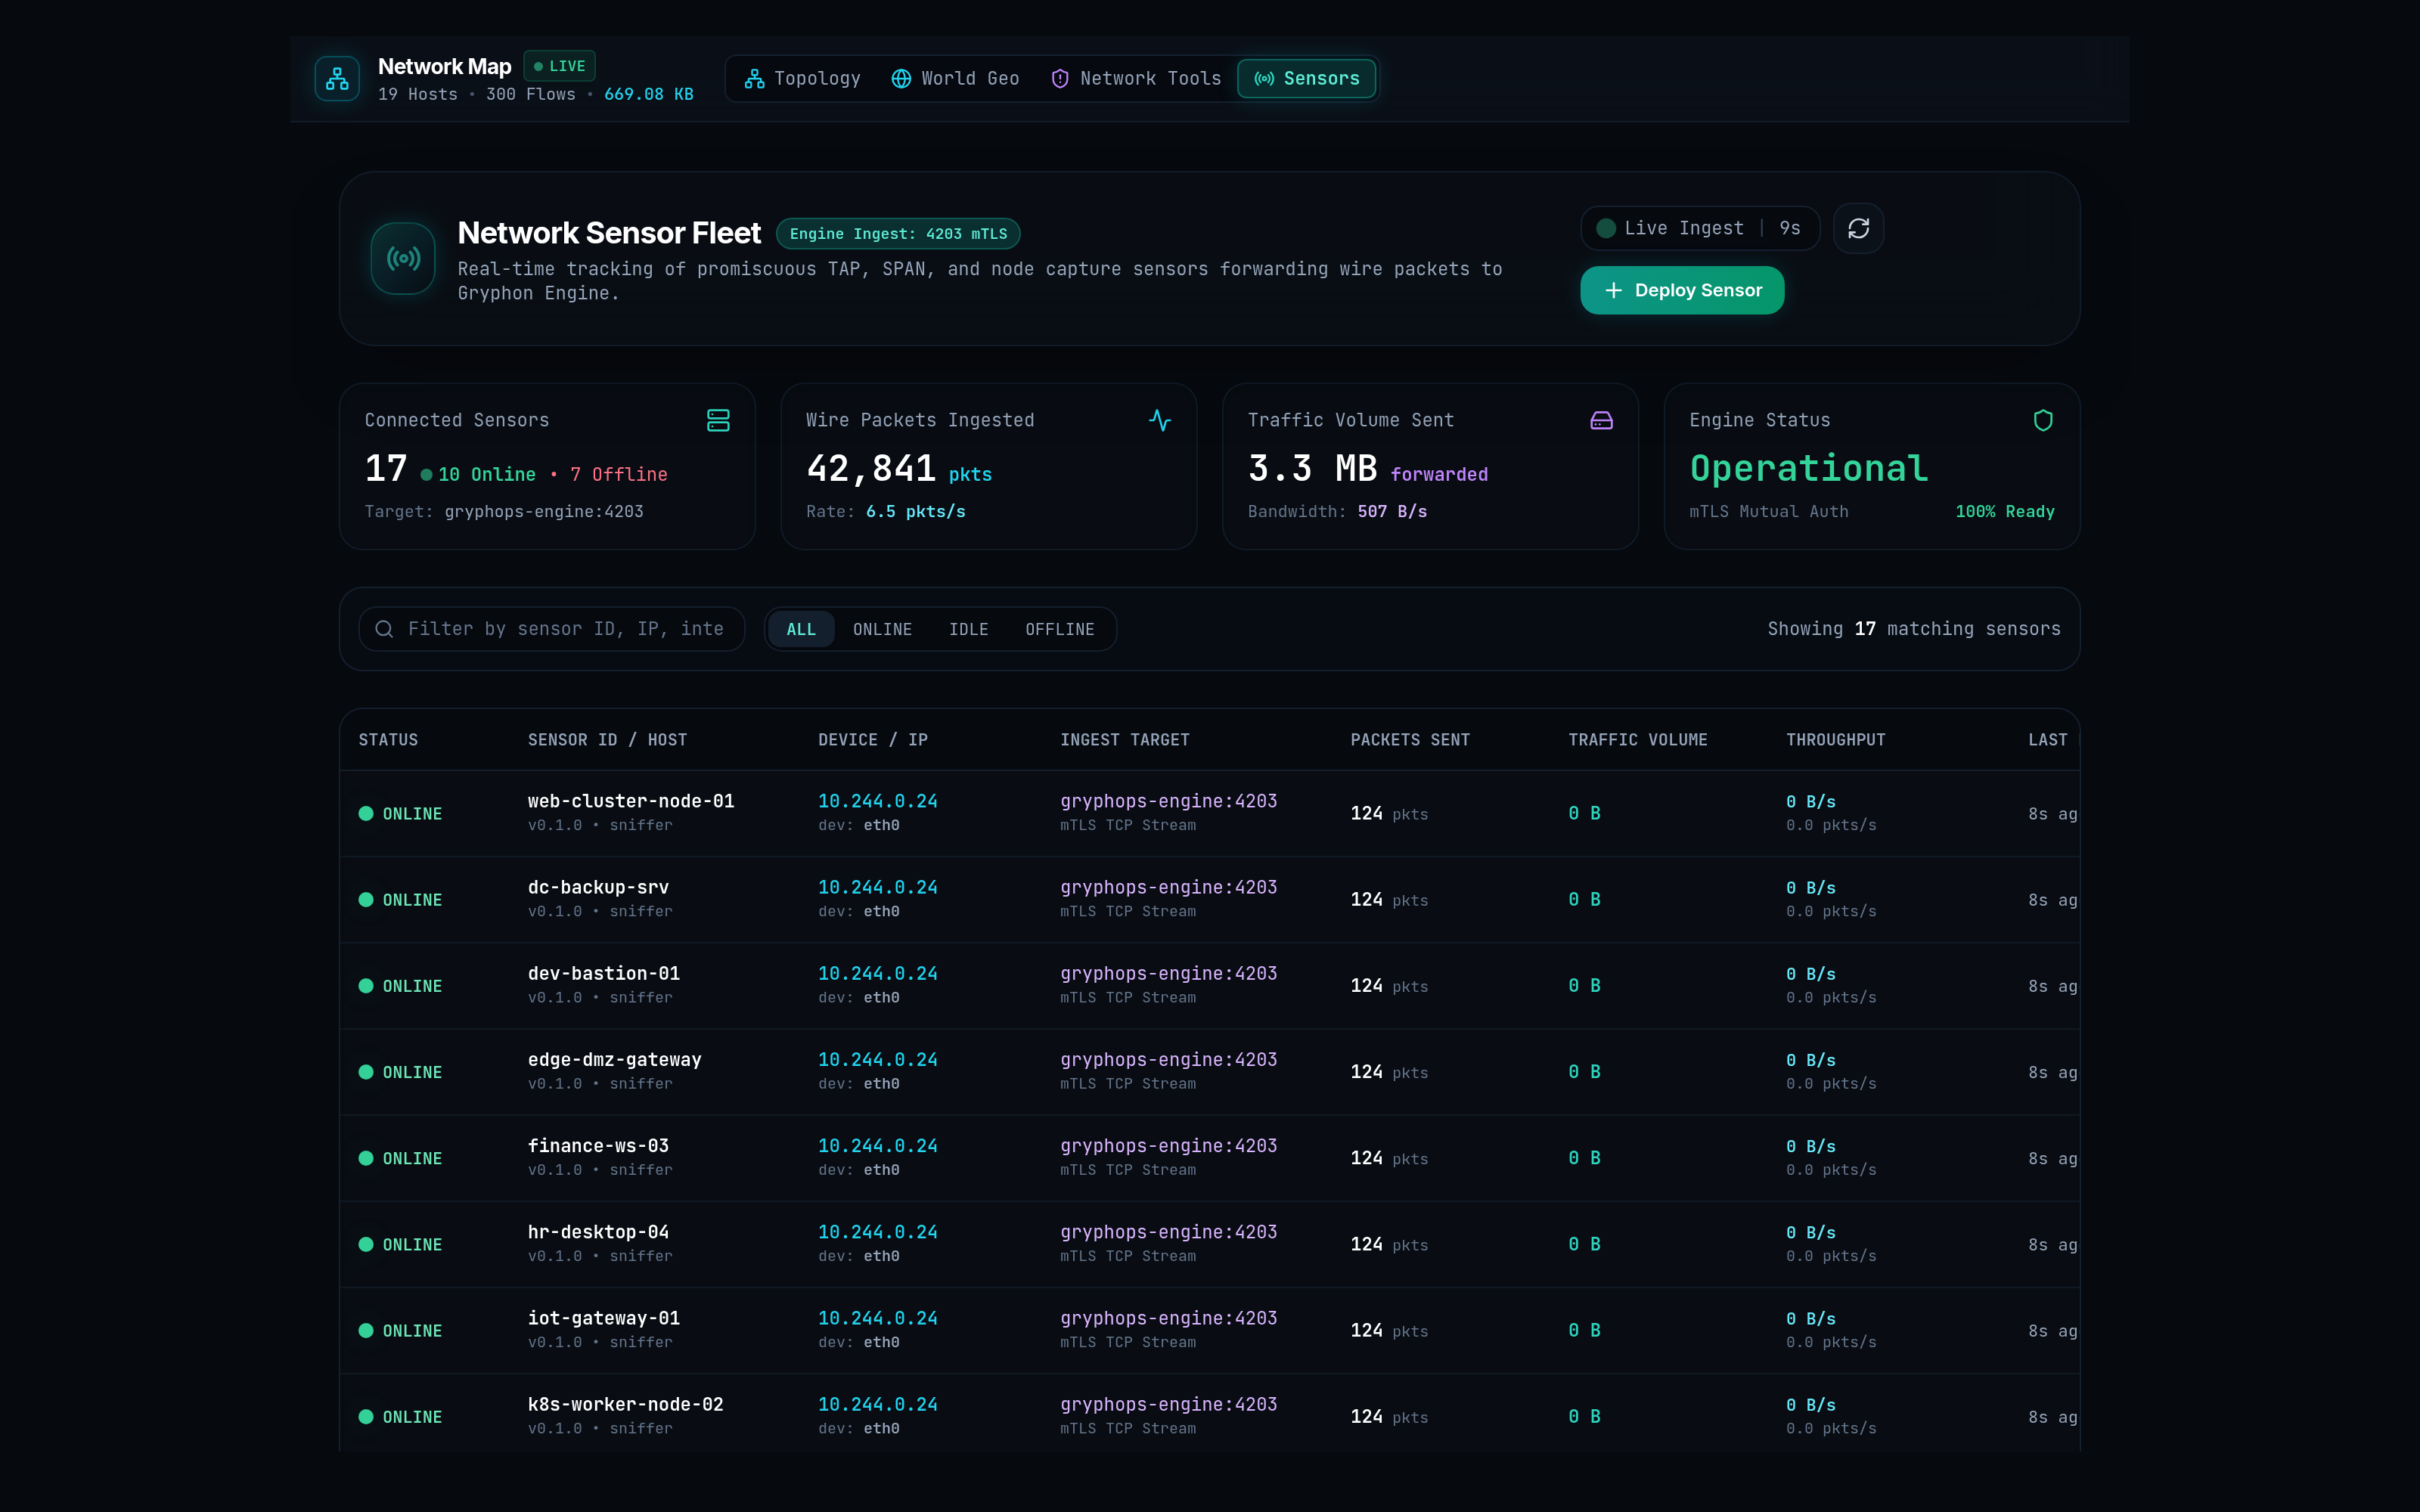
GRYPHOPS // NETWORK MAP // SENSOR FLEET CONSOLEhttps://gryphops.local/network-map/?view=sensors
● LIVE FLEET TELEMETRY
GryphOps Proprietary Network Sensor Fleet Management Console
CAPABILITIES DIRECTORYTap any card to view screenshot & architecture
GRYPHOPS // DEFENSE-IN-DEPTH CONSOLEOPERATIONS & FLEET
HYPERTABLE STREAM ACTIVE
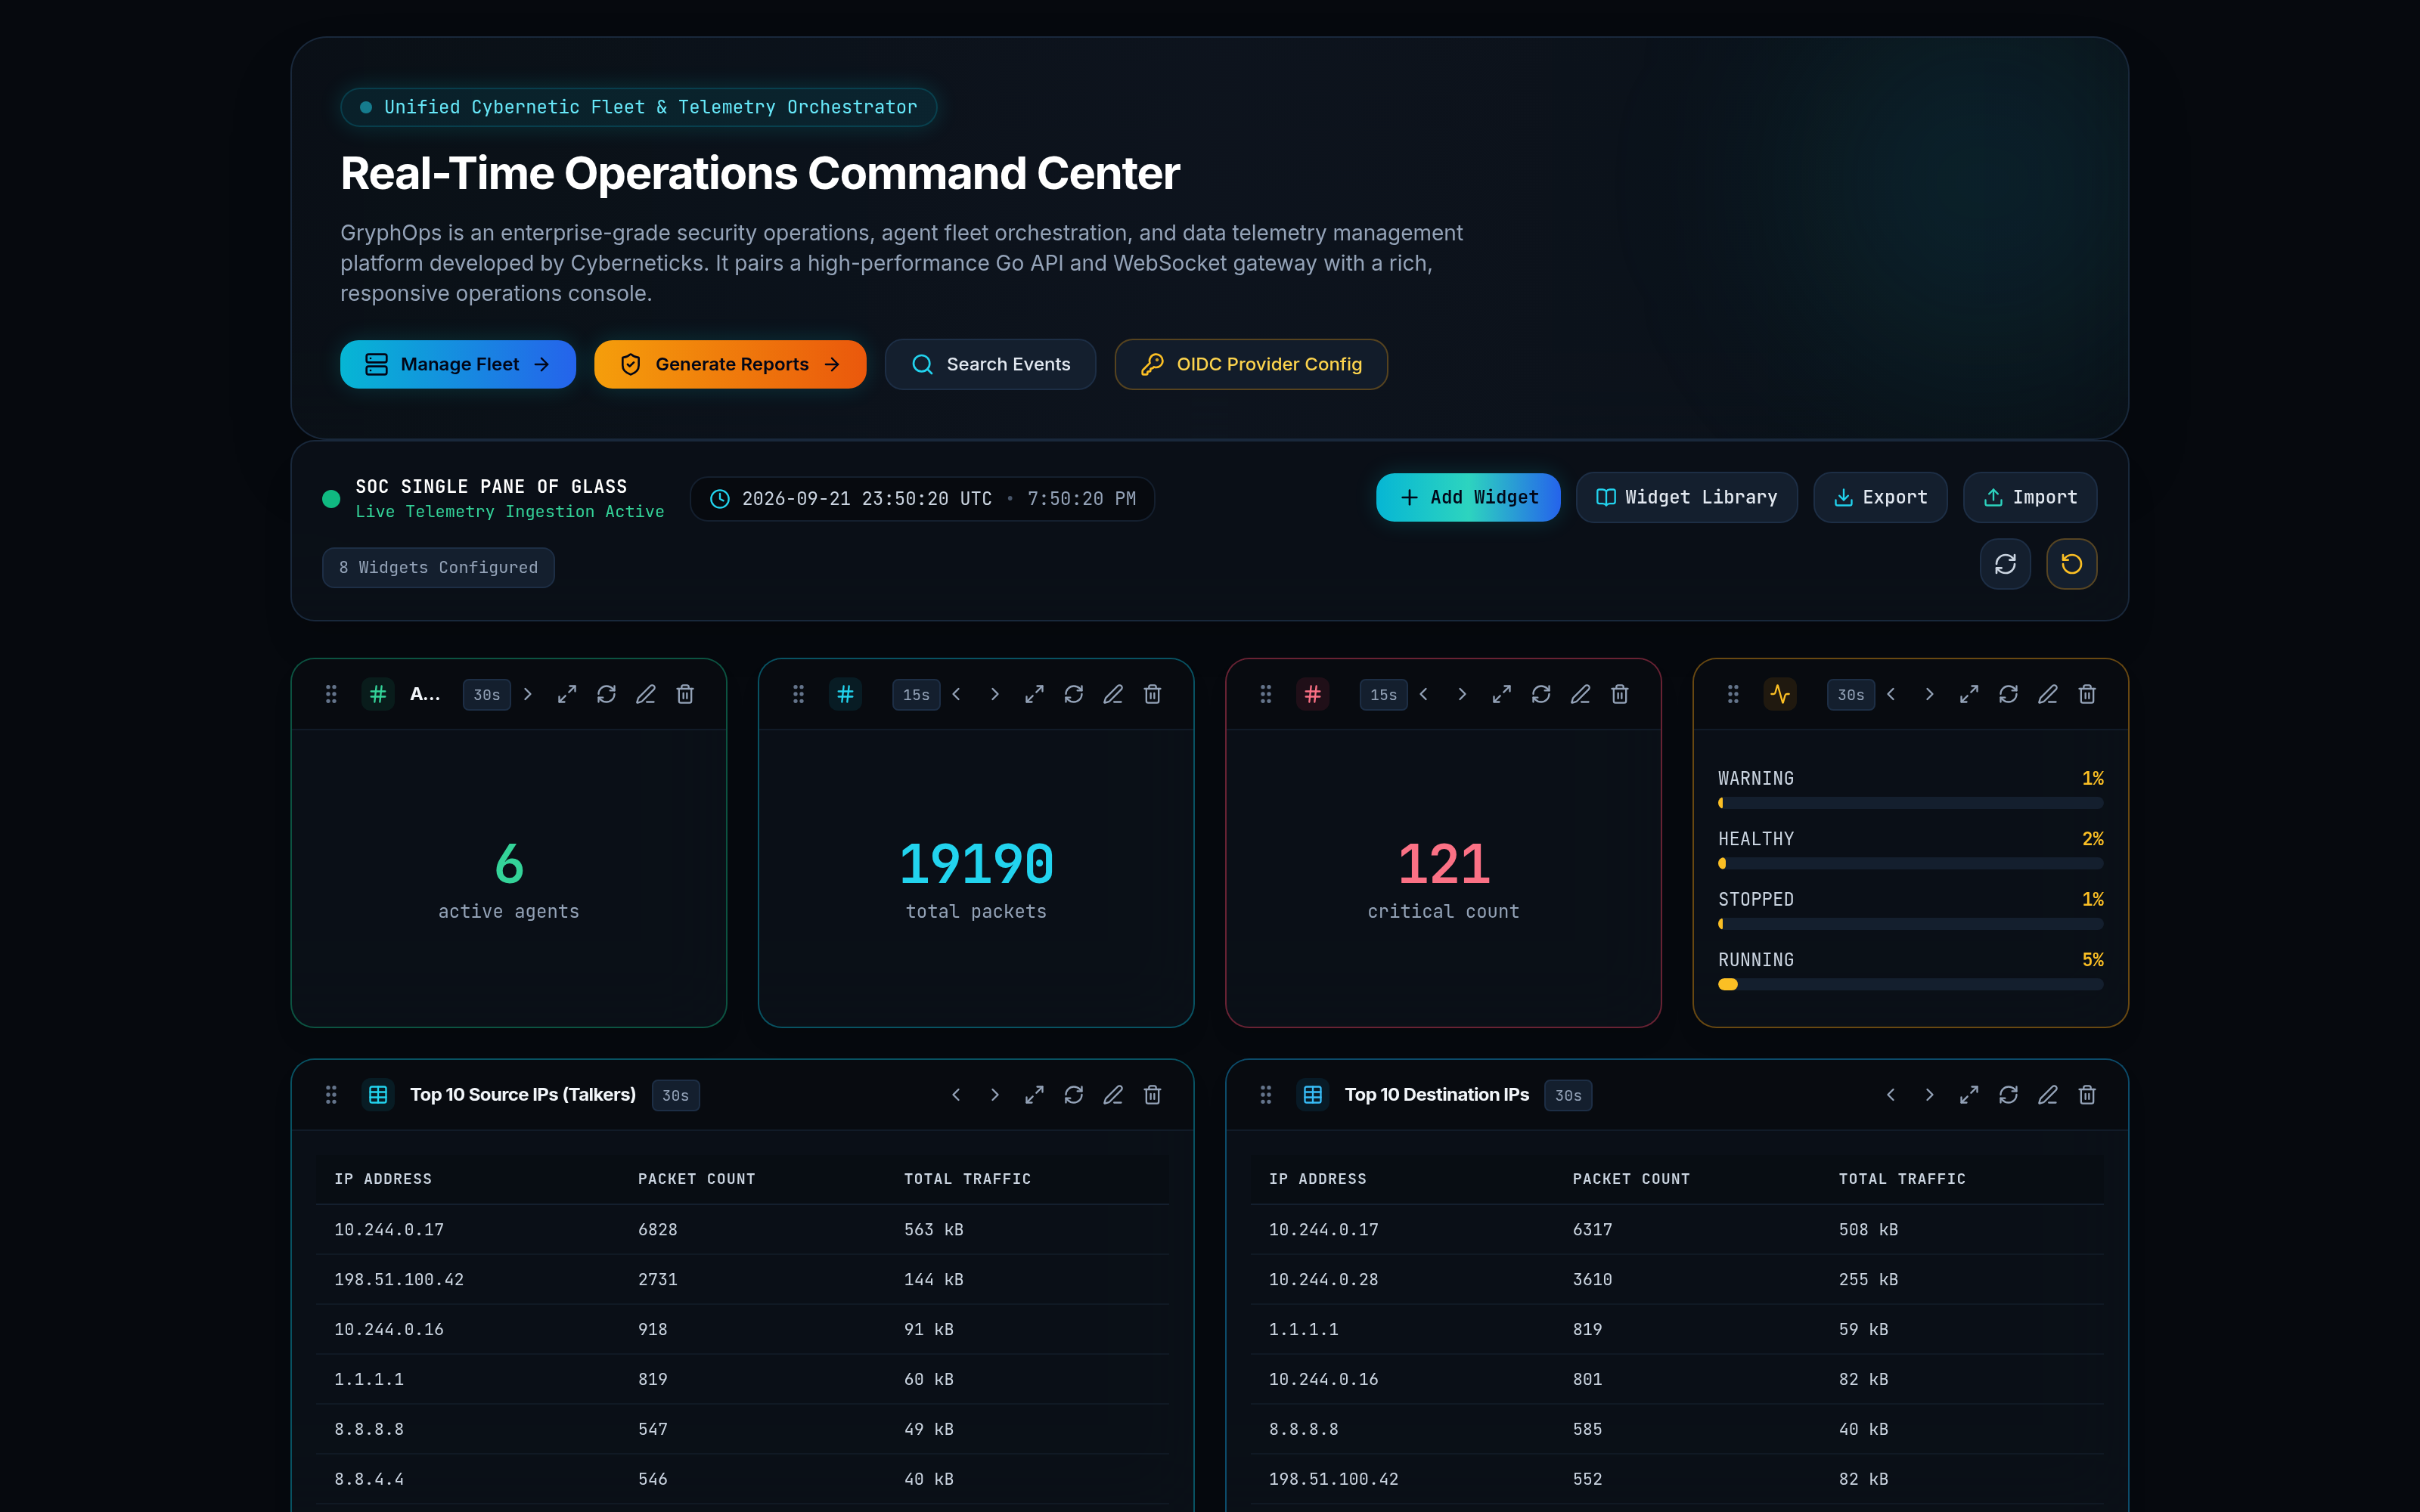
GryphOps Real-Time Operations Command Center
Real-Time Ingestion, Telemetry Topologies & Live Metrics

The central nervous system of the sovereign Cyber Arena: concurrently streams live host telemetry and raw wire packet events into TimescaleDB hypertables. Monitor active agent heartbeats, top source/destination talkers, protocol breakdowns, and critical alerts in a unified high-performance operational cockpit.

TimescaleDB HypertableseBPF IngestionLive WebSocketsReal-Time Query Streaming
KEY CAPABILITIES & ARCHITECTURE
Sub-millisecond packet & flow ingestion via eBPF sensors
Modular widget grid with real-time WebSocket event feeds
Instant Lucene-style search filters & direct SQL queries
Multi-tenant role-based access control with audit trails
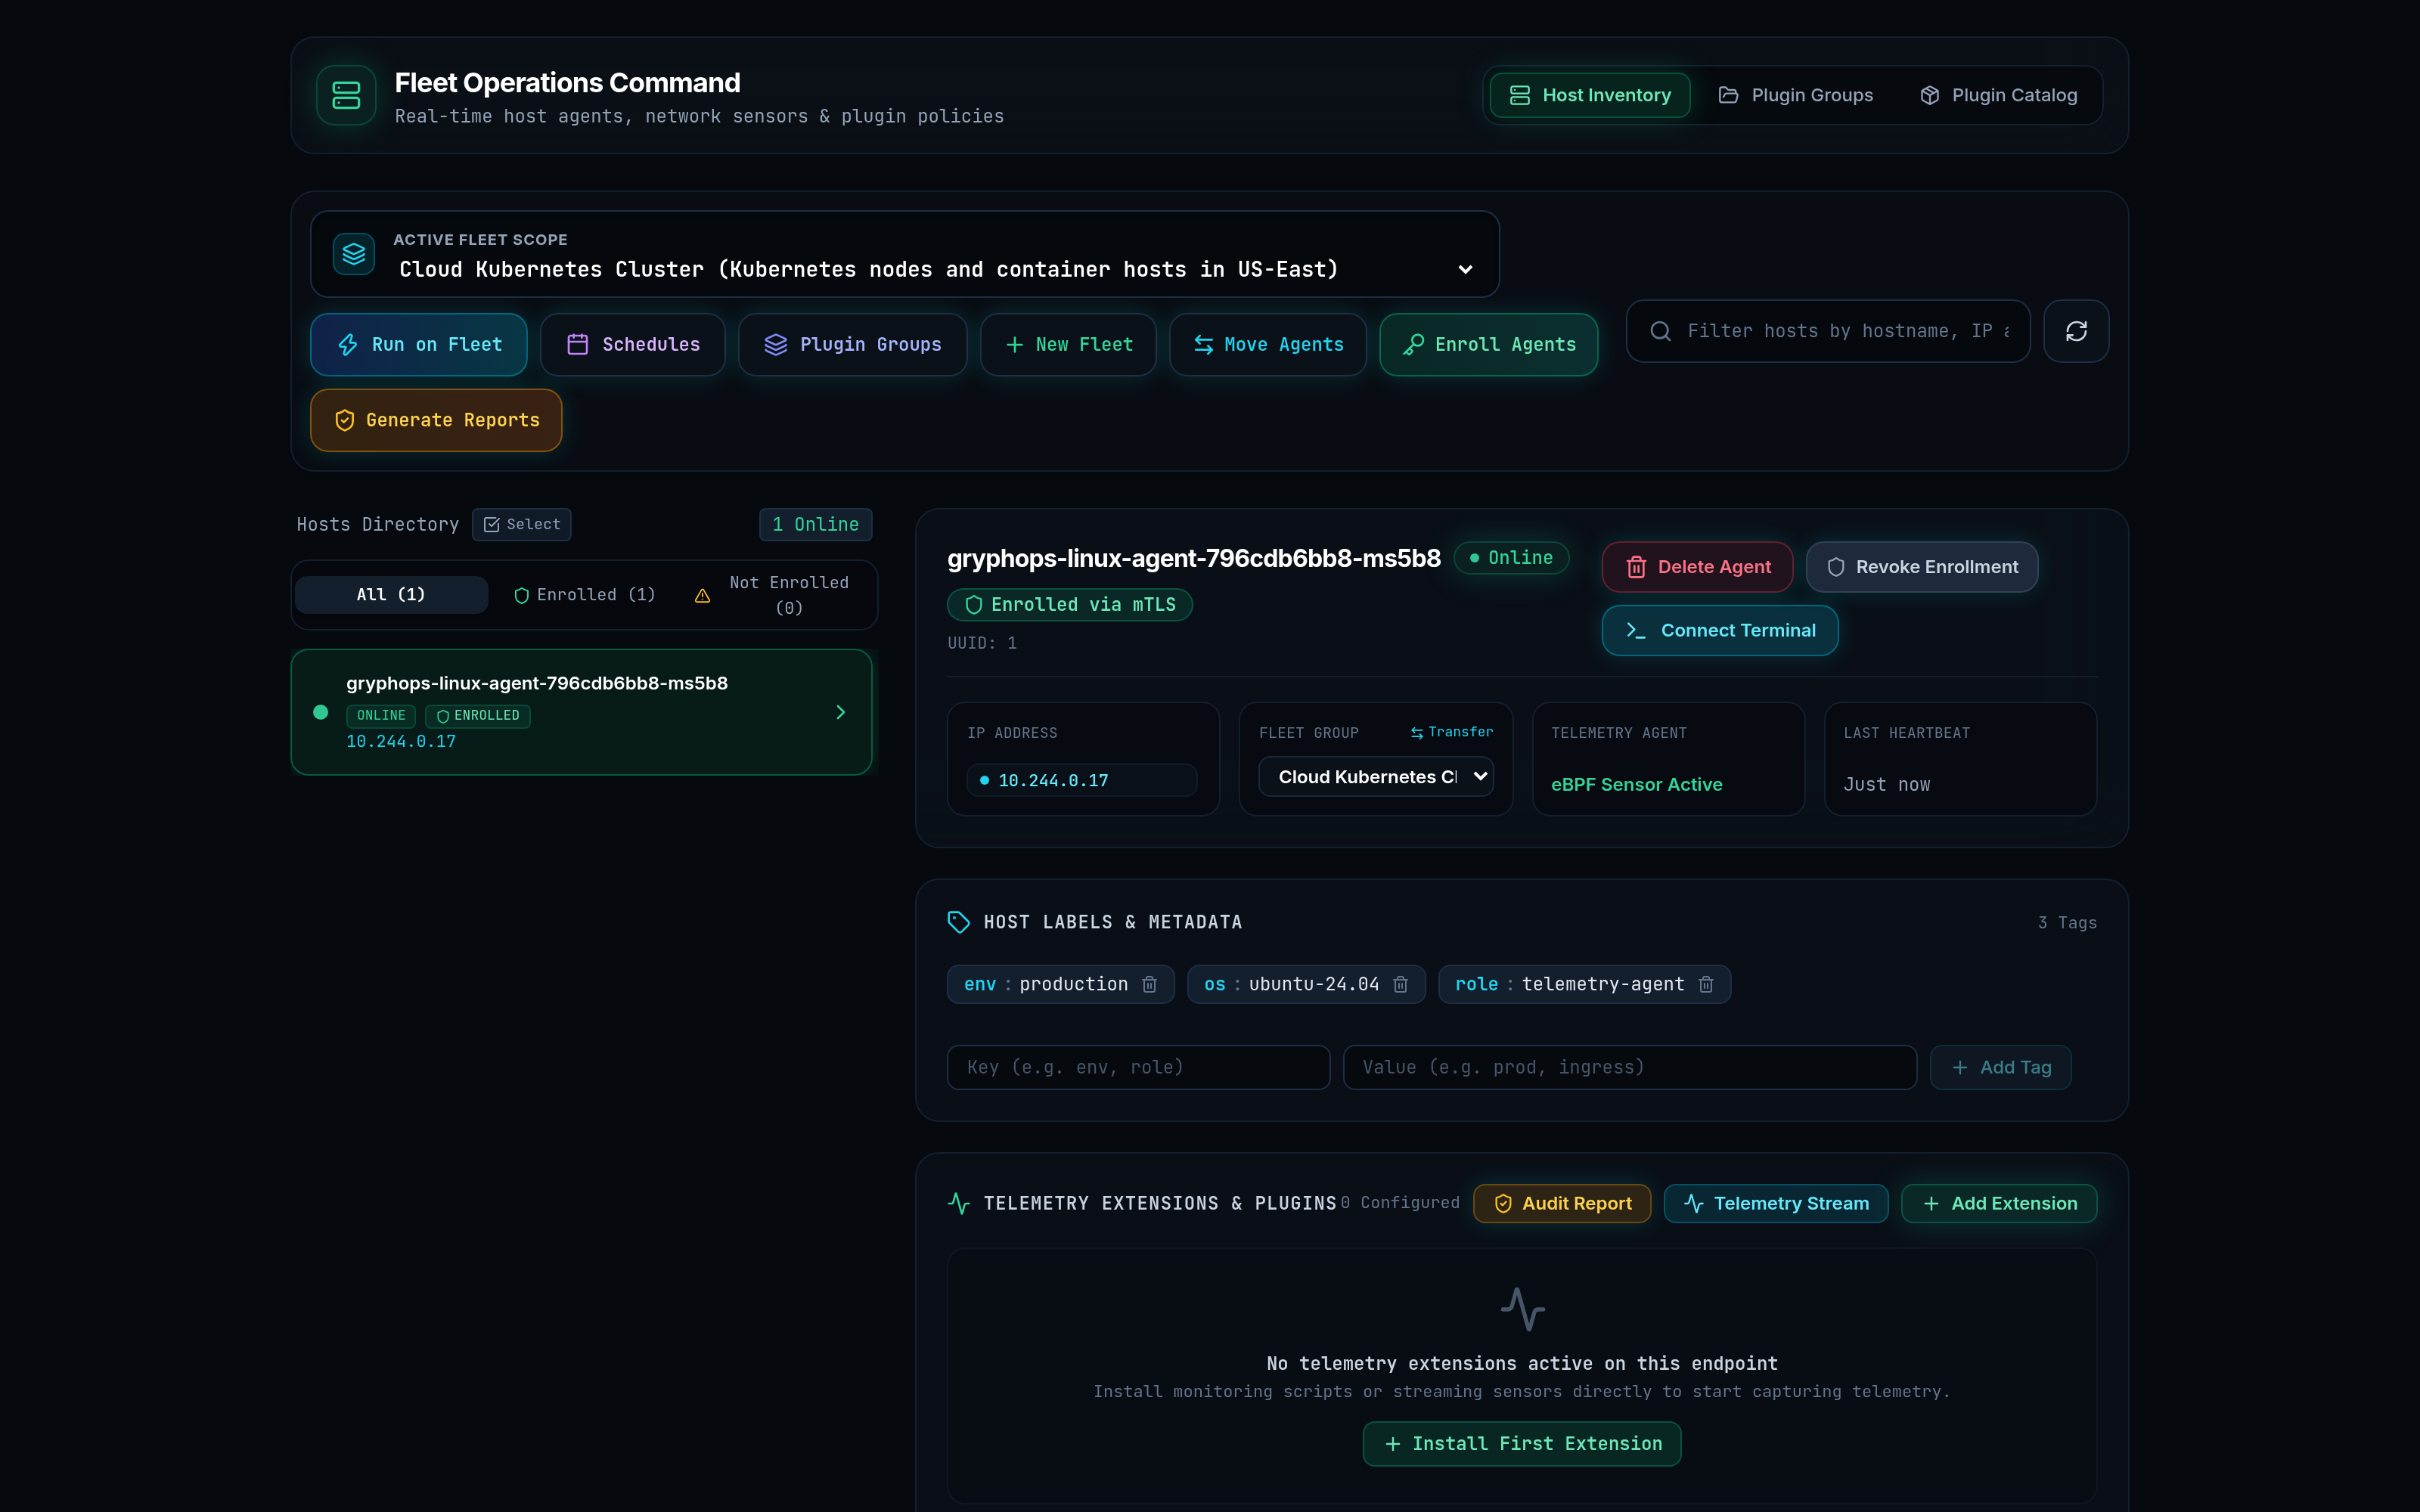
GryphOps Fleet Operations and Host Inventory
Host Enrollment, Policy Orchestration & Dynamic Extensions

Command sovereign endpoint agents across heterogeneous Linux distributions and Windows enclaves. Inspect real-time agent health, assign metadata tags and fleet groups, push dynamic telemetry extensions on the fly, and execute targeted security policies across thousands of endpoints without restarting daemons.

mTLS Agent TunnelLinux & WindowsHot-Load PluginsAir-Gap Ready
KEY CAPABILITIES & ARCHITECTURE
Cross-platform lightweight agents (Linux eBPF & Windows)
Zero-trust mutual TLS (mTLS) cryptographic agent tunnel
Dynamic plugin hot-loading & remote execution
Fleet-wide tag filtering, grouping, and bulk actions
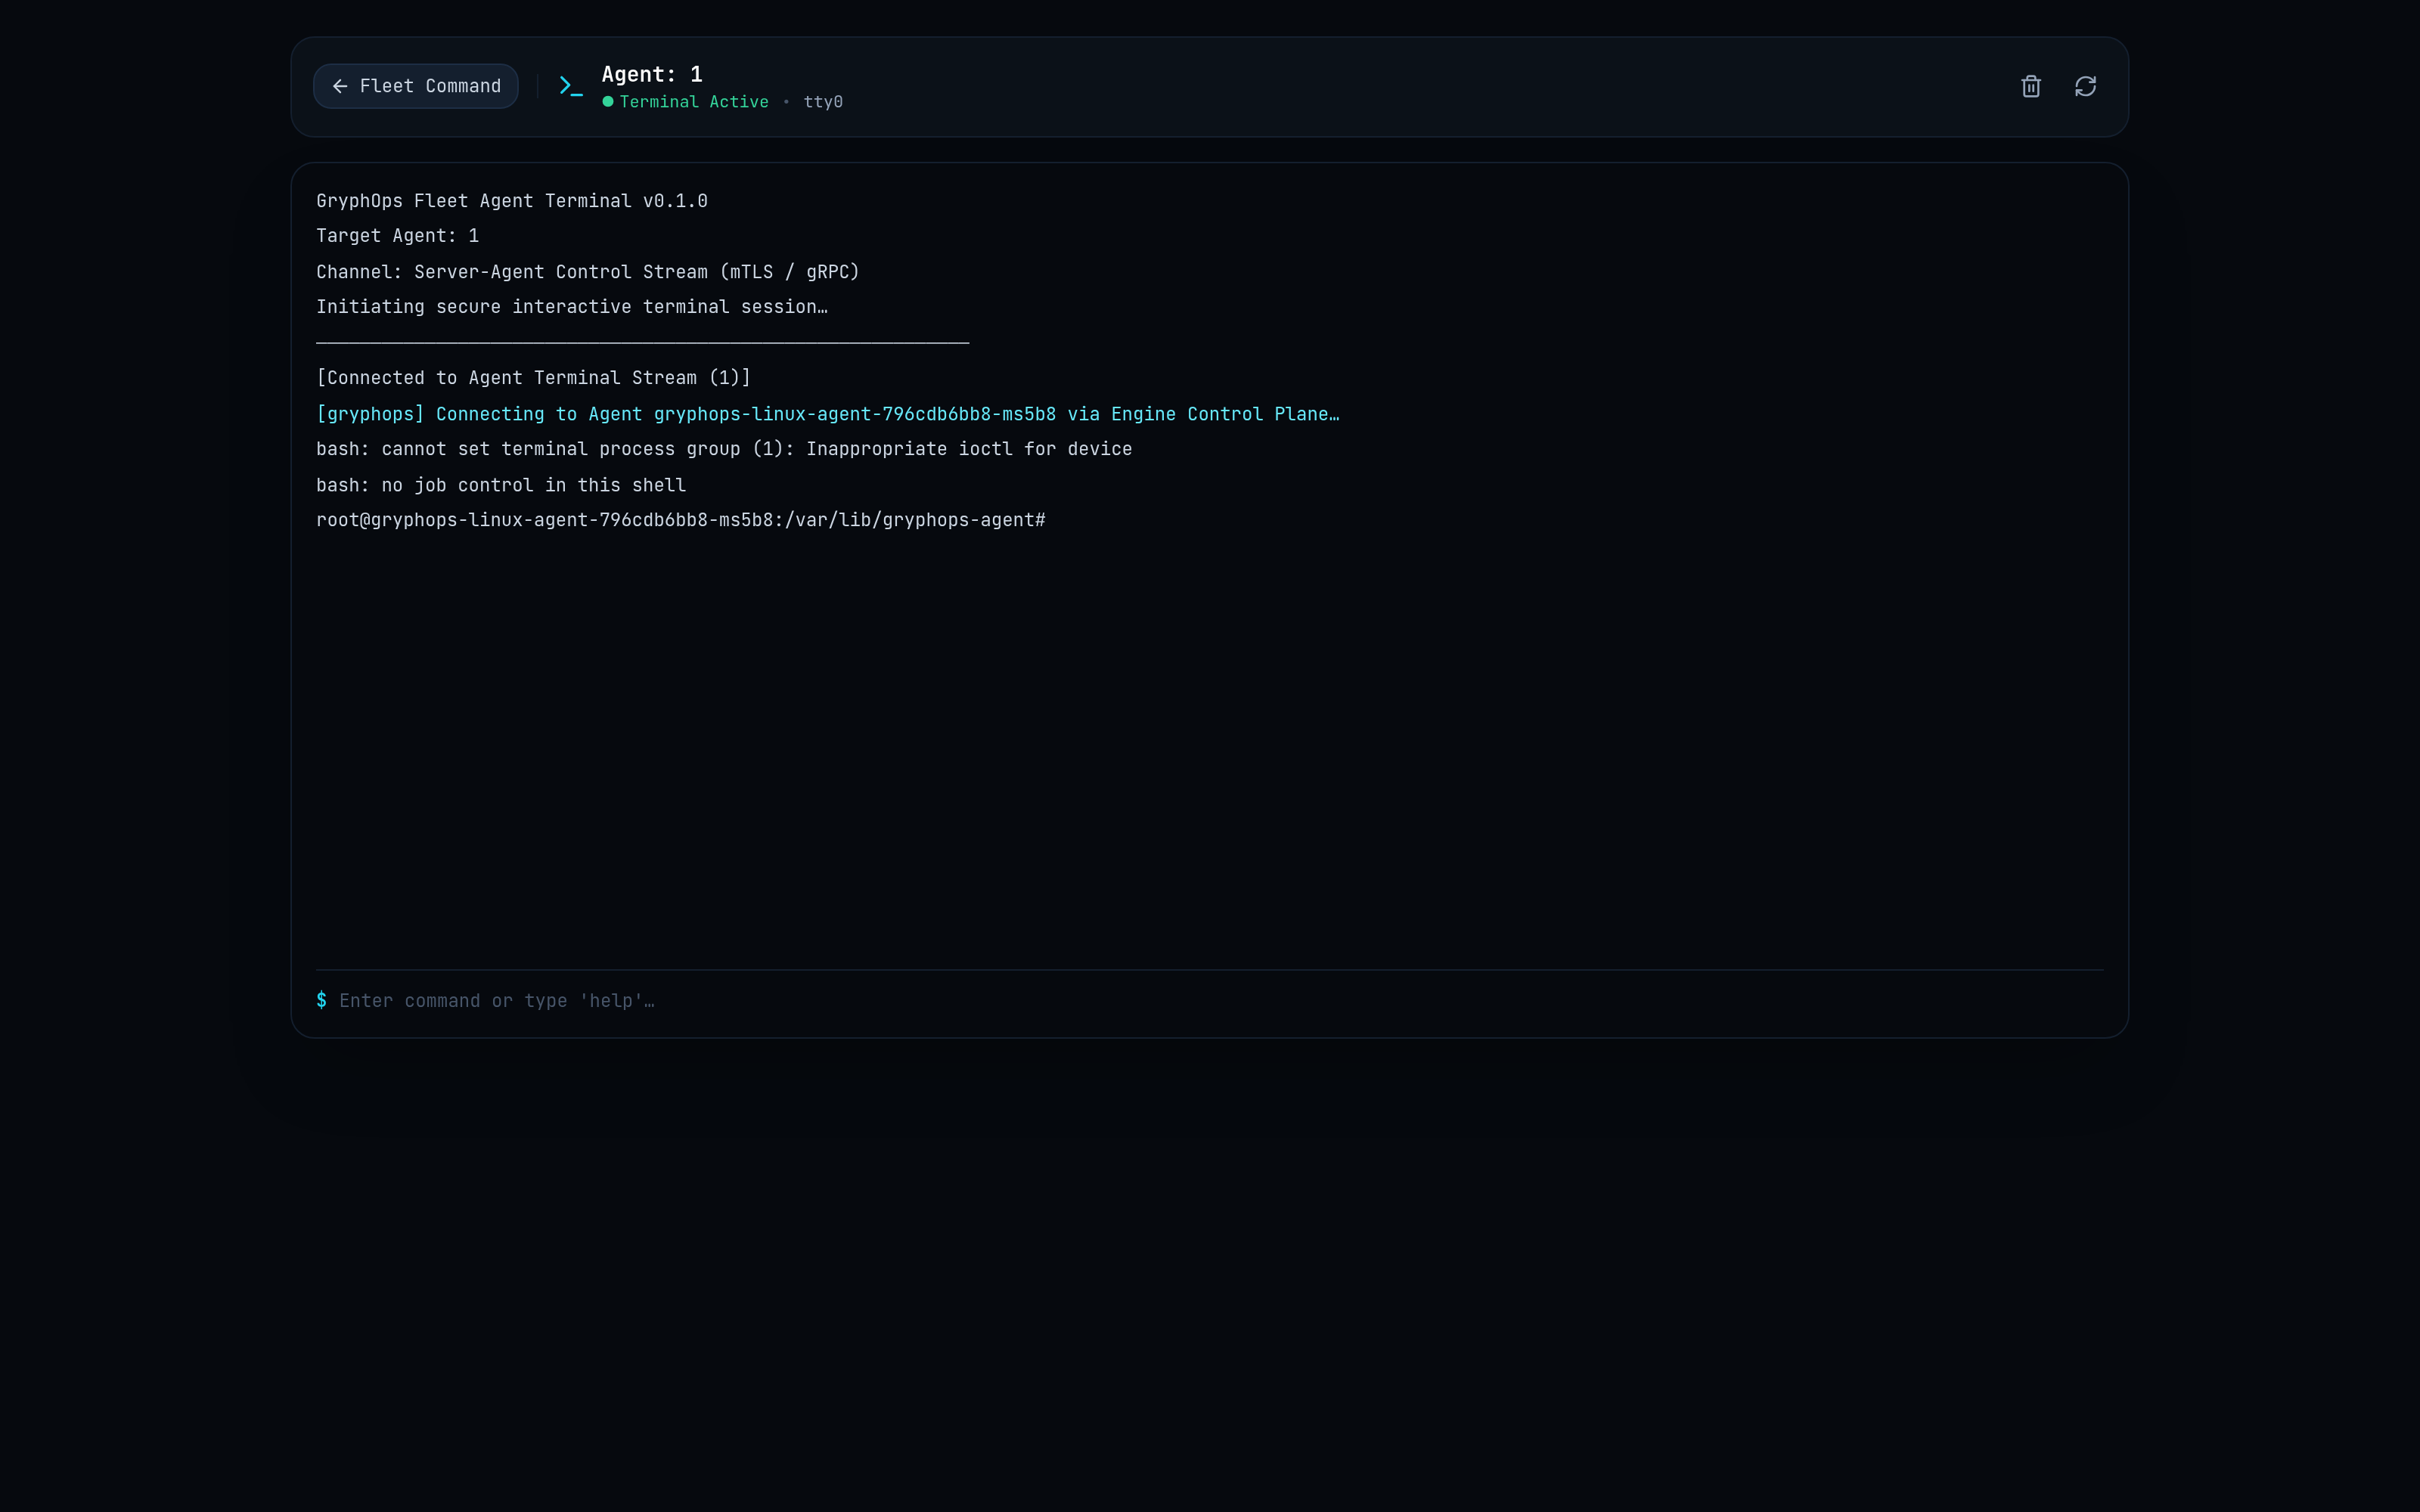
GryphOps Secure In-Browser Remote Terminal
Zero-Ingress Interactive Shell via WebSocket mTLS

Eliminate the need for exposed SSH ingress ports or jump boxes. Security operators and incident responders can establish an authenticated, encrypted, low-latency pseudo-terminal session directly into any enrolled fleet agent right from their browser, complete with full ANSI terminal emulation and session audit logging.

Zero Ingress PortsWebSocket MultiplexingANSI PTY TerminalSession Auditing
KEY CAPABILITIES & ARCHITECTURE
Zero open incoming firewall ports on managed endpoints
Direct WebSocket multiplexing over existing mTLS tunnel
Full interactive PTY support with terminal resize handling
Tamper-evident NIST AU audit trail of all executed commands
GryphOps 1-Command Helm Kubernetes Deployment
1-Command Sovereign Kubernetes Deployment & Quickstart Guides

Deploy the entire GryphOps platform into any air-gapped or multi-cloud Kubernetes cluster with a single Helm command. Built-in interactive quickstart guides provide copy-paste bash snippets for agent enrollment, token provisioning, and sensor validation.

Helm v3 ChartKinD & Production k8sEnvoy GatewayAir-Gap Containers
KEY CAPABILITIES & ARCHITECTURE
Single-command Helm deployment for vanilla or KinD k8s
Full air-gap compliance with self-contained container images
Automated Envoy Gateway & cert-manager TLS provisioning
Built-in SDK snippets for automated agent deployment
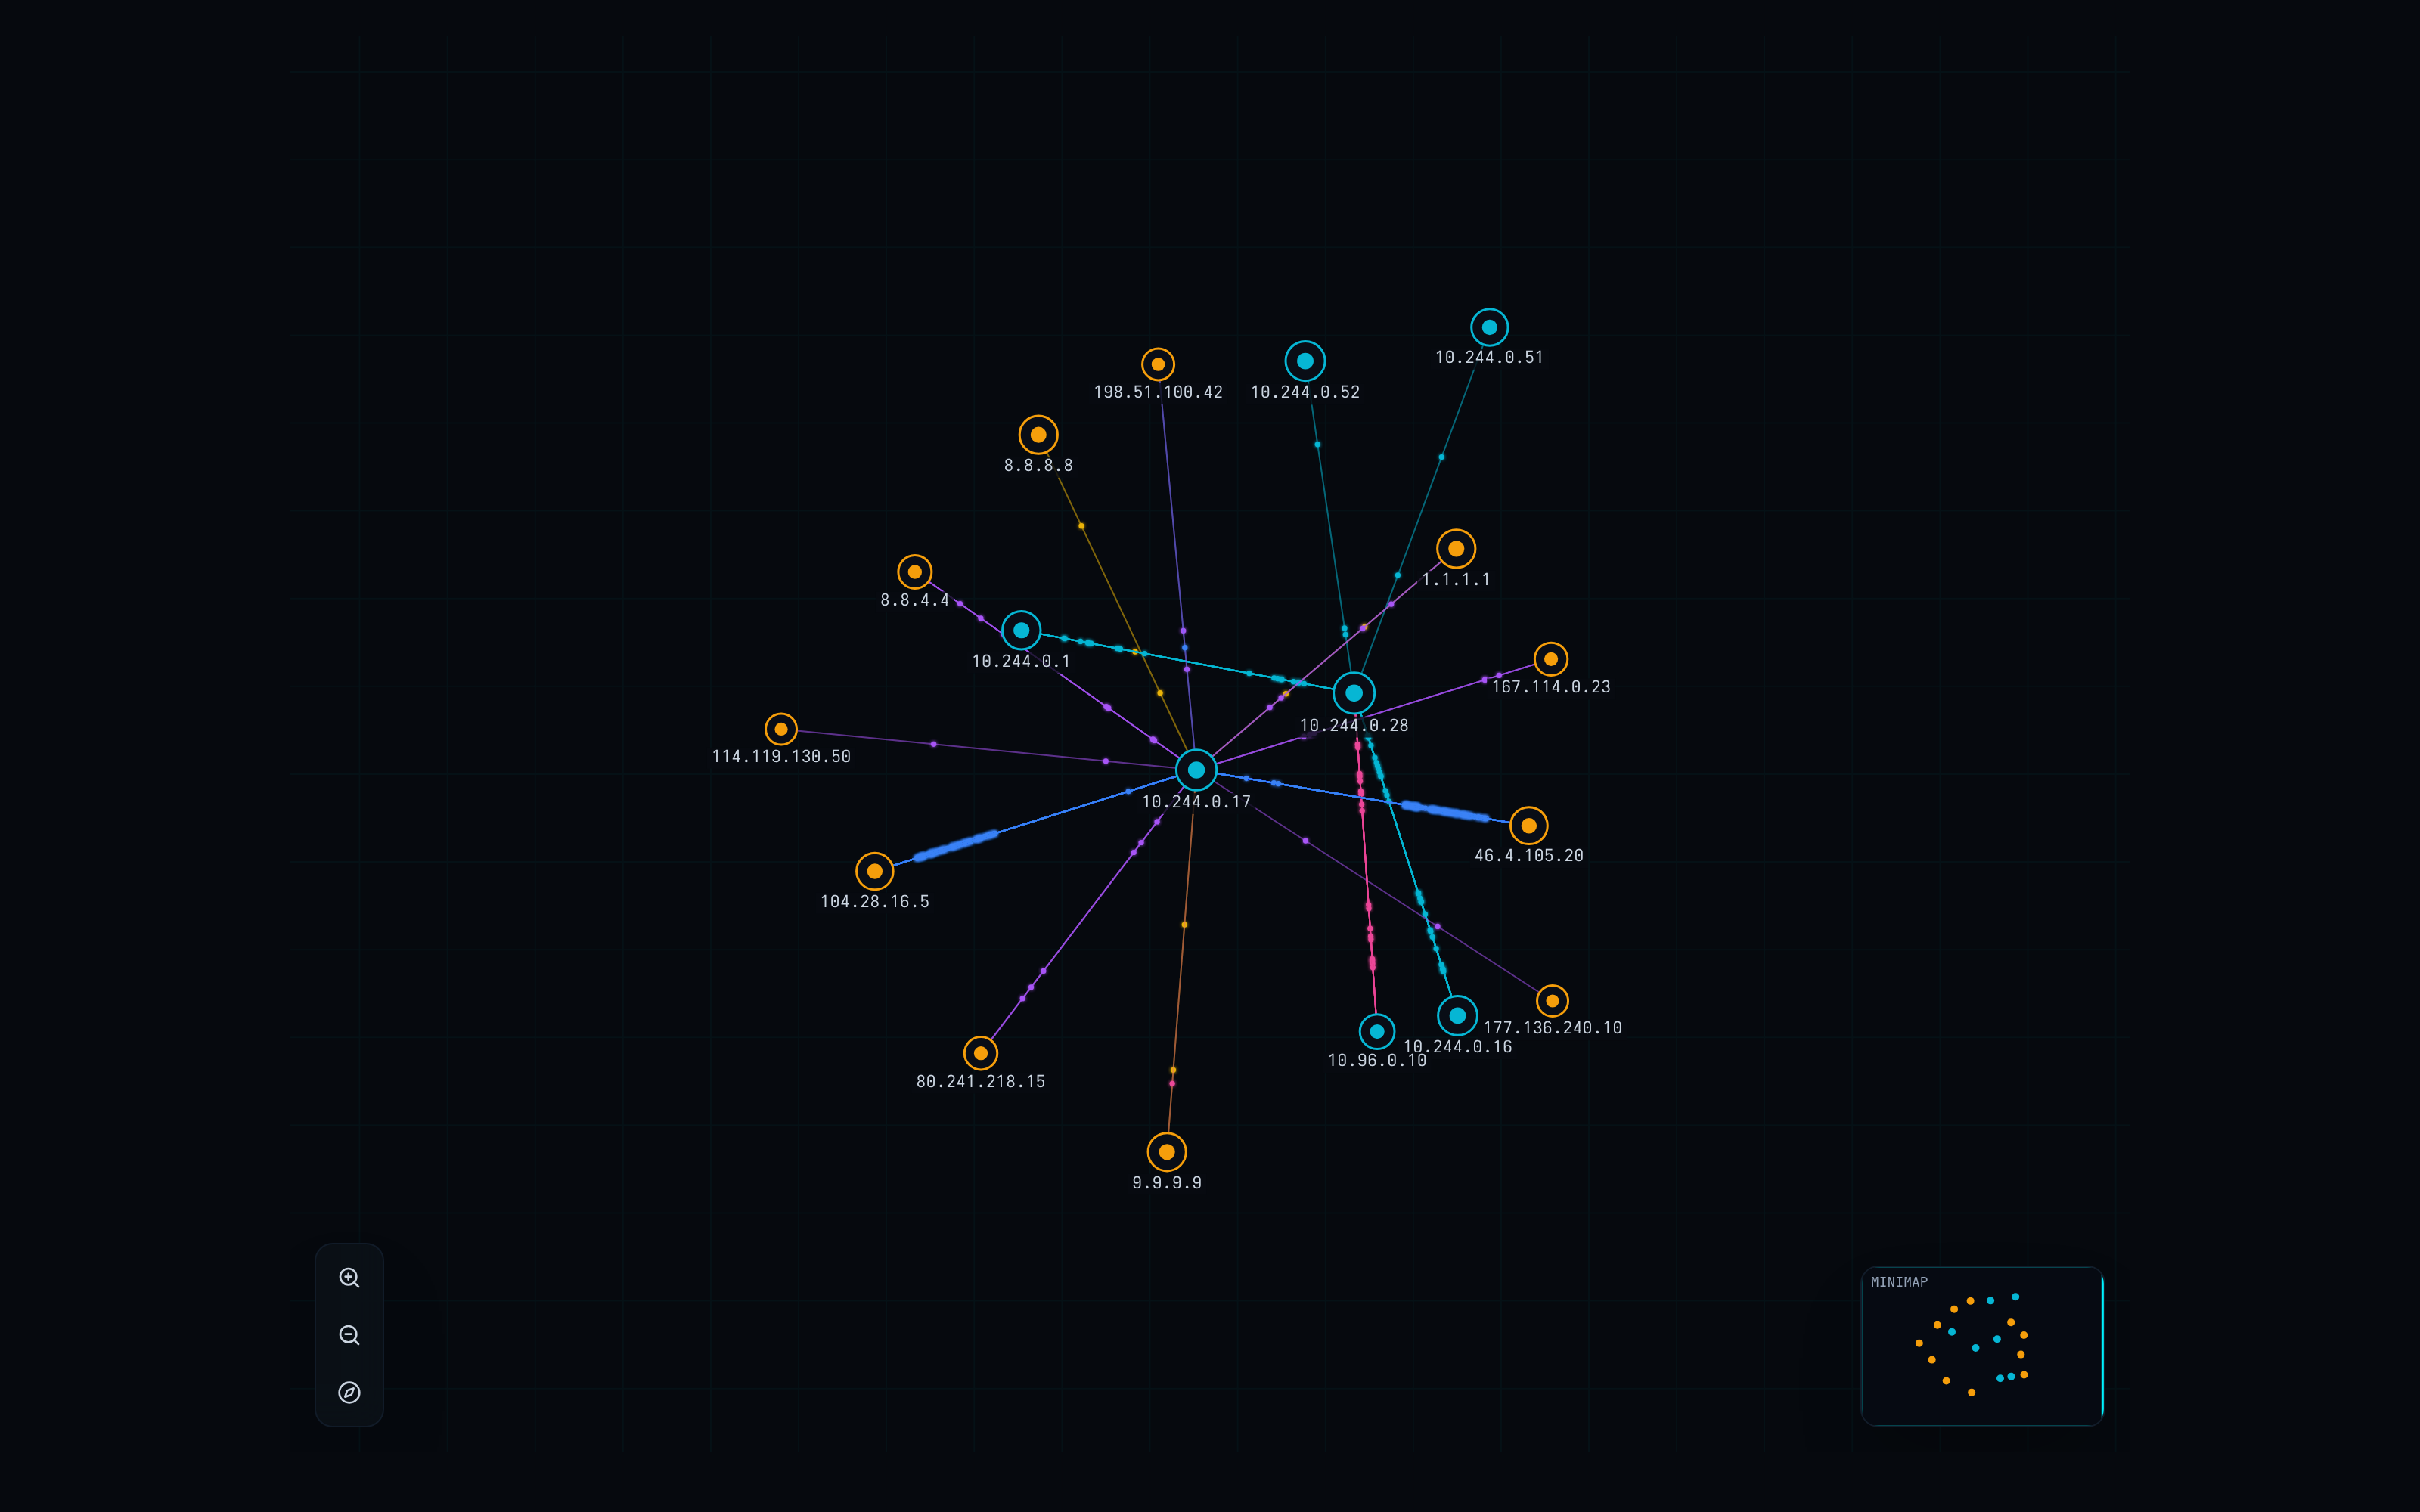
GryphOps Force-Directed Wire Topology Map
Force-Directed Graph Physics & Live Packet Particle Simulation

Visualize the entire network mesh in real-time with 60 FPS force-directed physics. Glowing particle animations illustrate packet volume, protocol velocity, and directional flows between subnets, endpoints, and external gateways. Zoom from high-level enterprise enclaves down into single socket connections.

60 FPS Canvas PhysicsSubnet ClusteringParticle Flow VectorsMinimap Navigation
KEY CAPABILITIES & ARCHITECTURE
D3 force-directed physics with automatic subnet clustering
Real-time particle flow rate proportional to packet volume
Interactive minimap, pan/zoom, and node inspect controls
Instant drilldown into TCP stream reassembly & host endpoints
GryphOps Network Analysis and Wire Forensics Console UI
Integrated Wire Tools UI: PCAP, Zeek, Suricata, Snort 3, Arkime, Sigma & YARA

Proprietary network sensor and wire forensics unified in one sovereign interface. Operators can seamlessly switch between live forensic consoles: PCAP Analyzer frame decoders, Zeek NSM transaction logs, Suricata intrusion alert streams, Snort 3 sticky buffer inspectors, Arkime session profilers, Sigma & JA4+ fingerprint classifiers, and the YARA hex payload viewer.

PCAP Frame TreeZeek NSM StudioSuricata Alert StreamSnort 3 Network SensorArkime SPI ProfilerJA4+ Fingerprint GridYARA Hex Viewer
KEY CAPABILITIES & ARCHITECTURE
Integrated operator consoles: PCAP, Zeek, Suricata, Snort 3, Arkime, Sigma & YARA
Interactive frame dissection tree & bidirectional TCP stream reassembly
Faceted SPI session graphs with 1-click raw PCAP slice exporting
In-browser dual-pane hex & ASCII wire payload viewer with MITRE ATT&CK mapping
INTEGRATED WIRE TOOLS UISelect any tool below to inspect its live operator interface & forensic workspace:
PACKET DISSECTION & STREAM REASSEMBLY

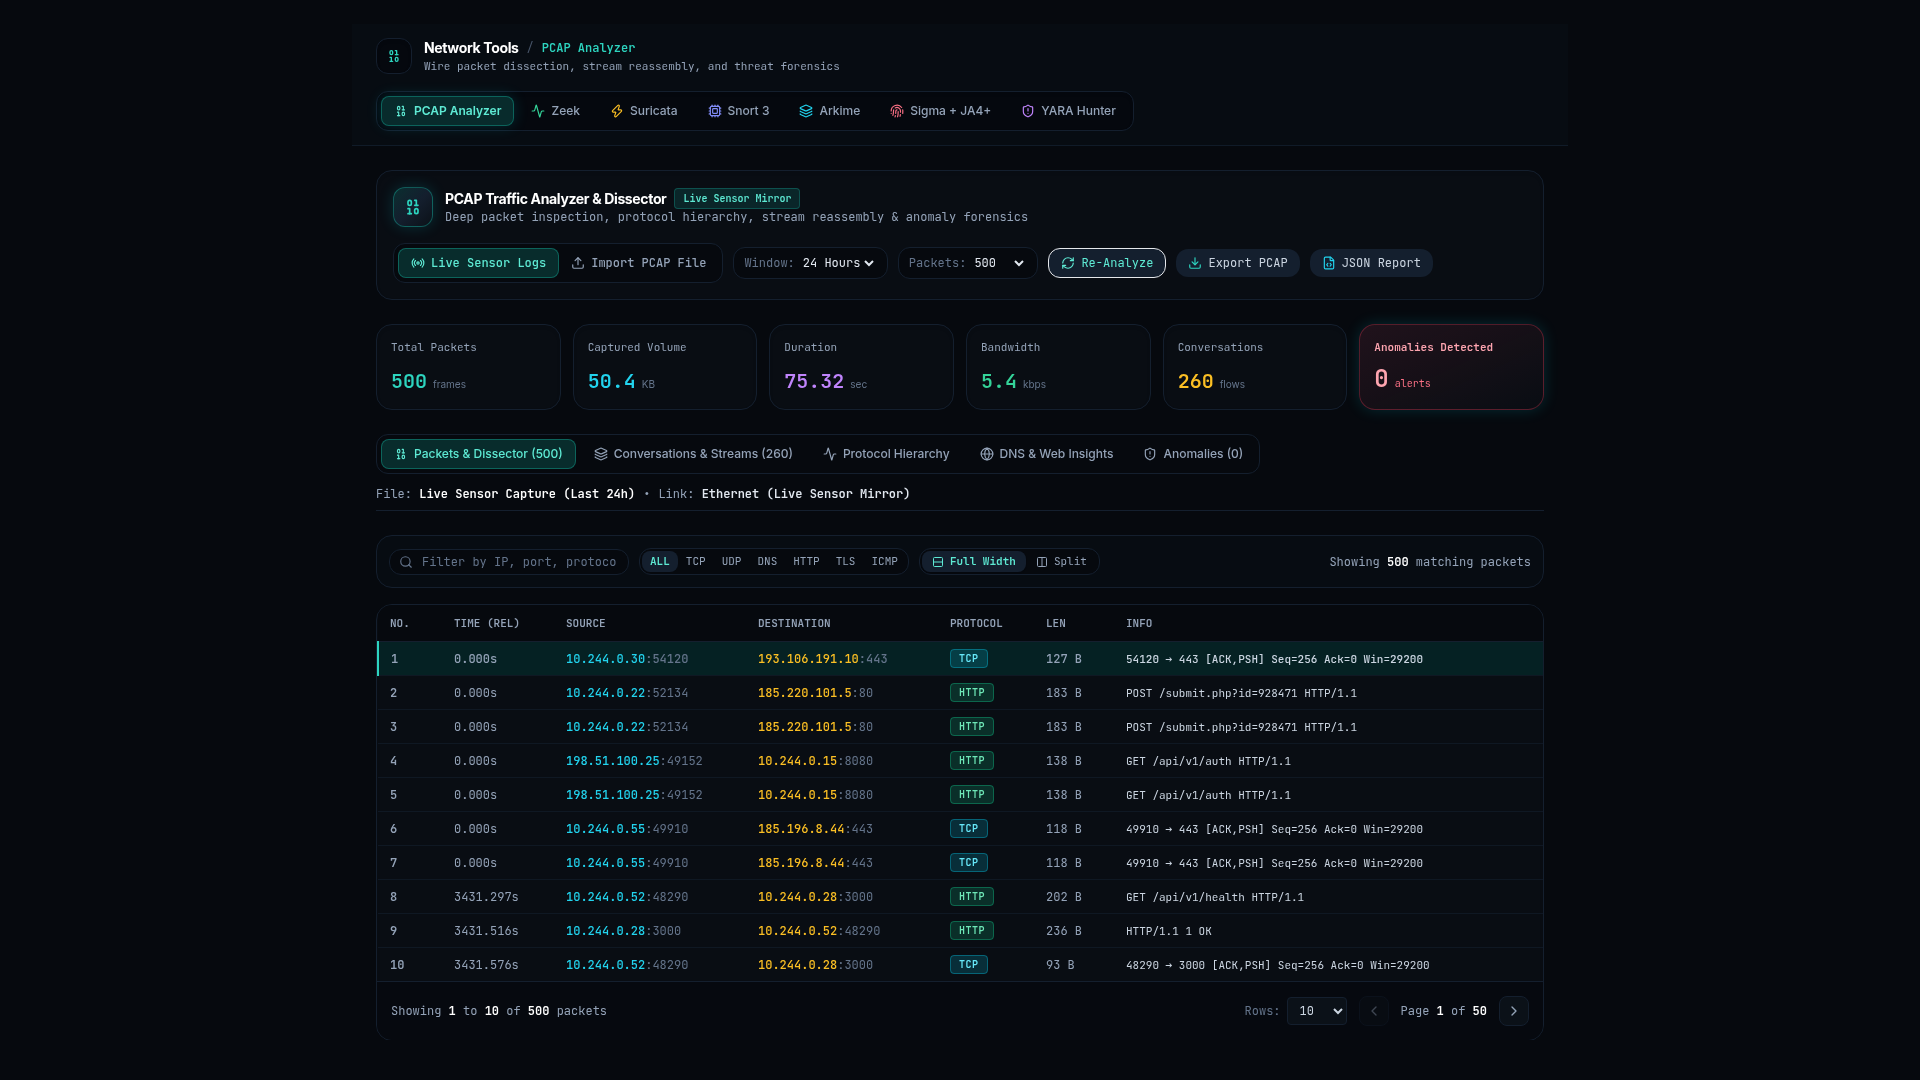
PCAP Analyzer

IN-TOOL WORKSPACE

The in-tool PCAP Analyzer interface provides full line-rate packet dissection directly within your browser. Analysts can inspect protocol decoders, reassemble TCP conversations, view byte-level payload streams, and analyze packet timing histograms without exporting captures to external tools.

GRYPHOPS // PCAP ANALYZER // LIVE OPERATOR UIPCAP Analyzer
GryphOps PCAP Analyzer In-Tool UI
Protocol Dissection Tree

Hierarchical decode tree displaying Ethernet frame headers, IPv4/IPv6 options, TCP flags, sequence numbers, and application payload segments.

TCP Stream Reassembly Pane

Reconstructs complete bidirectional conversations between endpoints with millisecond packet delta timing and payload flow directions.

Shannon Entropy Meter

Visual color-coded entropy gauge (0.0 to 8.0) pinpointing encrypted, compressed, or packed executable malware payloads in real time.

Wire-to-Host Causal Pivot

Single-click operator pivot button linking any network frame directly to the responsible host process PID, executable path, and user session.

Frame Tree DecoderTCP Stream ReassemblyPayload Hex/ASCII ViewerShannon Entropy GaugeBPF Ingestion Filter
TRANSACTION LOGS & NOTICES

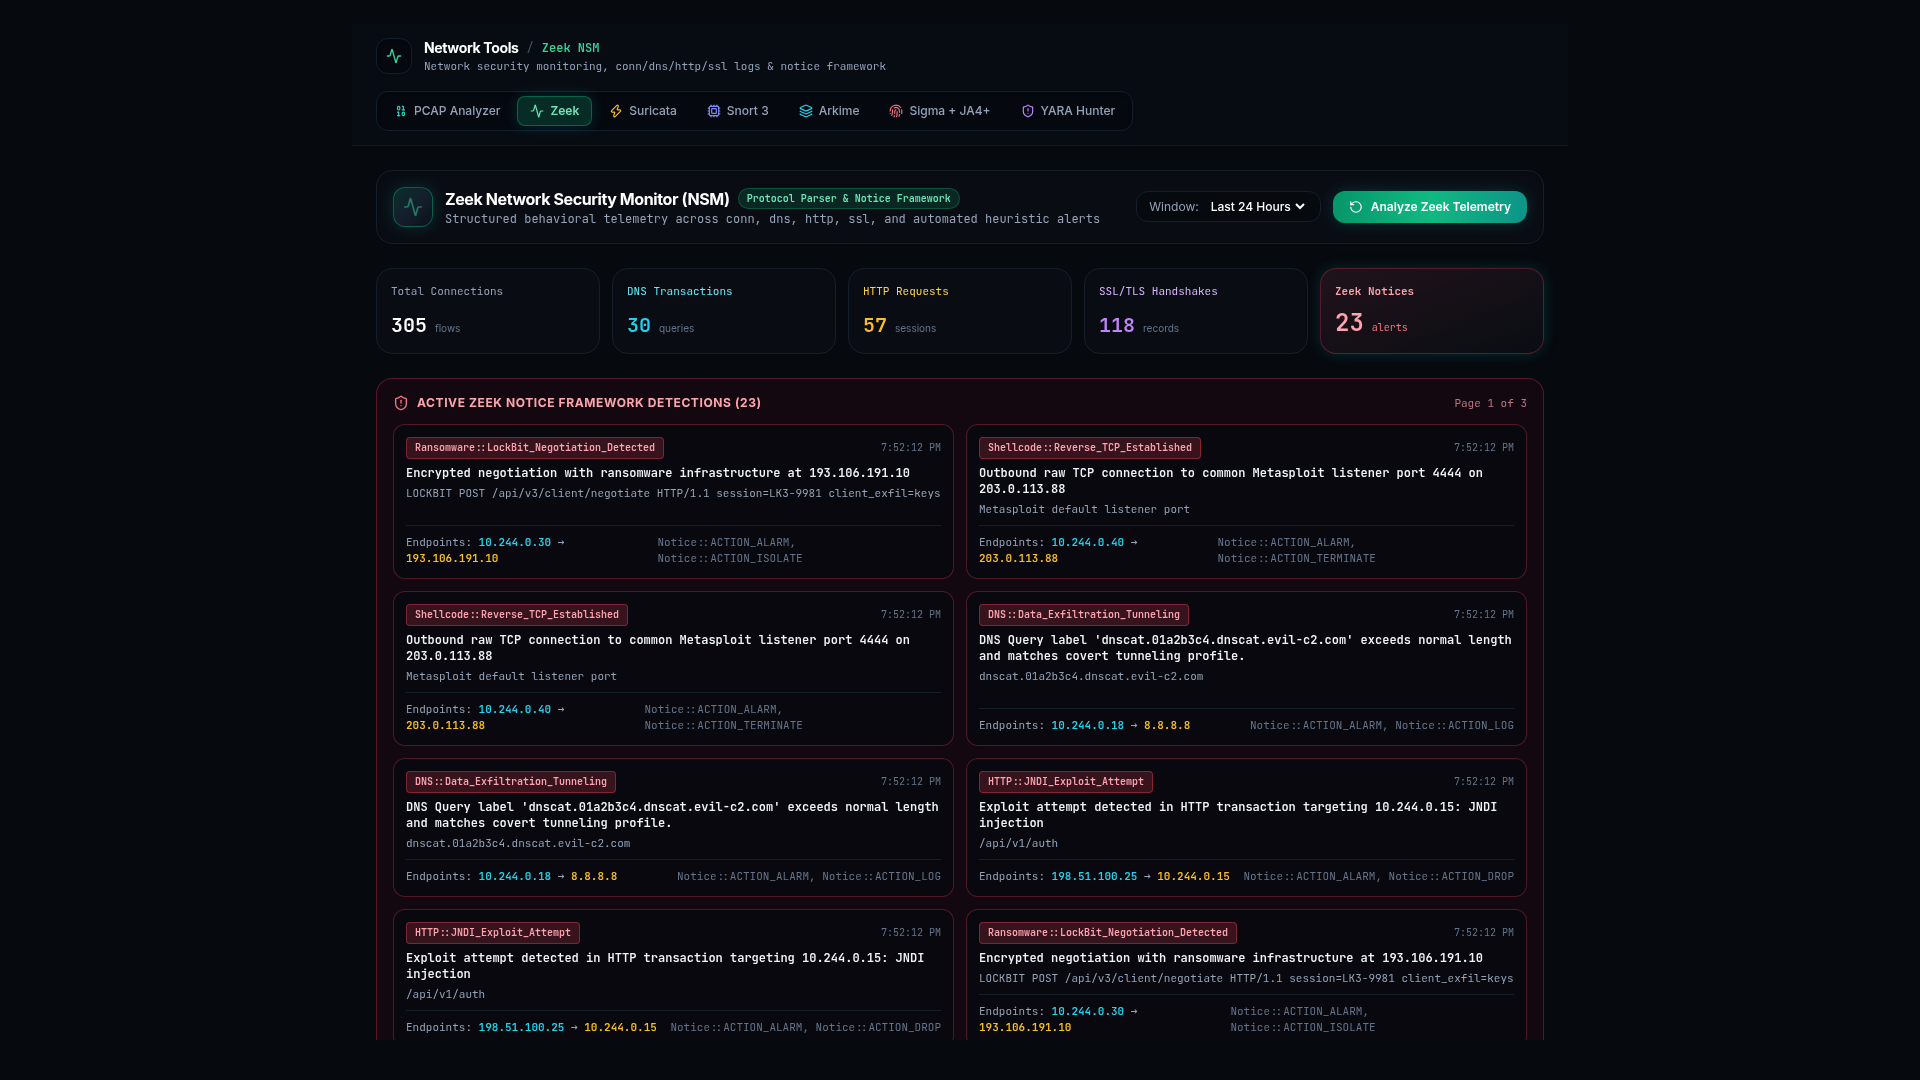
Zeek Network Security Monitor

IN-TOOL WORKSPACE

The Zeek NSM studio presents structured network transactions in high-performance operational grids. Seamlessly switch between connection records, DNS lookups, HTTP transactions, SSL/TLS certificates, and automated security notices with instant search and filtering.

GRYPHOPS // ZEEK NETWORK SECURITY MONITOR // LIVE OPERATOR UIZeek NSM
GryphOps Zeek NSM In-Tool UI
Interactive Log Tabs

One-click tab switching between conn.log (flow records), dns.log (queries & responses), http.log (URIs & user agents), and ssl.log (certificates).

Notice Alert Banner

High-priority alert ribbon highlighting detected covert DNS tunnels, protocol violations, and abnormal connection volumes.

Stateful Connection Badges

Color-coded TCP connection status tags (SF Normal Close, S0 Syn Flood, REJ Rejected, RSTO Reset by Originator) for instant triage.

Fast Subnet & CIDR Filter

In-table search bar enabling instant filtering across originator IP, responder IP, port numbers, protocol types, and service names.

conn.log / dns.log TabsActive Notice RibbonStateful Conn BadgesSSL Certificate TreeCIDR Range Filtering
STATEFUL IDS ALERTS & RULES

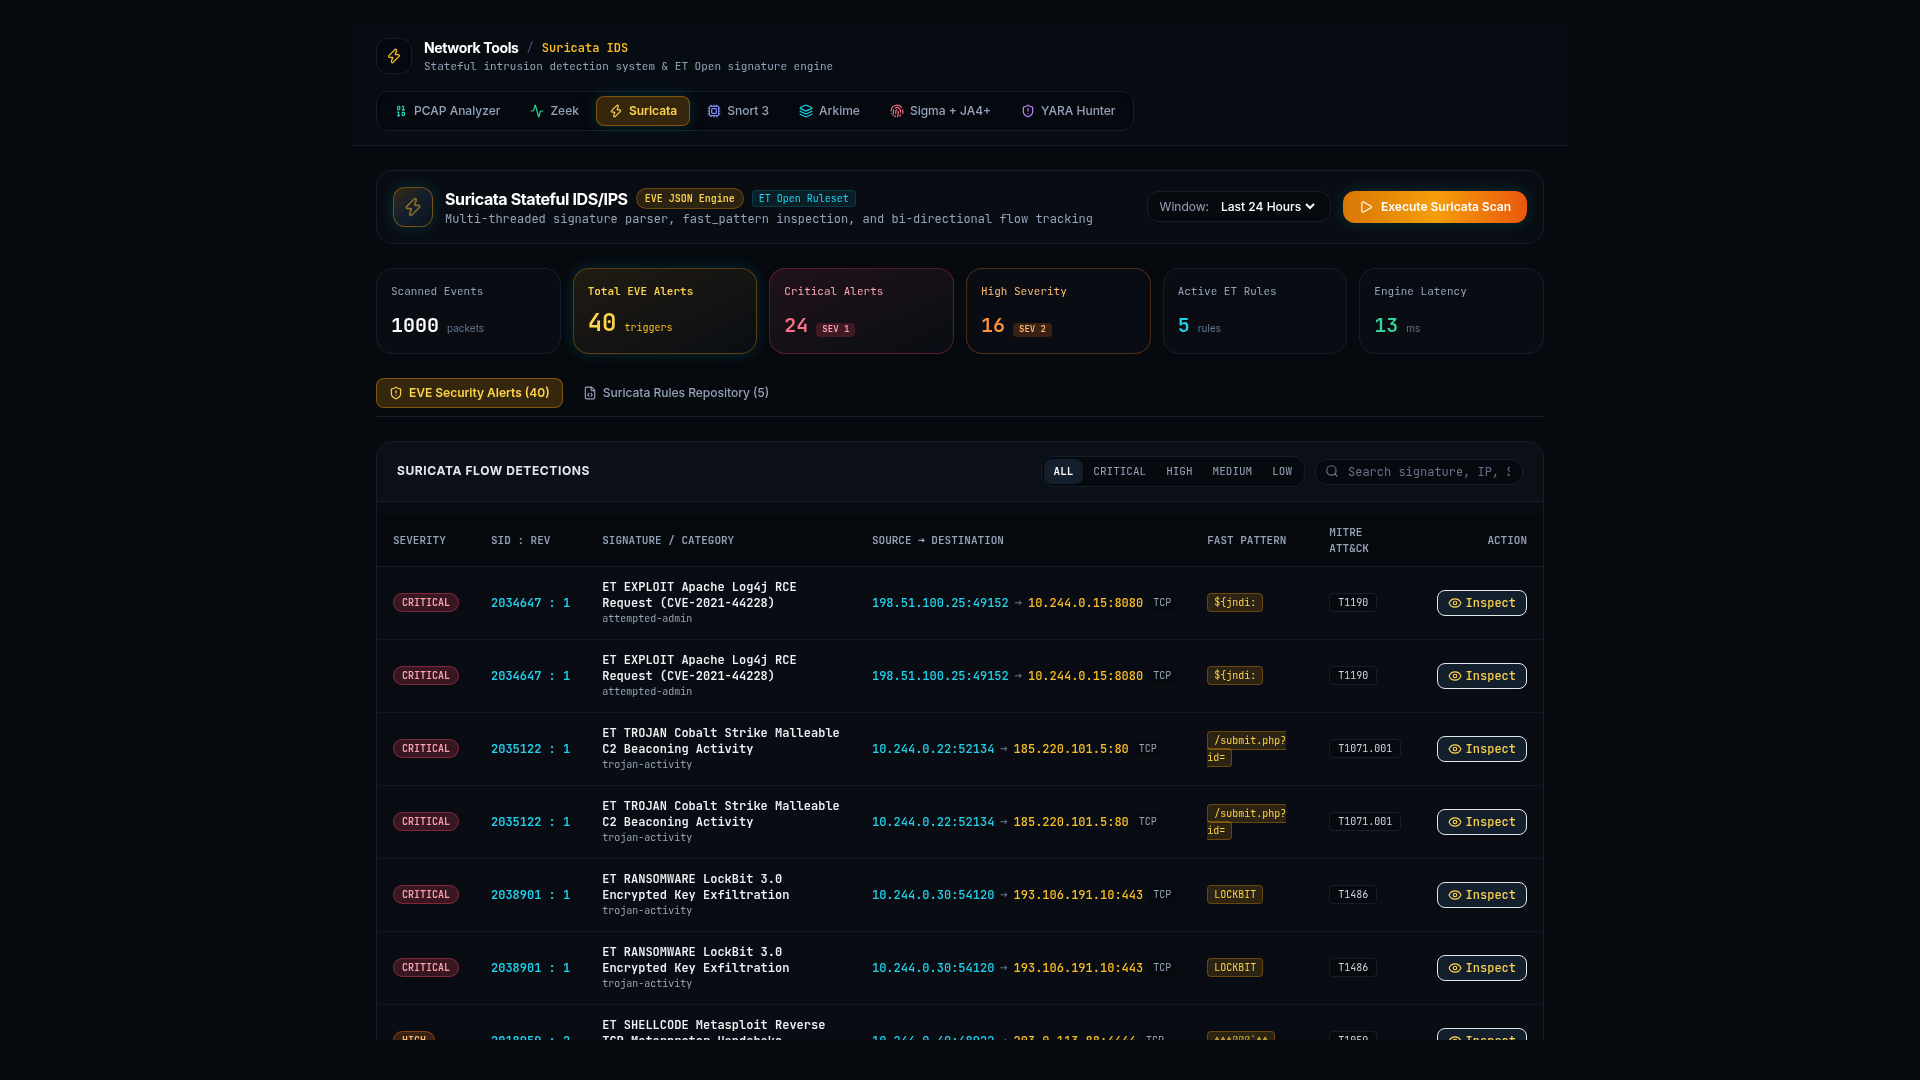
Suricata Stateful IDS/IPS

IN-TOOL WORKSPACE

The Suricata IDS dashboard displays real-time signature alerts from Emerging Threats (ET Open) rulesets. Security operators can triage alerts by severity, inspect packet payloads, browse the active rule repository, and monitor intrusion trends across all network segments.

GRYPHOPS // SURICATA STATEFUL IDS/IPS // LIVE OPERATOR UISuricata IDS
GryphOps Suricata Stateful IDS In-Tool UI
Live Alert Stream Grid

Interactive alert table displaying signature descriptions, SID identifiers, source/destination endpoints, and MITRE technique classifications.

Severity & Classtype Tags

Color-coded severity indicators (Critical, High, Medium, Low) with classification tags such as attempted-admin, trojan-activity, and web-application-attack.

Rule Catalog Browser

Built-in rule manager allowing operators to search active rules, review revision history, and check matching statistics.

Deep Payload Inspector Drawer

Slide-out inspection drawer displaying raw matched packet bytes and flow state metadata with one-click drilldown into raw wire captures.

Live Alert TableET Open Rule CatalogSeverity Status PillsMITRE Technique TagsPayload Inspect Drawer
NEXT-GEN STICKY BUFFERS

Snort 3 Network Sensor

IN-TOOL WORKSPACE

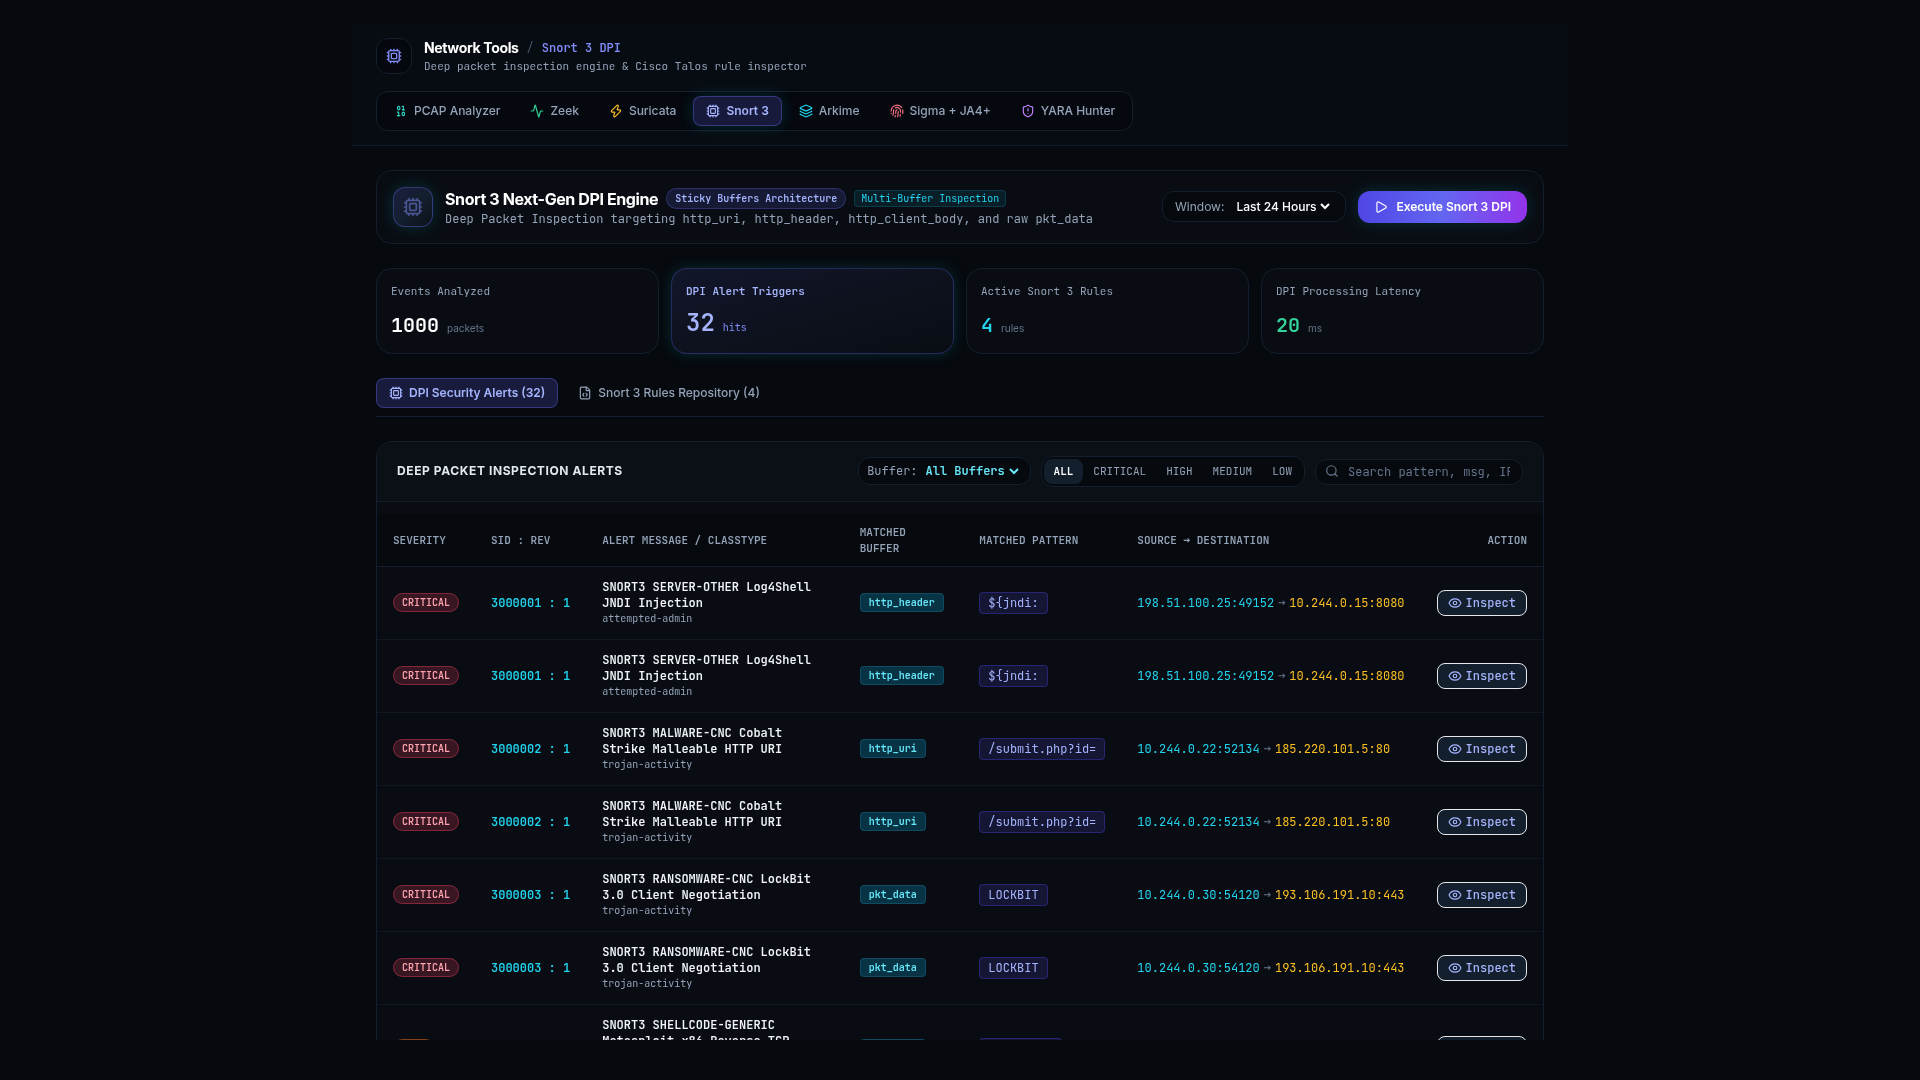
The Snort 3 Network Sensor interface showcases next-generation sticky buffer inspection results. Operators can examine matched protocol buffers (http_uri, http_header, http_client_body), verify Talos intrusion rules, and review enforced security actions.

GRYPHOPS // SNORT 3 NETWORK SENSOR // LIVE OPERATOR UISnort 3 Sensor
GryphOps Snort 3 Network Sensor In-Tool UI
Sticky Buffer Indicator Badges

Visual chips showing which exact protocol buffer triggered detection (http_uri, http_header, client_body) for zero-ambiguity triage.

Enforcement Action Badges

Clear status badges showing action outcomes (Alert, Drop, Pass, Reject) based on the active inline IPS security profile.

Talos Rule Library Viewer

Searchable catalog of Cisco Talos signature definitions with category filters, SID search, and revision metadata.

Matched Event Context Cards

Detailed finding cards displaying packet arrival timestamps, source/destination IP pairs, protocol headers, and matched string offsets.

Sticky Buffer TagsTalos Rule BrowserEnforcement Action PillsFlow State TrackerEvent Context Cards
SESSION PROFILING & SPI SEARCH

Arkime SPI & Full-Packet Index

IN-TOOL WORKSPACE

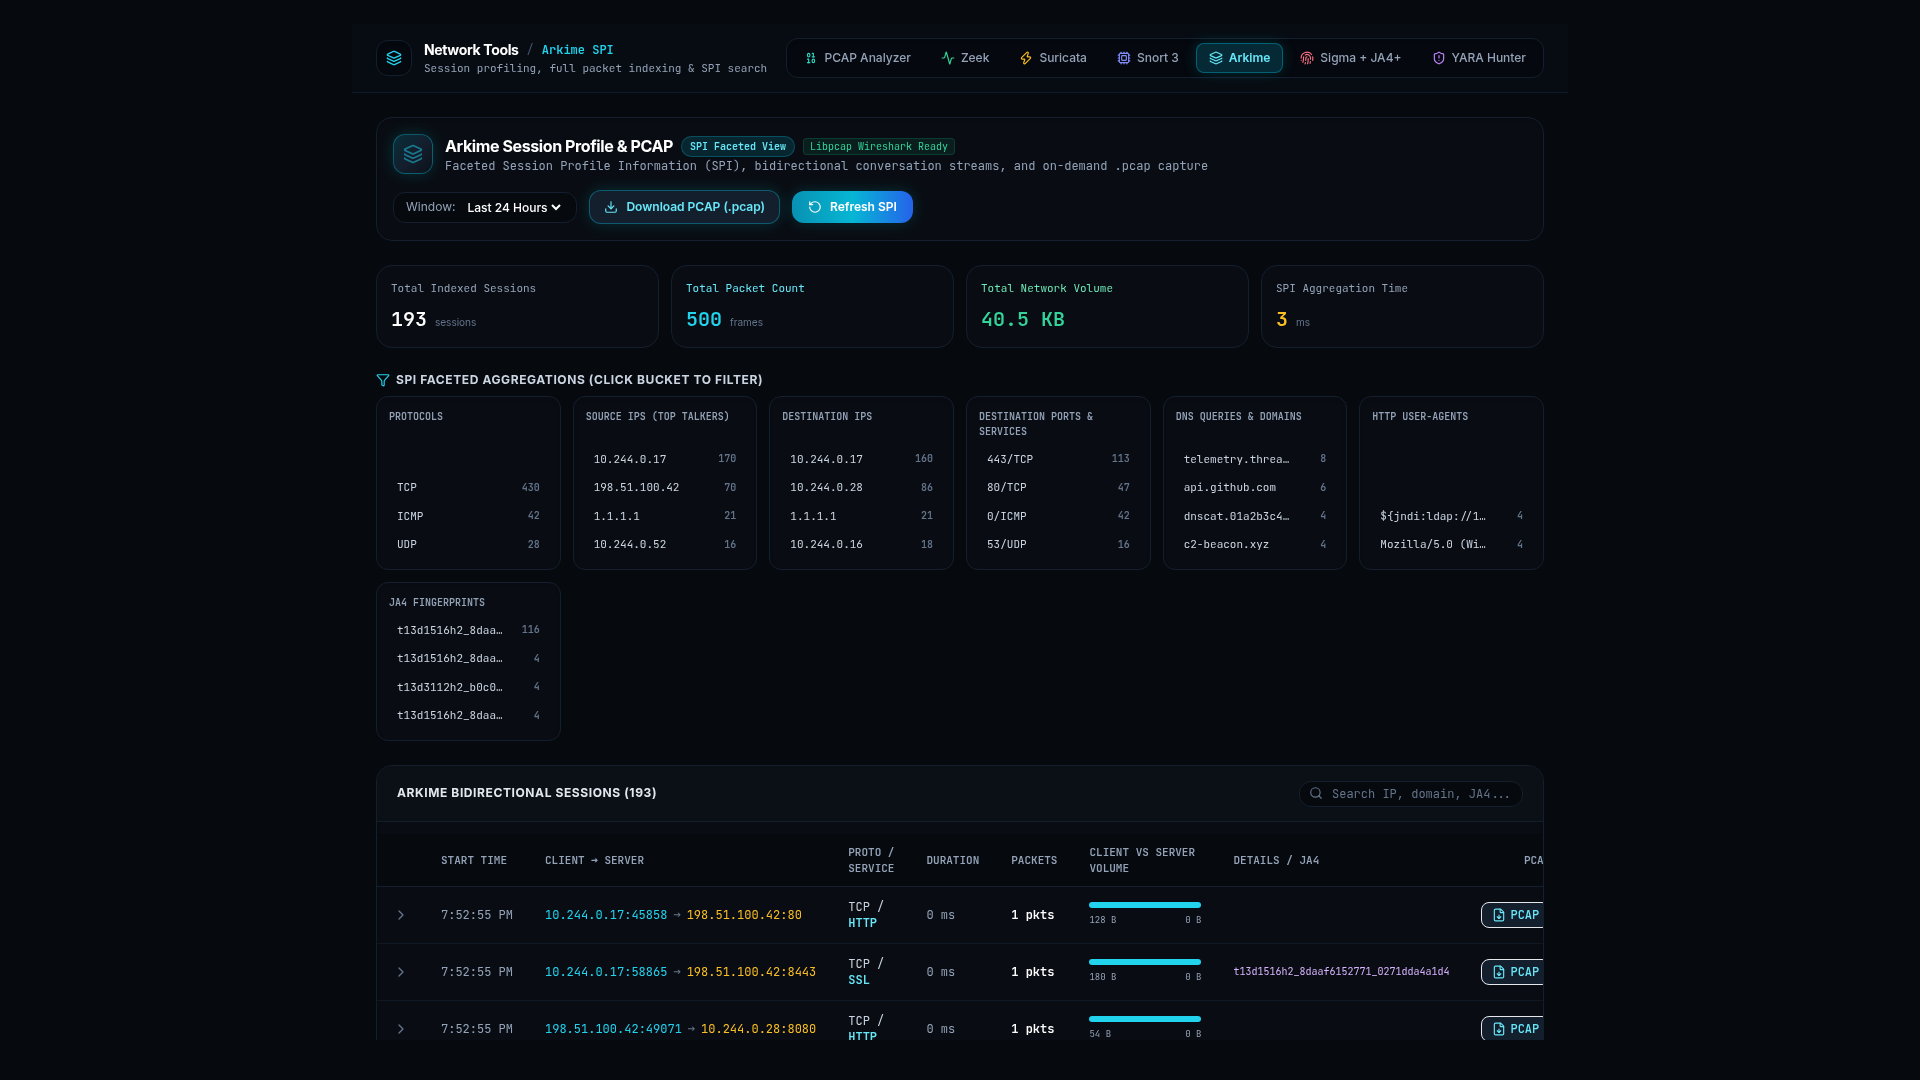
The Arkime SPI interface provides full-scale session indexing and packet search. Operators can analyze faceted protocol distributions, visualize network activity over time histograms, and download exact raw PCAP slices for forensic archiving.

GRYPHOPS // ARKIME SPI & FULL-PACKET INDEX // LIVE OPERATOR UIArkime SPI
GryphOps Arkime SPI Session Profiler In-Tool UI
Faceted SPI Search Interface

High-speed faceted aggregation panels breaking down active traffic by protocol, destination port, country code, and ASN.

Session Histogram & Timeline

Interactive time-scrubbing packet volume histogram displaying traffic bursts, protocol shifts, and communication spikes.

1-Click Raw PCAP Export

Instant download button extracting exact reconstructed PCAP segments directly to the analyst's workstation for offline analysis.

Session Stream Viewer

Color-coded dual-direction stream viewer displaying client requests in blue and server responses in green with full metadata headers.

Faceted SPI FacetsTimeline Histogram1-Click PCAP ExportStream Replay PaneGeo-IP / ASN Enrichment
BEHAVIORAL WIRE SIGNATURES

Sigma Rules & JA4+ Fingerprinting

IN-TOOL WORKSPACE

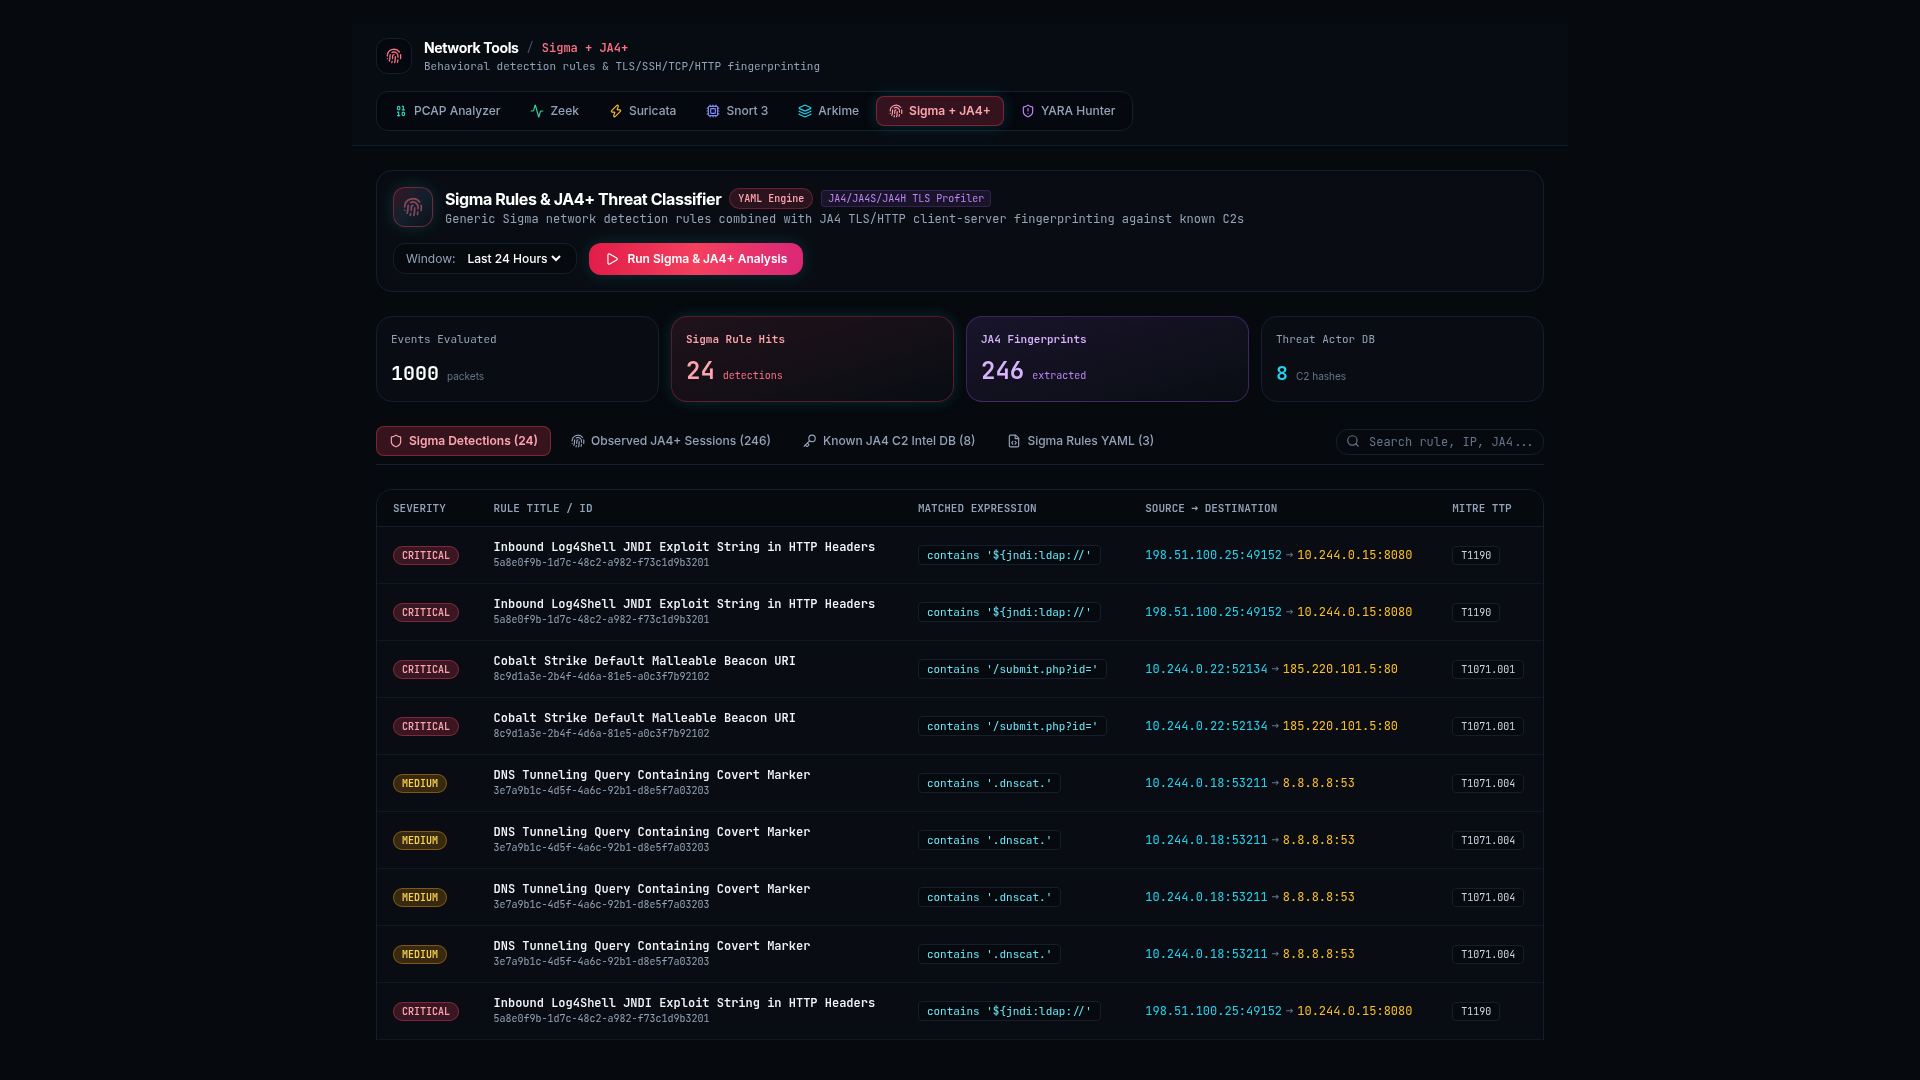
The Sigma + JA4+ studio unifies behavioral detection rules with cutting-edge network fingerprinting. The interface correlates client TLS/SSH handshakes against threat intelligence databases to detect Cobalt Strike, Metasploit, and custom implants even over encrypted channels.

GRYPHOPS // SIGMA RULES & JA4+ FINGERPRINTING // LIVE OPERATOR UISigma + JA4+
GryphOps Sigma Rules and JA4+ Fingerprinting In-Tool UI
JA4 Cryptographic Fingerprint Grid

Structured table displaying computed JA4 TLS, JA4S server, JA4H HTTP, and JA4SSH hashes with known application attribution.

Threat Attribution Cards

Visual malware identification cards mapping recognized fingerprints to threat actors, malware families, and confidence percentages.

Behavioral Rule Library

Catalog of open-standard Sigma rules for network telemetry with MITRE ATT&CK technique tags and automated detection toggles.

Encrypted C2 Channel Detector

Real-time indicator badges flagging known malicious TLS handshakes without requiring SSL/TLS decryption.

JA4/JA4S/JA4H TableMalware Attribution CardsBehavioral Match BadgesMITRE ATT&CK LinksConfidence Score Meters
PAYLOAD MALWARE SCANNER

YARA Wire Payload Hunter

IN-TOOL WORKSPACE

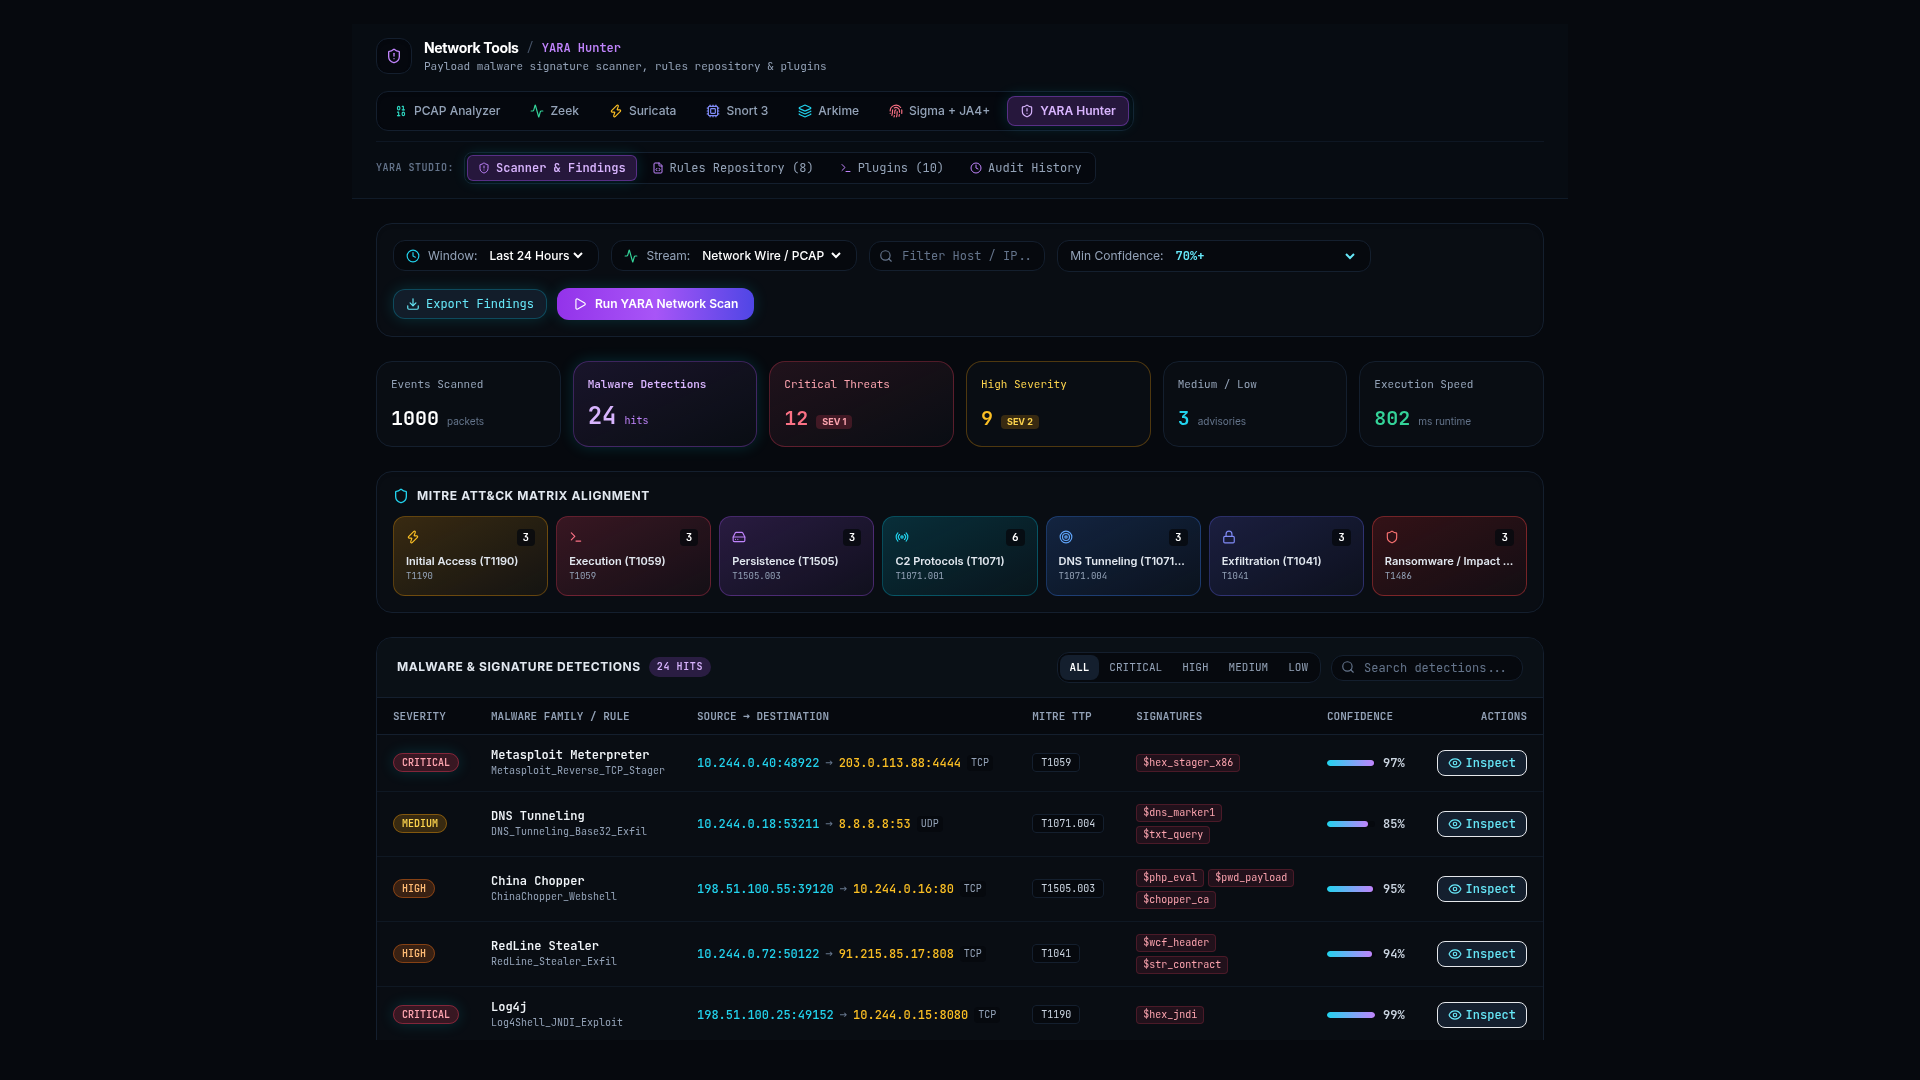
The YARA Hunter interface equips analysts with an in-browser hex payload viewer and live rule sandbox. Evaluate compiled signatures across wire streams, inspect malware byte patterns in hex/ASCII, and visualize tactical threat coverage on an integrated MITRE matrix.

GRYPHOPS // YARA WIRE PAYLOAD HUNTER // LIVE OPERATOR UIYARA Rules
GryphOps YARA Wire Payload Hunter In-Tool UI
Interactive Hex & ASCII Payload Viewer

Colorized byte-grid inspection tool displaying raw packet offsets, ASCII representations, and highlighted malware signature match regions.

MITRE ATT&CK Matrix Tactical Card

Visual tactical matrix mapping triggered YARA signatures directly to adversary tactics (C2, Exfiltration, Initial Access, Execution).

Rule Sandbox & Test Workbench

Interactive testing modal enabling analysts to validate custom signatures against sample packet buffers with instant detection feedback.

Payload Detection Scorecards

Summary scorecards displaying malware family names, rule confidence ratings, detection timestamps, and affected endpoints.

Interactive Hex ViewerMITRE ATT&CK Matrix CardRule Test SandboxMalware Family ScorecardsByte Offset Highlights
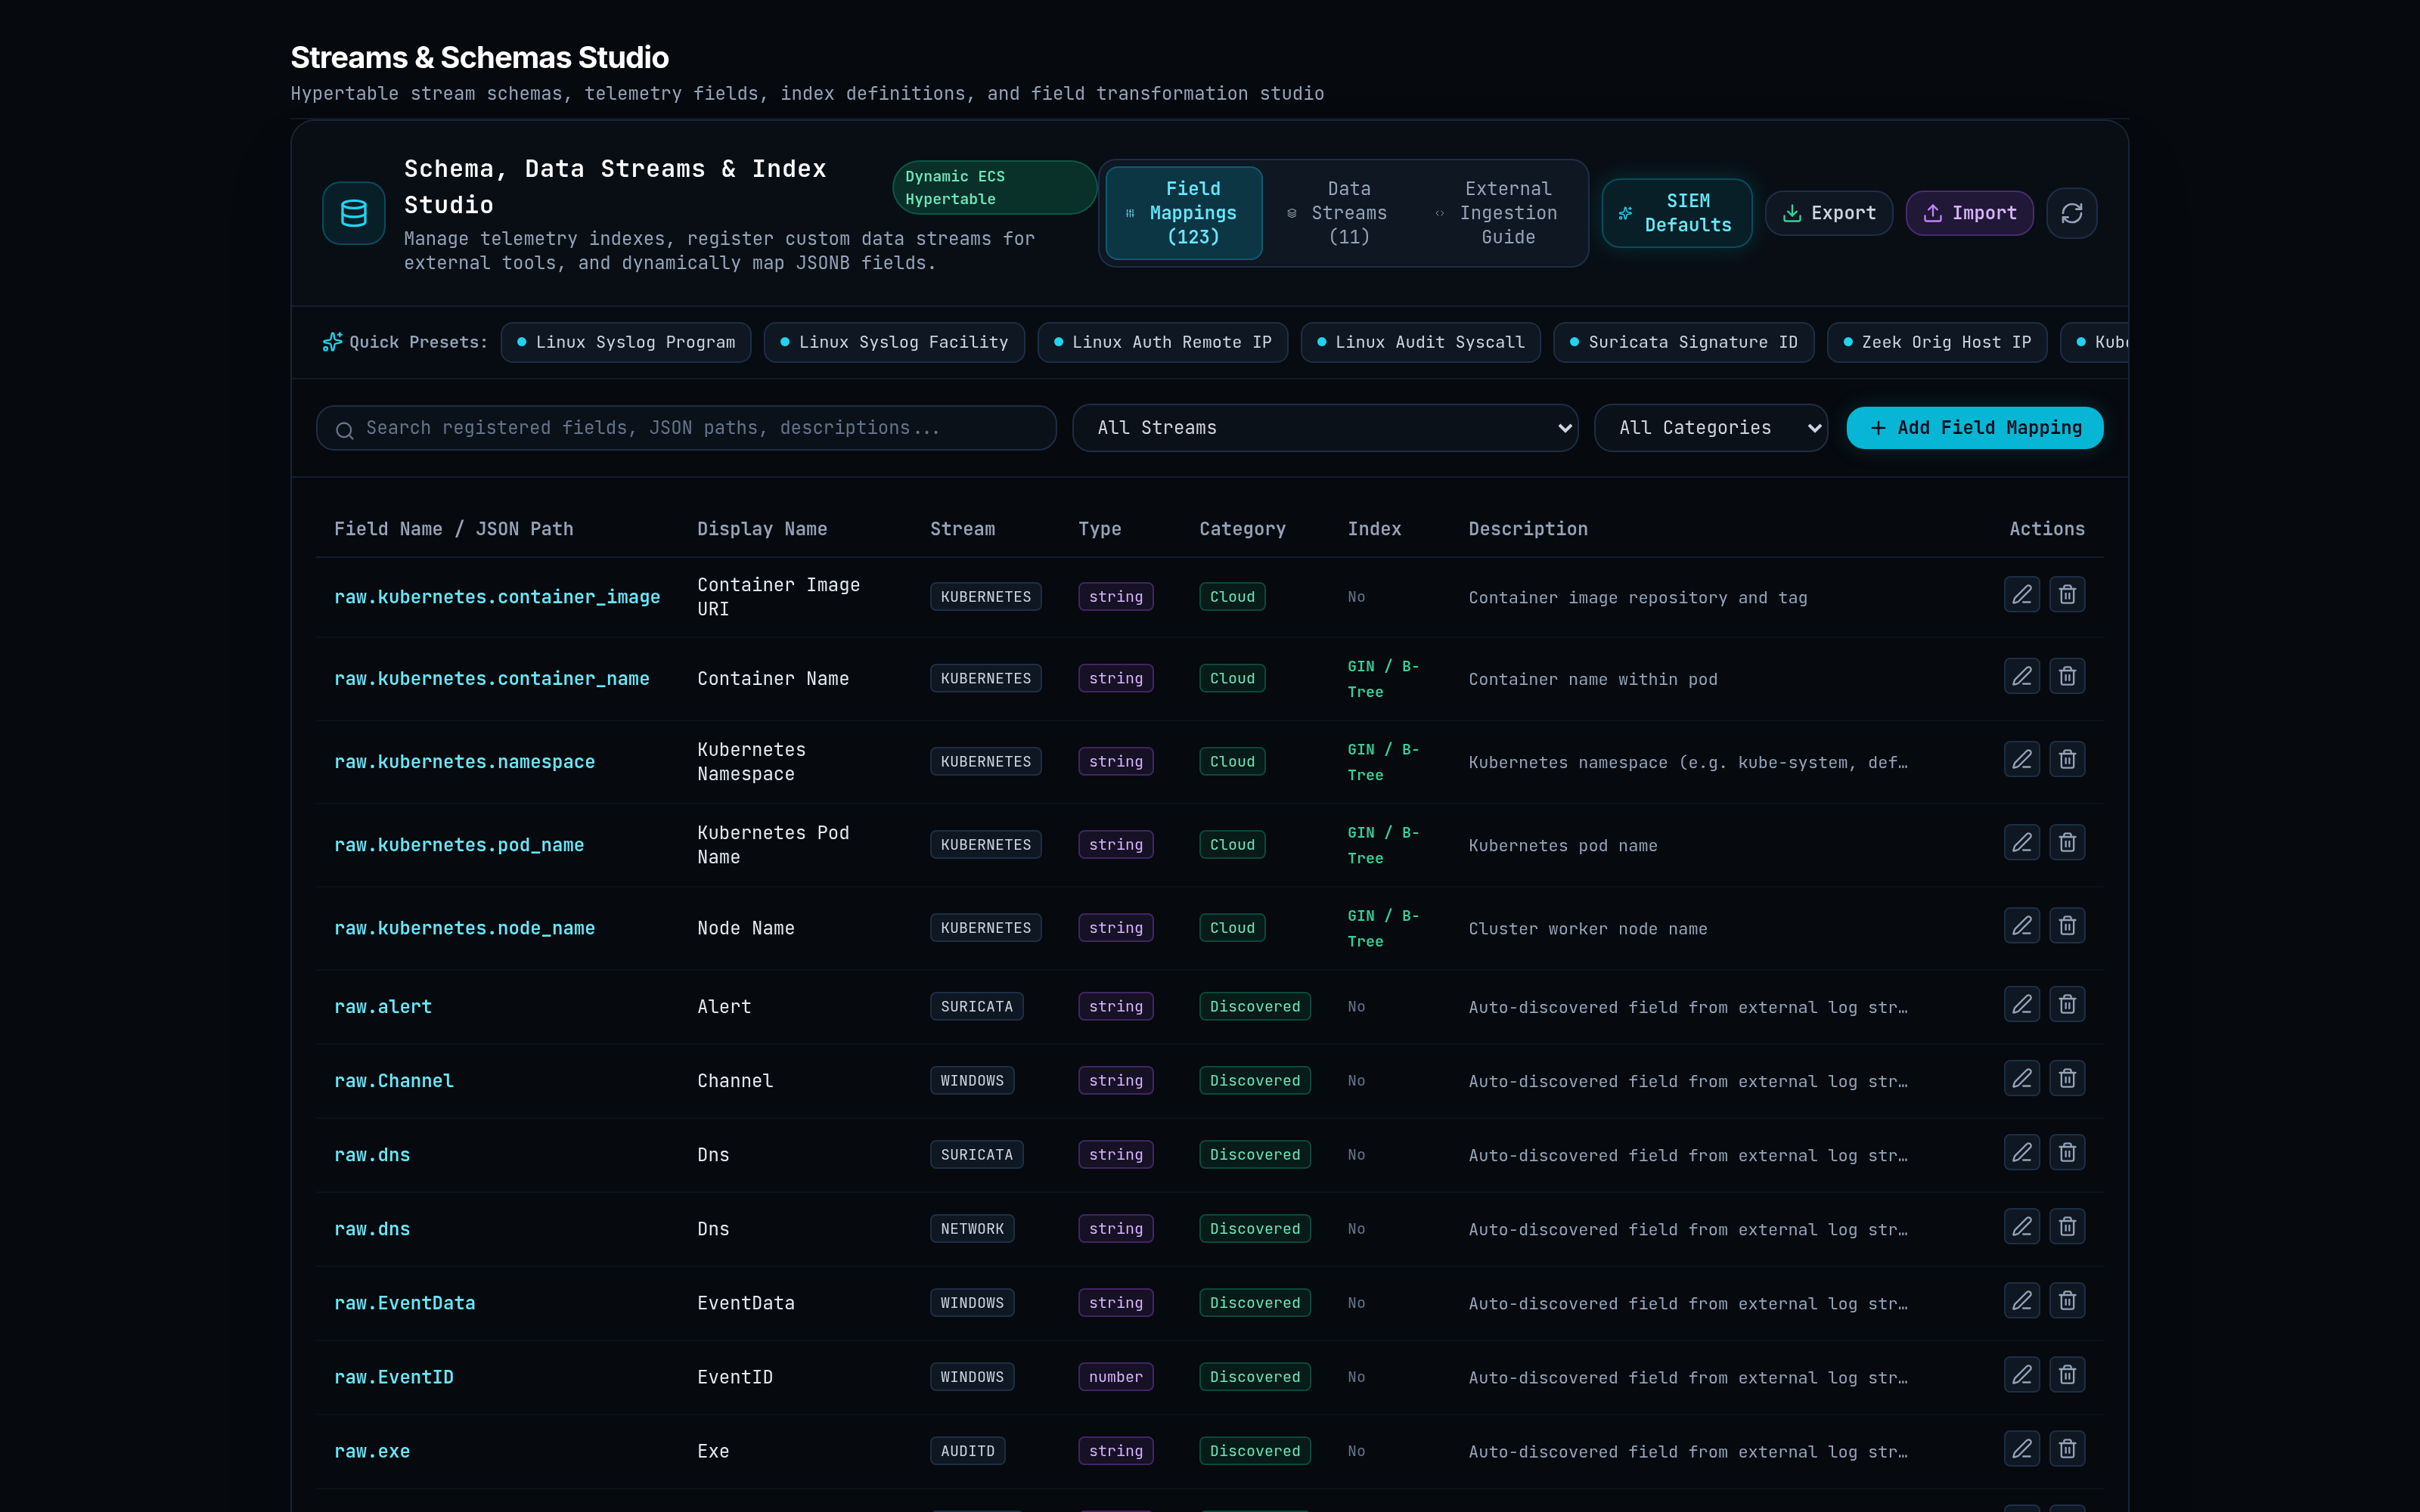
GryphOps Telemetry Hypertable Studio
TimescaleDB Dual-Spectrum Schema Management & Chunk Compression

Inspect and optimize the underlying PostgreSQL/TimescaleDB time-series hypertables storing billions of host and wire telemetry records. Monitor chunk distribution, verify disk compression ratios (high-ratio columnar ZSTD compression), and configure automated rollups and retention policies.

PostgreSQL HypertablesColumnar ZSTD CompressionChunk LifecycleData Retention Policies
KEY CAPABILITIES & ARCHITECTURE
Transparent TimescaleDB chunking & retention policies
High-ratio ZSTD columnar compression monitoring
Live row count, disk usage, and index performance stats
Seamless schema migrations for custom telemetry fields
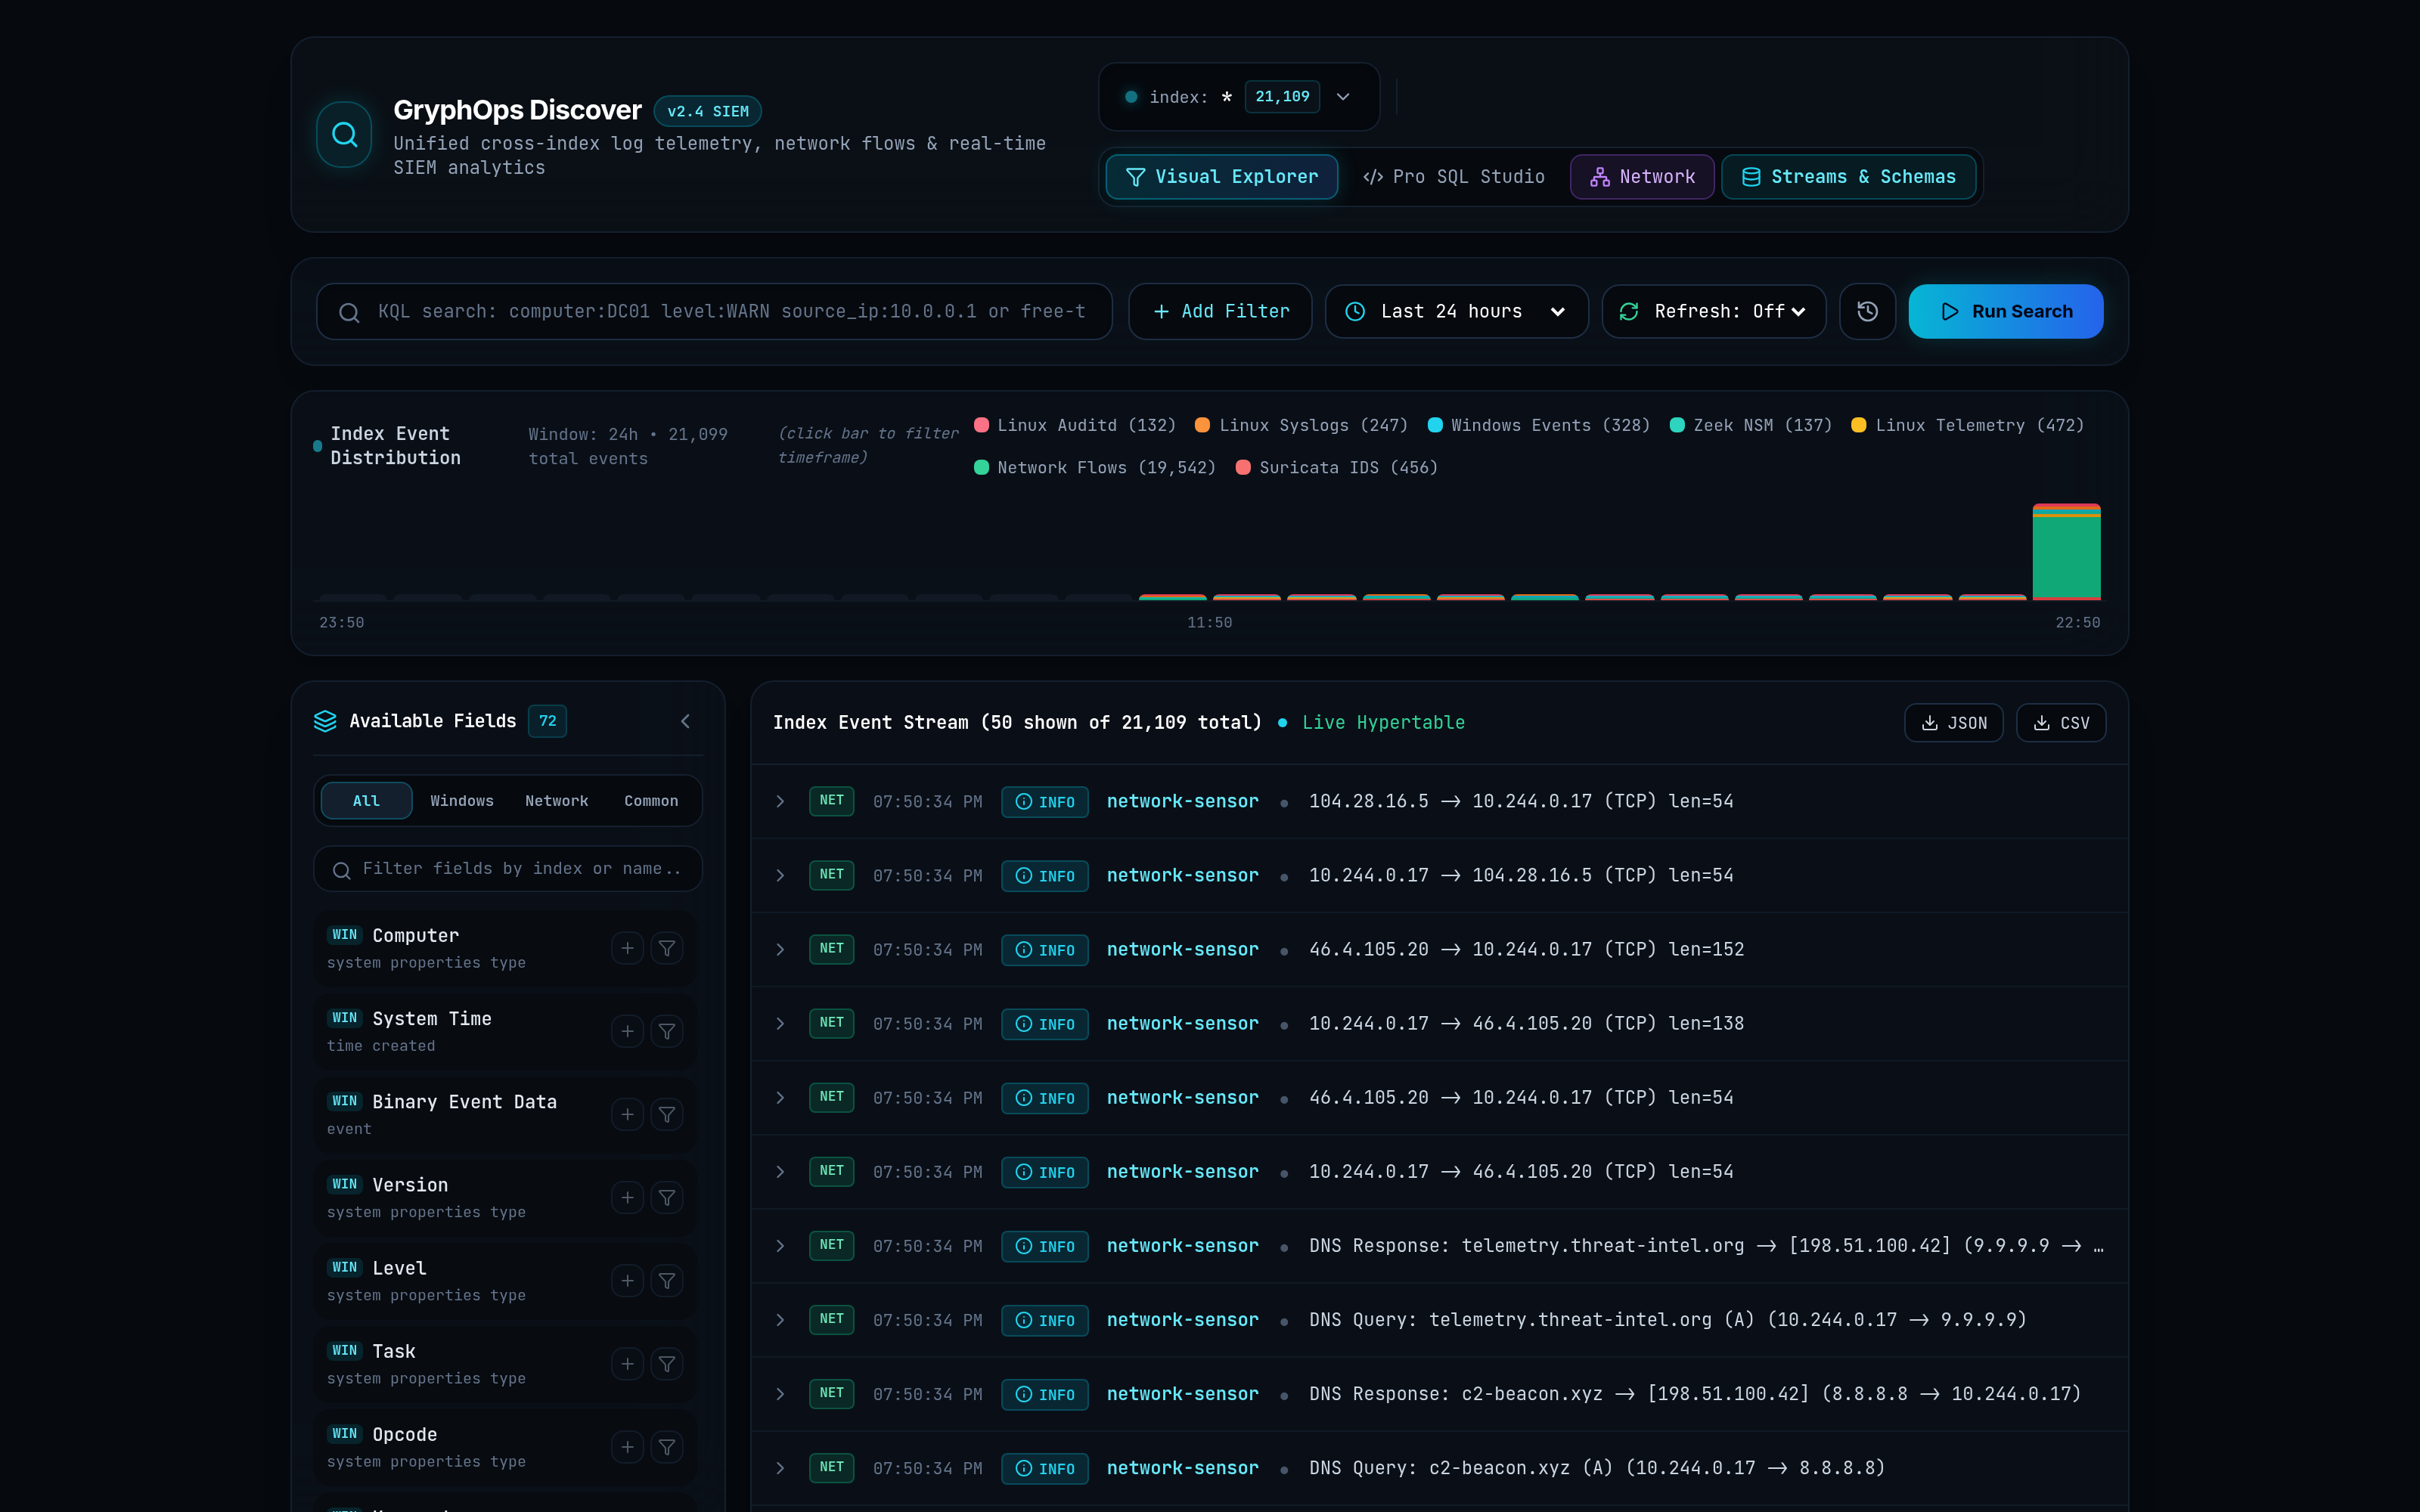
GryphOps Discover SIEM and Log Explorer
Unified Cross-Index Host Logs & Wire Packet Flows

Search millions of host system events (Linux auditd, Windows Security 4624/4688) alongside raw wire packet flows in a unified interface. Filter across time, hostnames, protocols, and severities with instant Lucene-style search syntax. Pinpoint the exact second a network connection occurred and identify the spawning process.

Lucene & SQL SyntaxTimeline HistogramsCross-Index QueryForensic Export
KEY CAPABILITIES & ARCHITECTURE
Sub-millisecond query execution across billions of events
Dual-spectrum filtering: toggle Host, Network, or Unified
Visual timeline distribution histograms with zoom scrubbing
Forensic JSON, CSV, and PCAP payload export
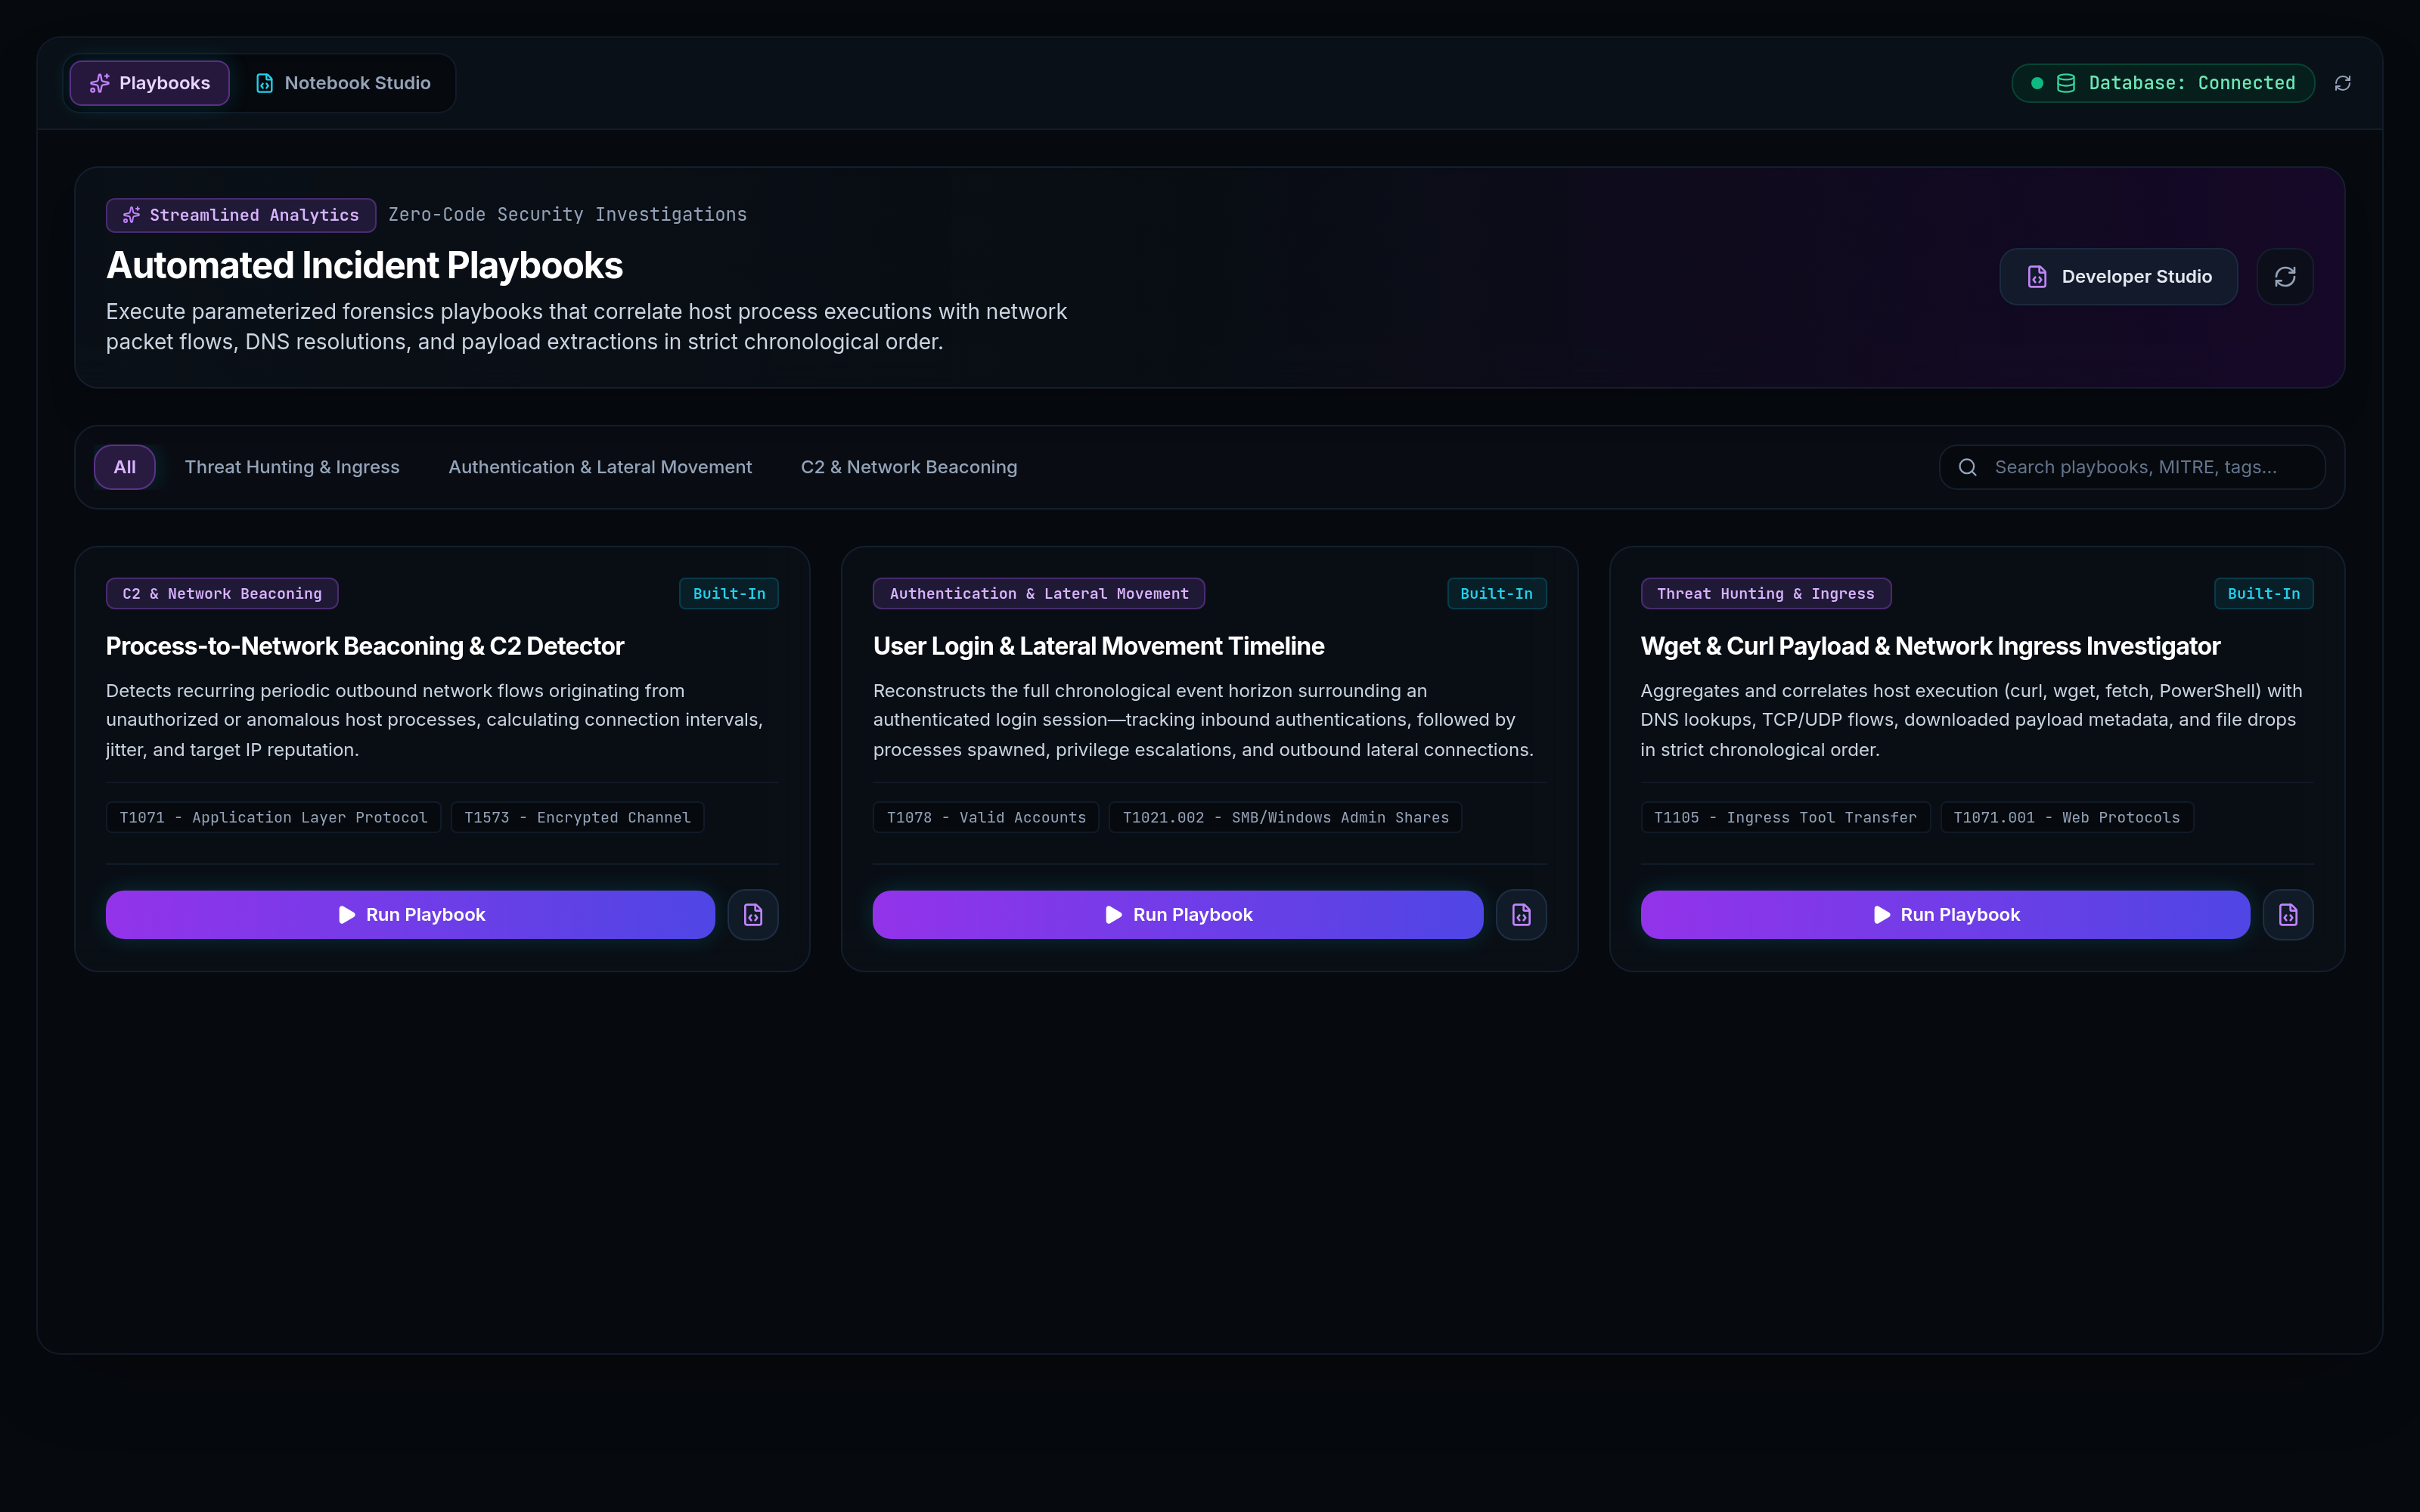
GryphOps AI Threat Hunting and Machine Learning
Unsupervised Anomaly Detection & Executable Threat Notebooks

Detect stealthy cyber threats that bypass signature-based rules. GryphOps trains unsupervised Isolation Forest models on combined host and wire telemetry to uncover anomalous C2 beaconing, credential dumping, and lateral movement. Execute automated threat hunting playbooks backed by containerized Jupyter worker pods.

Isolation Forest MLJupyter Worker PodsCausal Graph TreesC2 Beaconing Hunt
KEY CAPABILITIES & ARCHITECTURE
Unsupervised Isolation Forest anomaly detection engine
Socket-to-process causal graph reconstruction
Dedicated CPU/GPU worker pod execution for threat playbooks
Pre-built threat notebooks for C2 beaconing & data exfiltration
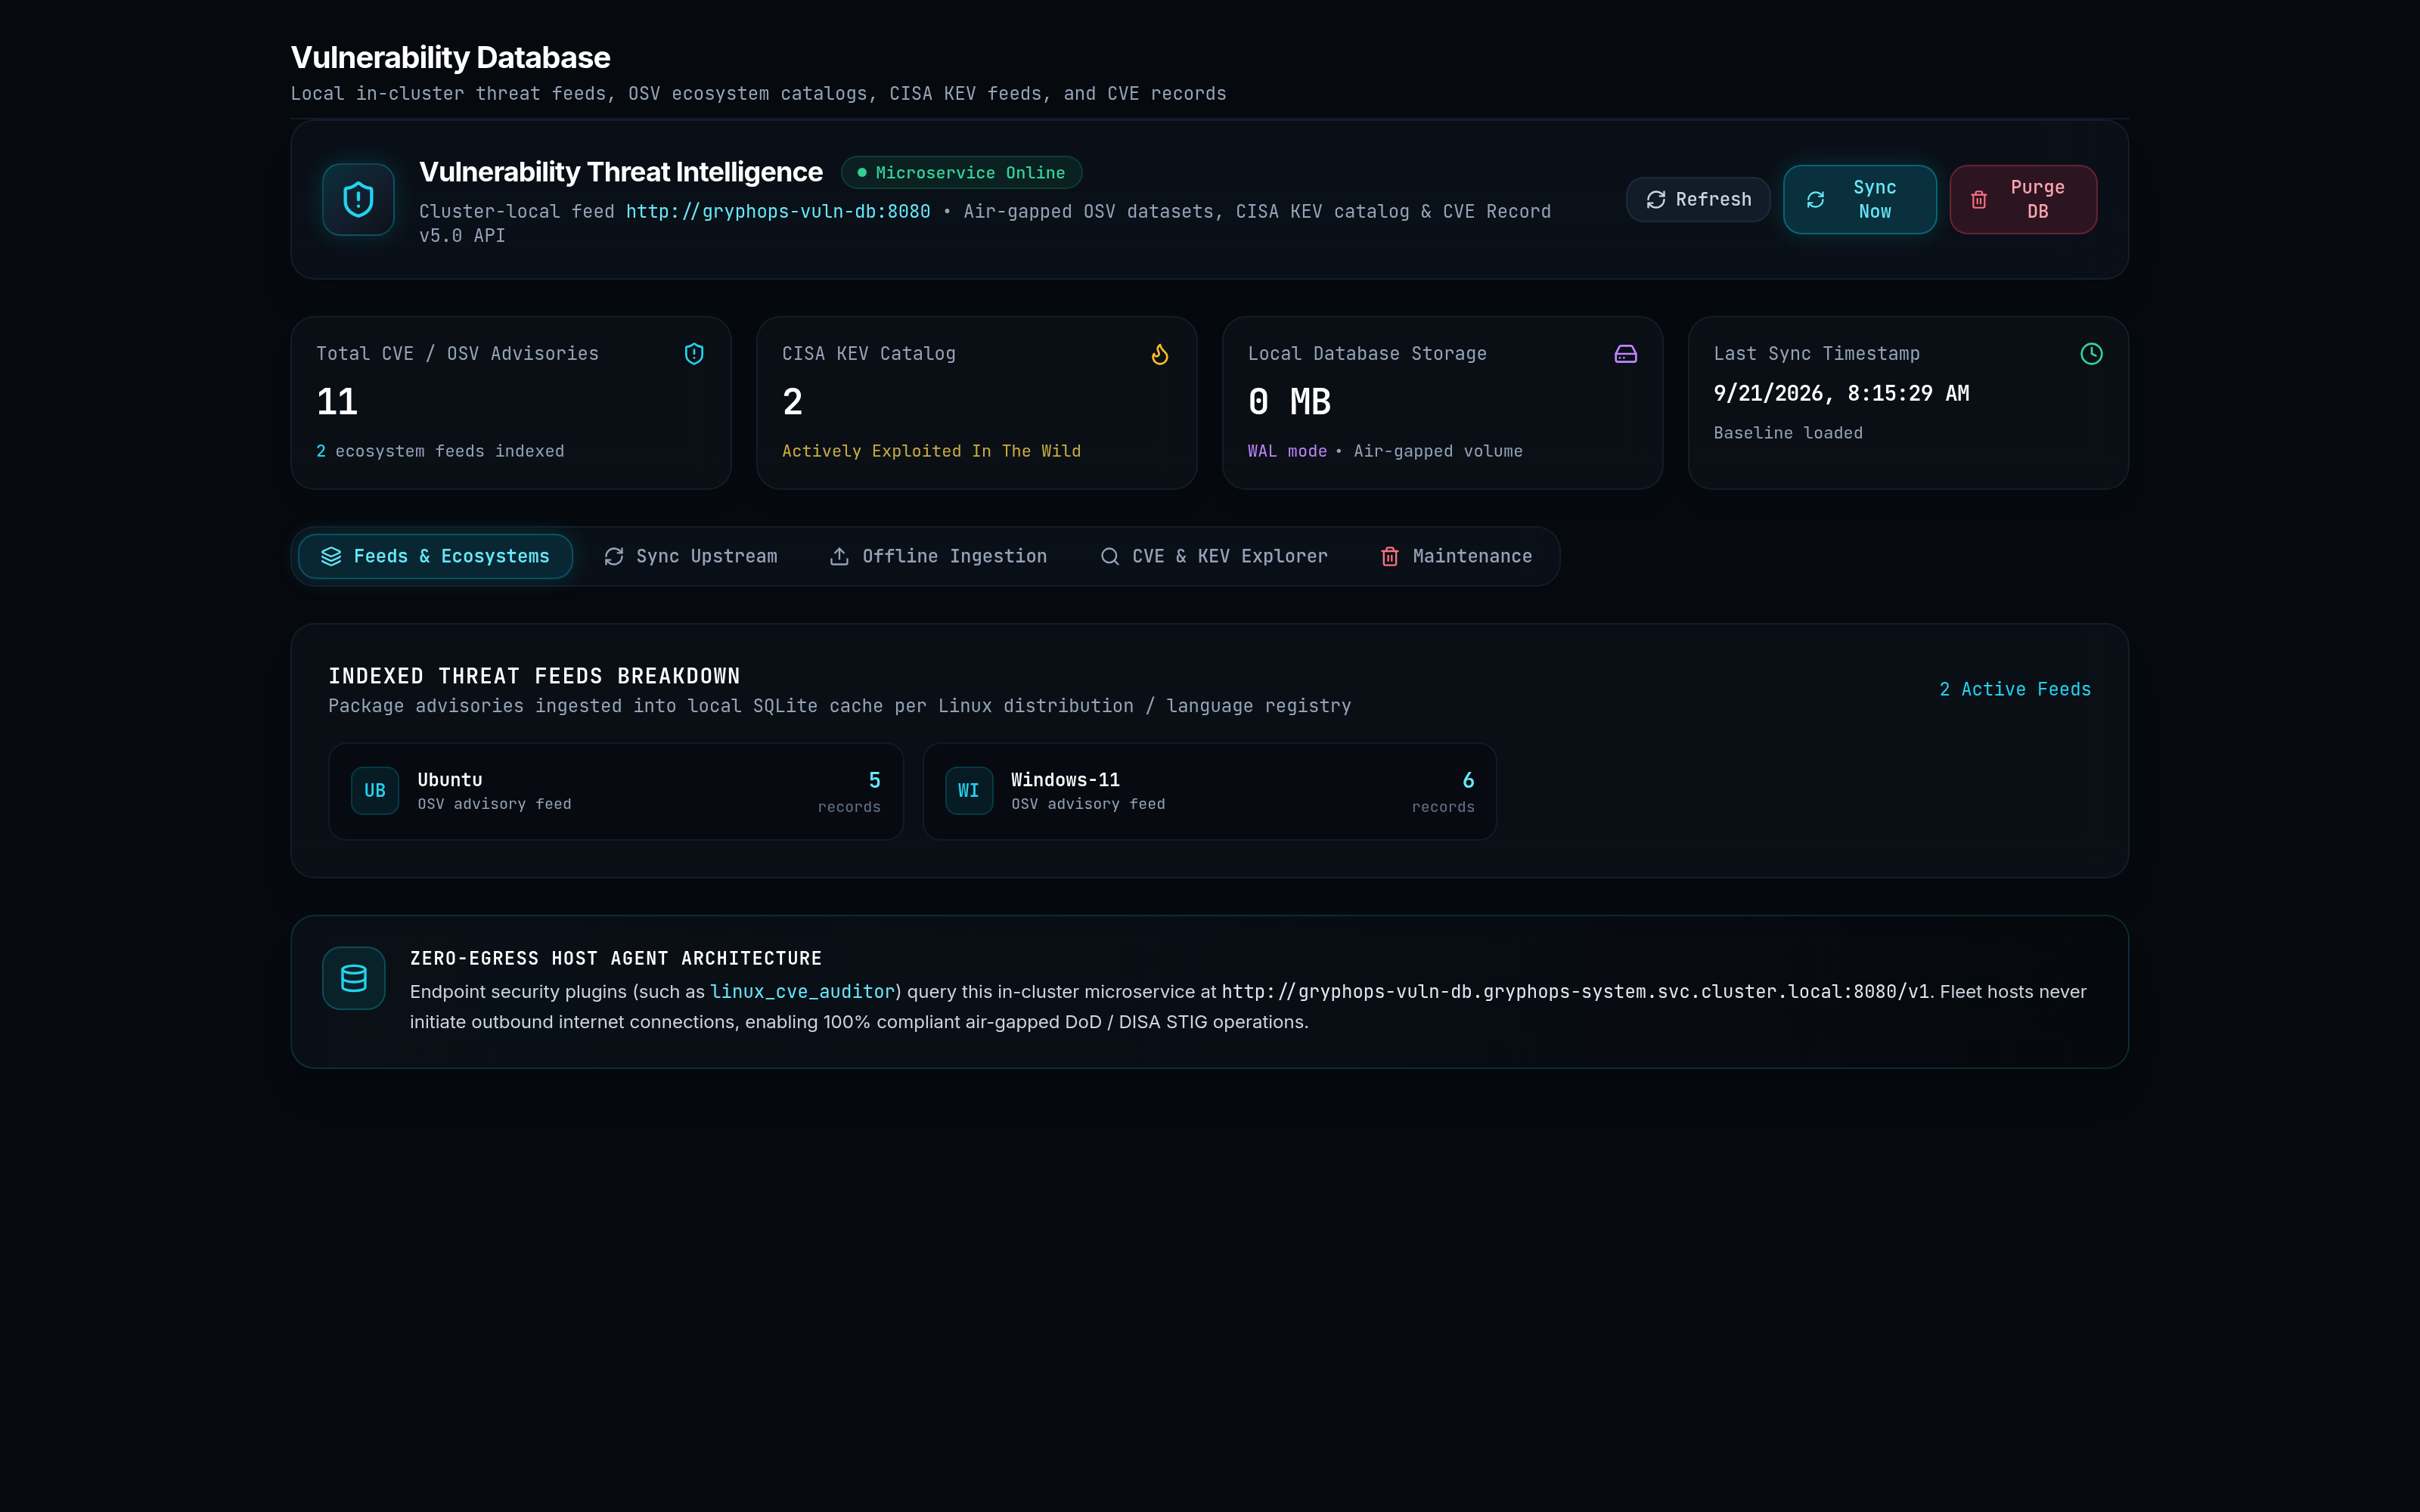
GryphOps Vulnerability and Threat Intelligence Database
OSV, NVD & CISA Known Exploited Vulnerabilities (KEV) Feeds

Correlate installed software packages and kernel versions across your entire fleet against real-time vulnerability databases. Ingest upstream CVEs, GitHub Advisory Database, and CISA Known Exploited Vulnerabilities (KEV) catalog with severity scoring, CVSS v3 vectors, and actionable remediation steps.

CISA KEV CatalogsOSV & NVD FeedsCVSS v3 ScoringAutomated Remediation
KEY CAPABILITIES & ARCHITECTURE
Automated fleet package cross-referencing against OSV & NVD
CISA KEV flag indicators for actively exploited zero-days
Severity categorization (Critical, High, Medium, Low)
1-click generation of host vulnerability remediation tickets
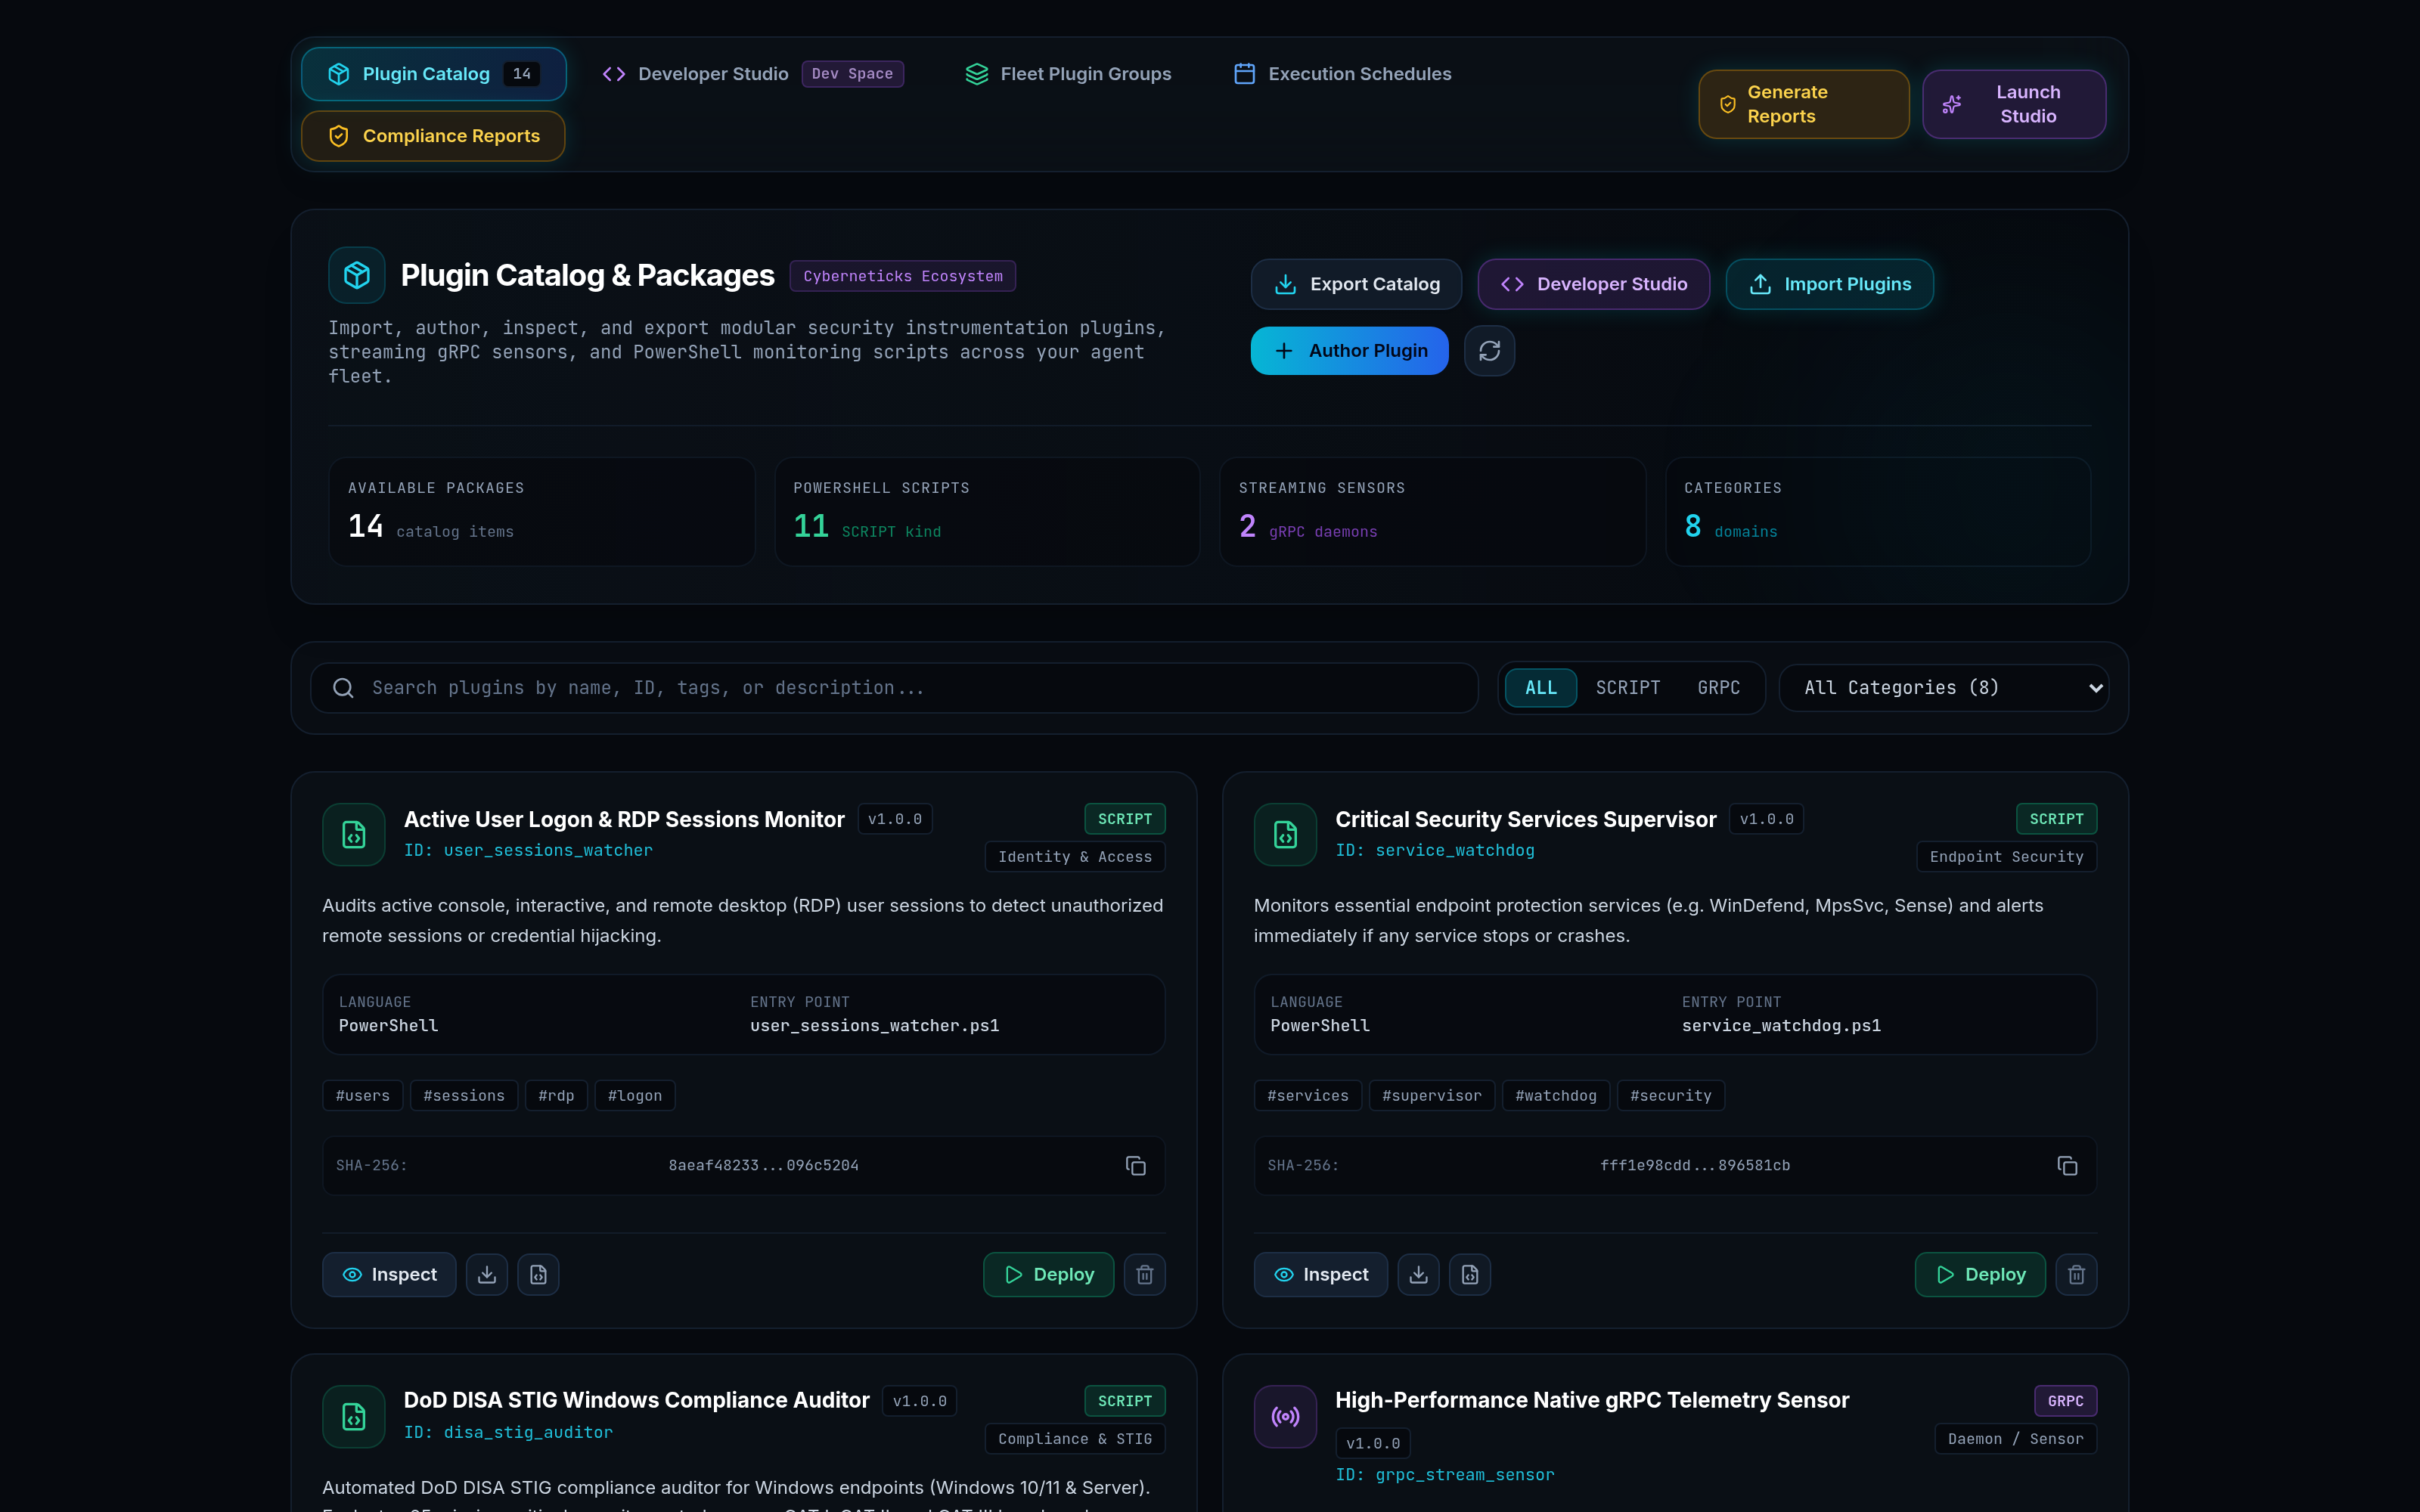
GryphOps Dynamic Plugin Catalog and Schedules
Modular Security Instrumentation, STIG Audits & Cron Schedules

Extend agent capabilities dynamically without recompiling or redeploying agent binaries. Browse a rich catalog of community and enterprise security plugins, including DISA STIG compliance auditors, CVE scanners, firewall verifiers, and custom gRPC streaming probes. Schedule recurring runs across targeted fleet groups.

Hot-Load ScriptsCron OrchestrationgRPC Streaming ProbesFleet Targeting
KEY CAPABILITIES & ARCHITECTURE
Hot-loadable PowerShell, Bash, and compiled Go/gRPC plugins
Targeted fleet deployment by environment, OS, or custom tags
Flexible cron-based recurring execution scheduling
Real-time execution status, error logging, and output parsing
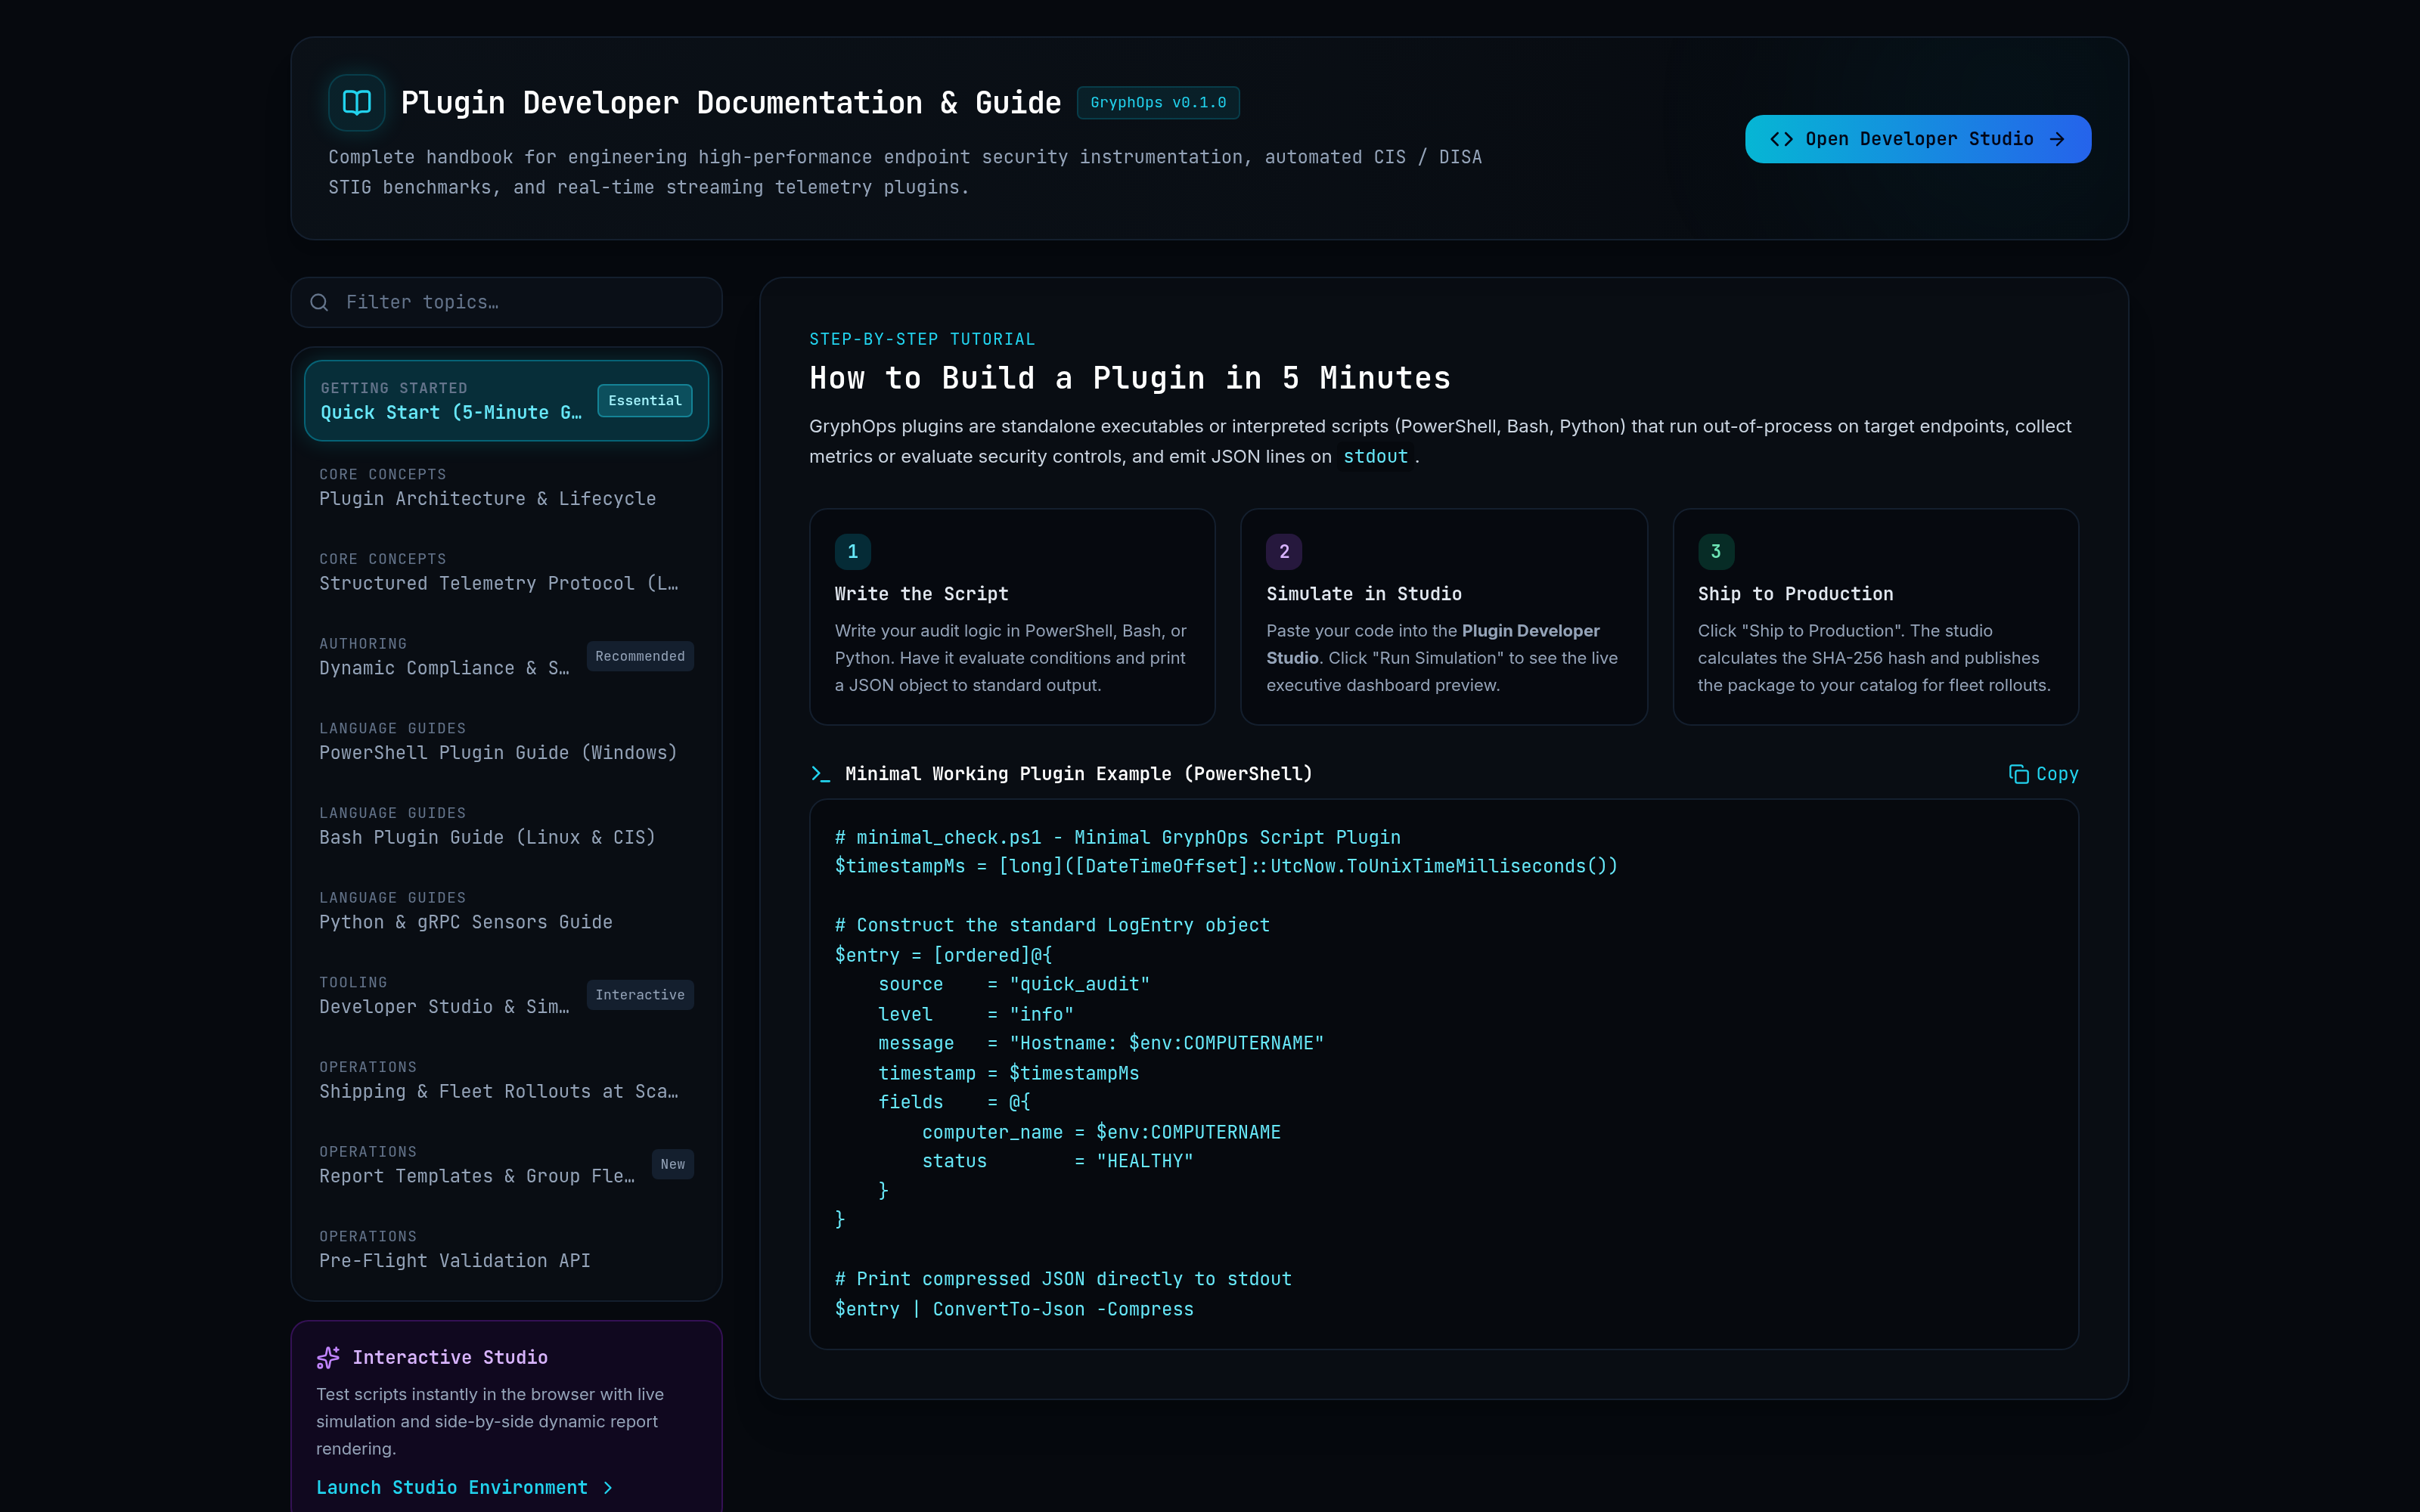
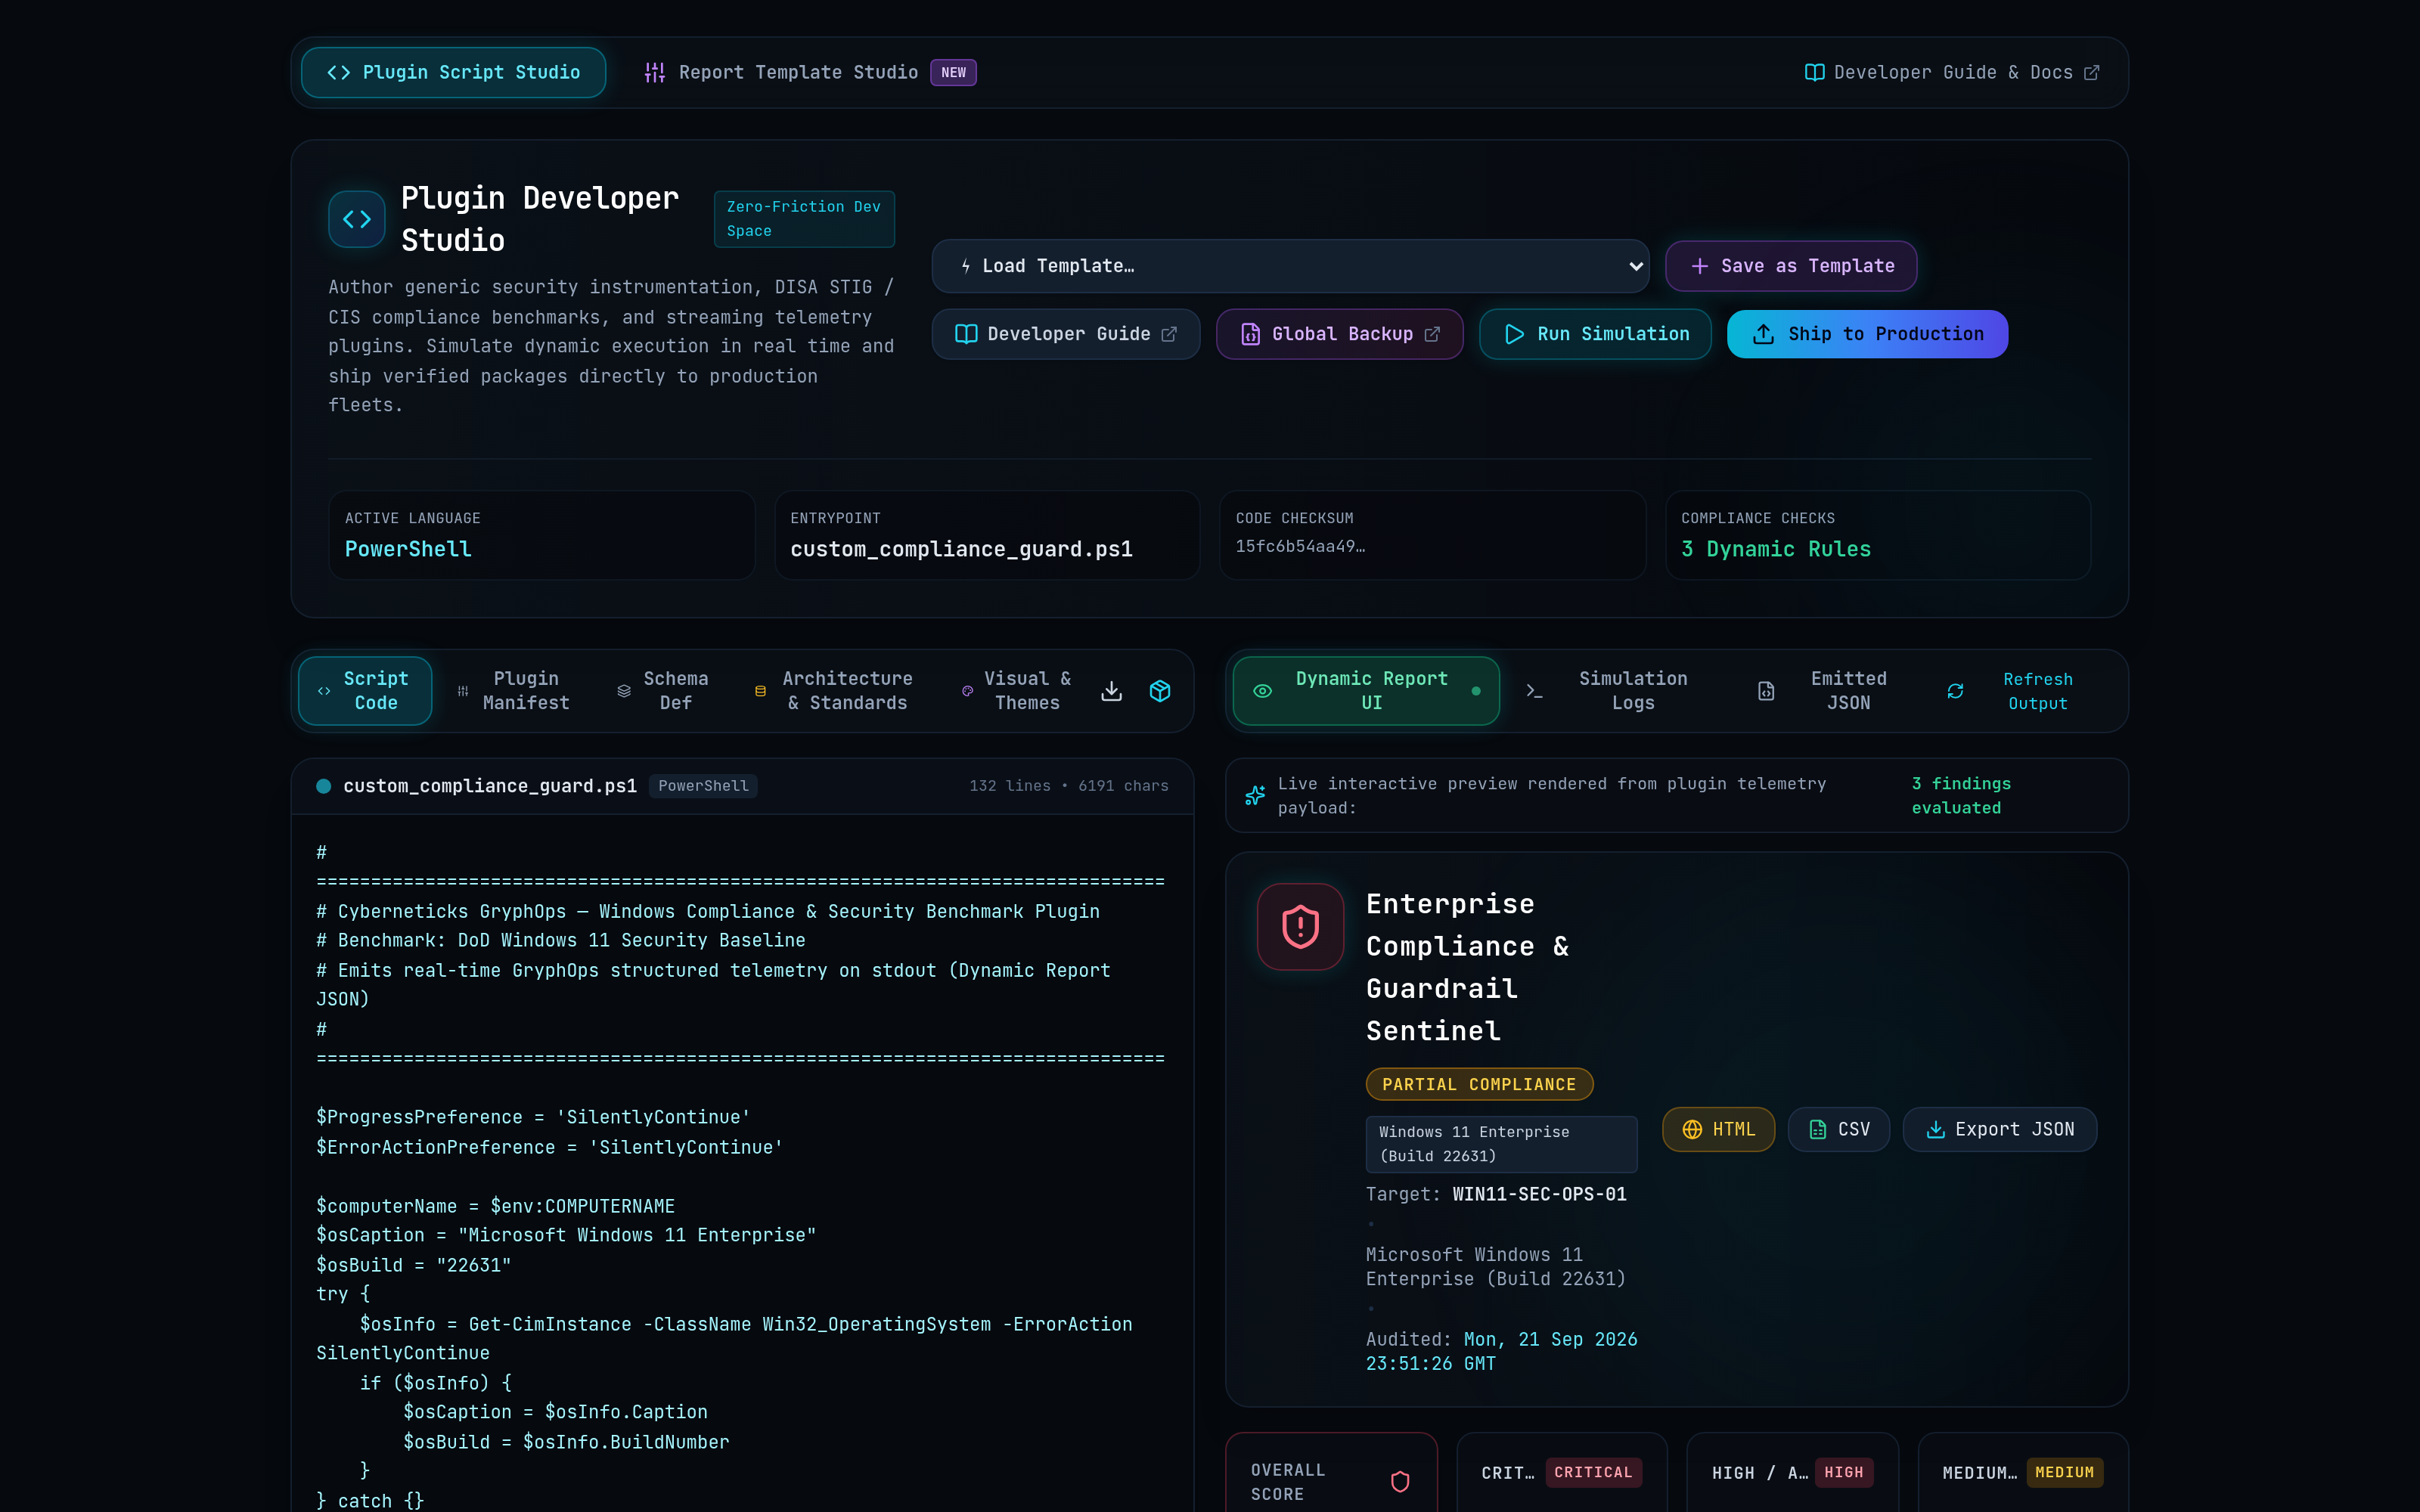
GryphOps Plugin Developer Studio
Monaco Code Editor, Plugin Manifests & Live Report UI Preview

A full-featured in-browser development environment for authoring custom security plugins and dynamic report templates. Features syntax highlighting, manifest linting, in-browser sandbox simulation, and a live rendering pane that displays generated compliance report cards before shipping to production fleets.

Monaco Code EditorSandboxed SimulationLive Report PreviewManifest Linting
KEY CAPABILITIES & ARCHITECTURE
Monaco code editor with PowerShell, Bash & Python support
Plugin manifest builder with schema validation
One-click local simulation sandbox with stdout/stderr capture
Live dynamic report UI preview with compliance scorecards
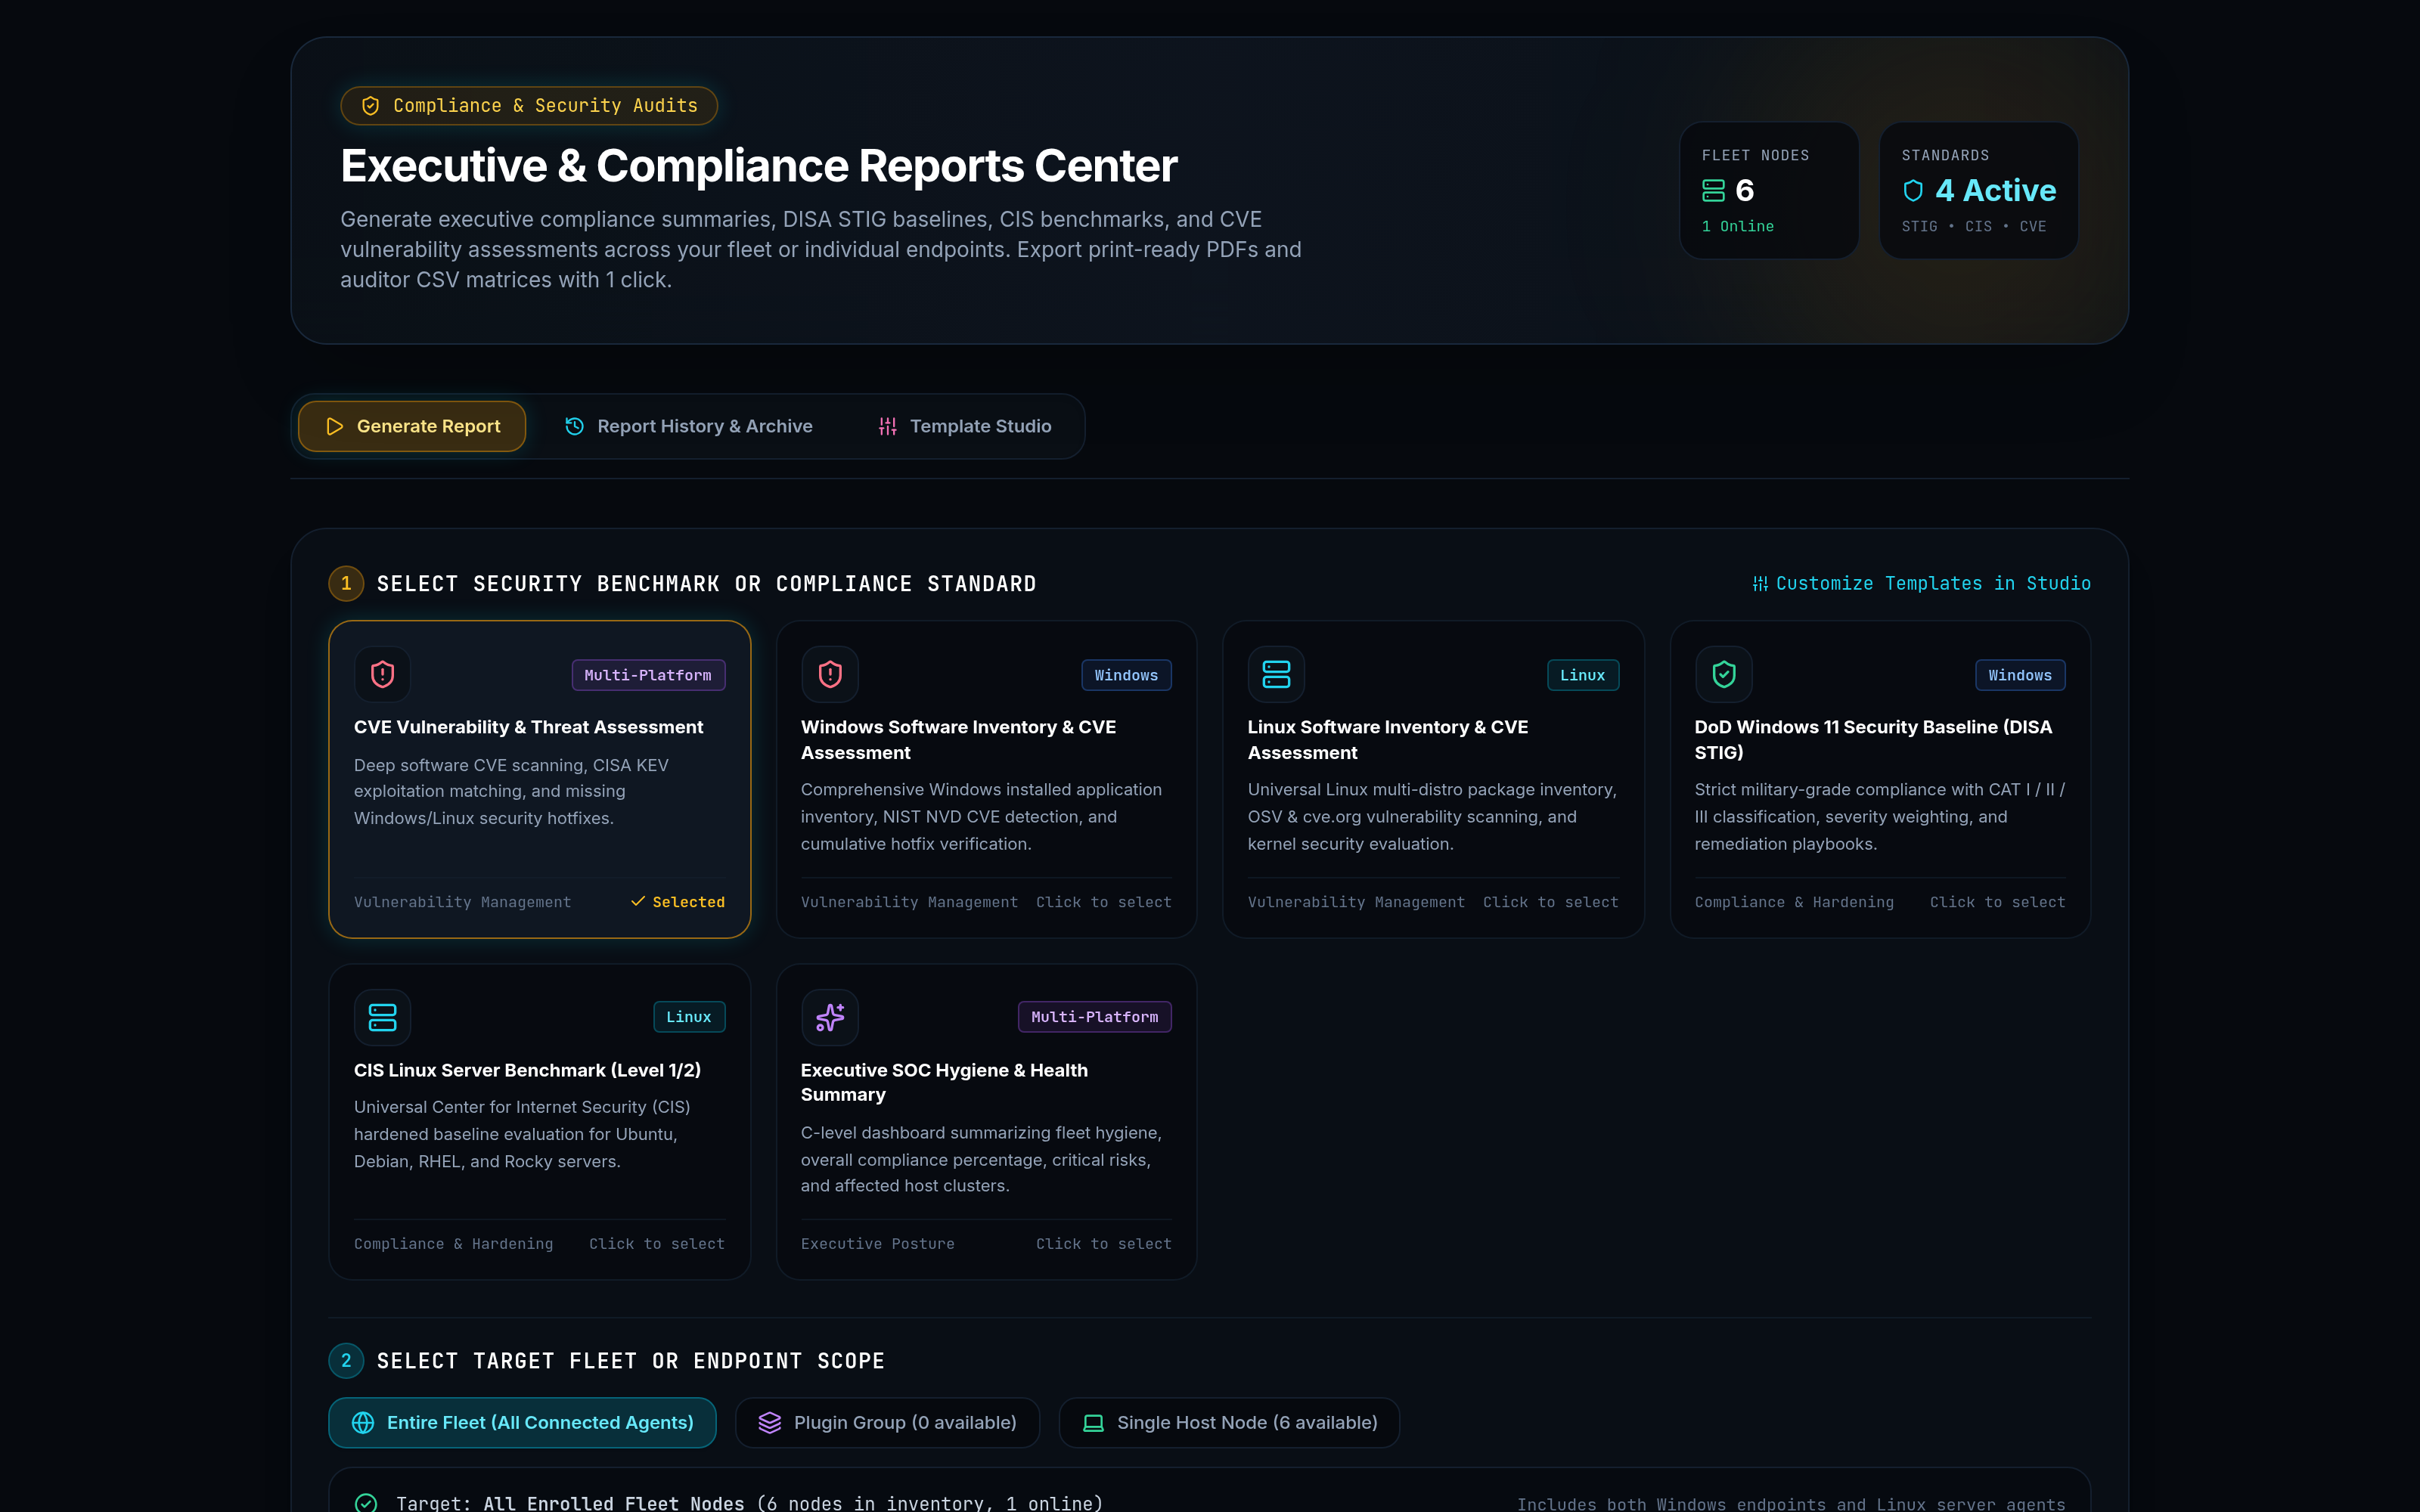
GryphOps Executive and Compliance Reports Center
DISA STIG, CIS Benchmarks, CMMC & Executive Briefings

Generate comprehensive, audit-ready compliance reports for Department of Defense and civilian regulatory frameworks. Evaluates fleet endpoints against DISA STIG baselines, CIS Benchmarks, and CMMC controls. Export branded executive summaries, detailed technical findings, and raw JSON/CSV matrices.

DISA STIG BaselinesCIS BenchmarksPrintable PDF & HTMLDrift Auditing
KEY CAPABILITIES & ARCHITECTURE
Built-in DISA STIG Windows & Linux automated evaluation
CIS Benchmark compliance scoring with pass/fail breakdowns
One-click export to printable HTML, PDF, CSV, and JSON
Historical compliance drift tracking across fleet cycles
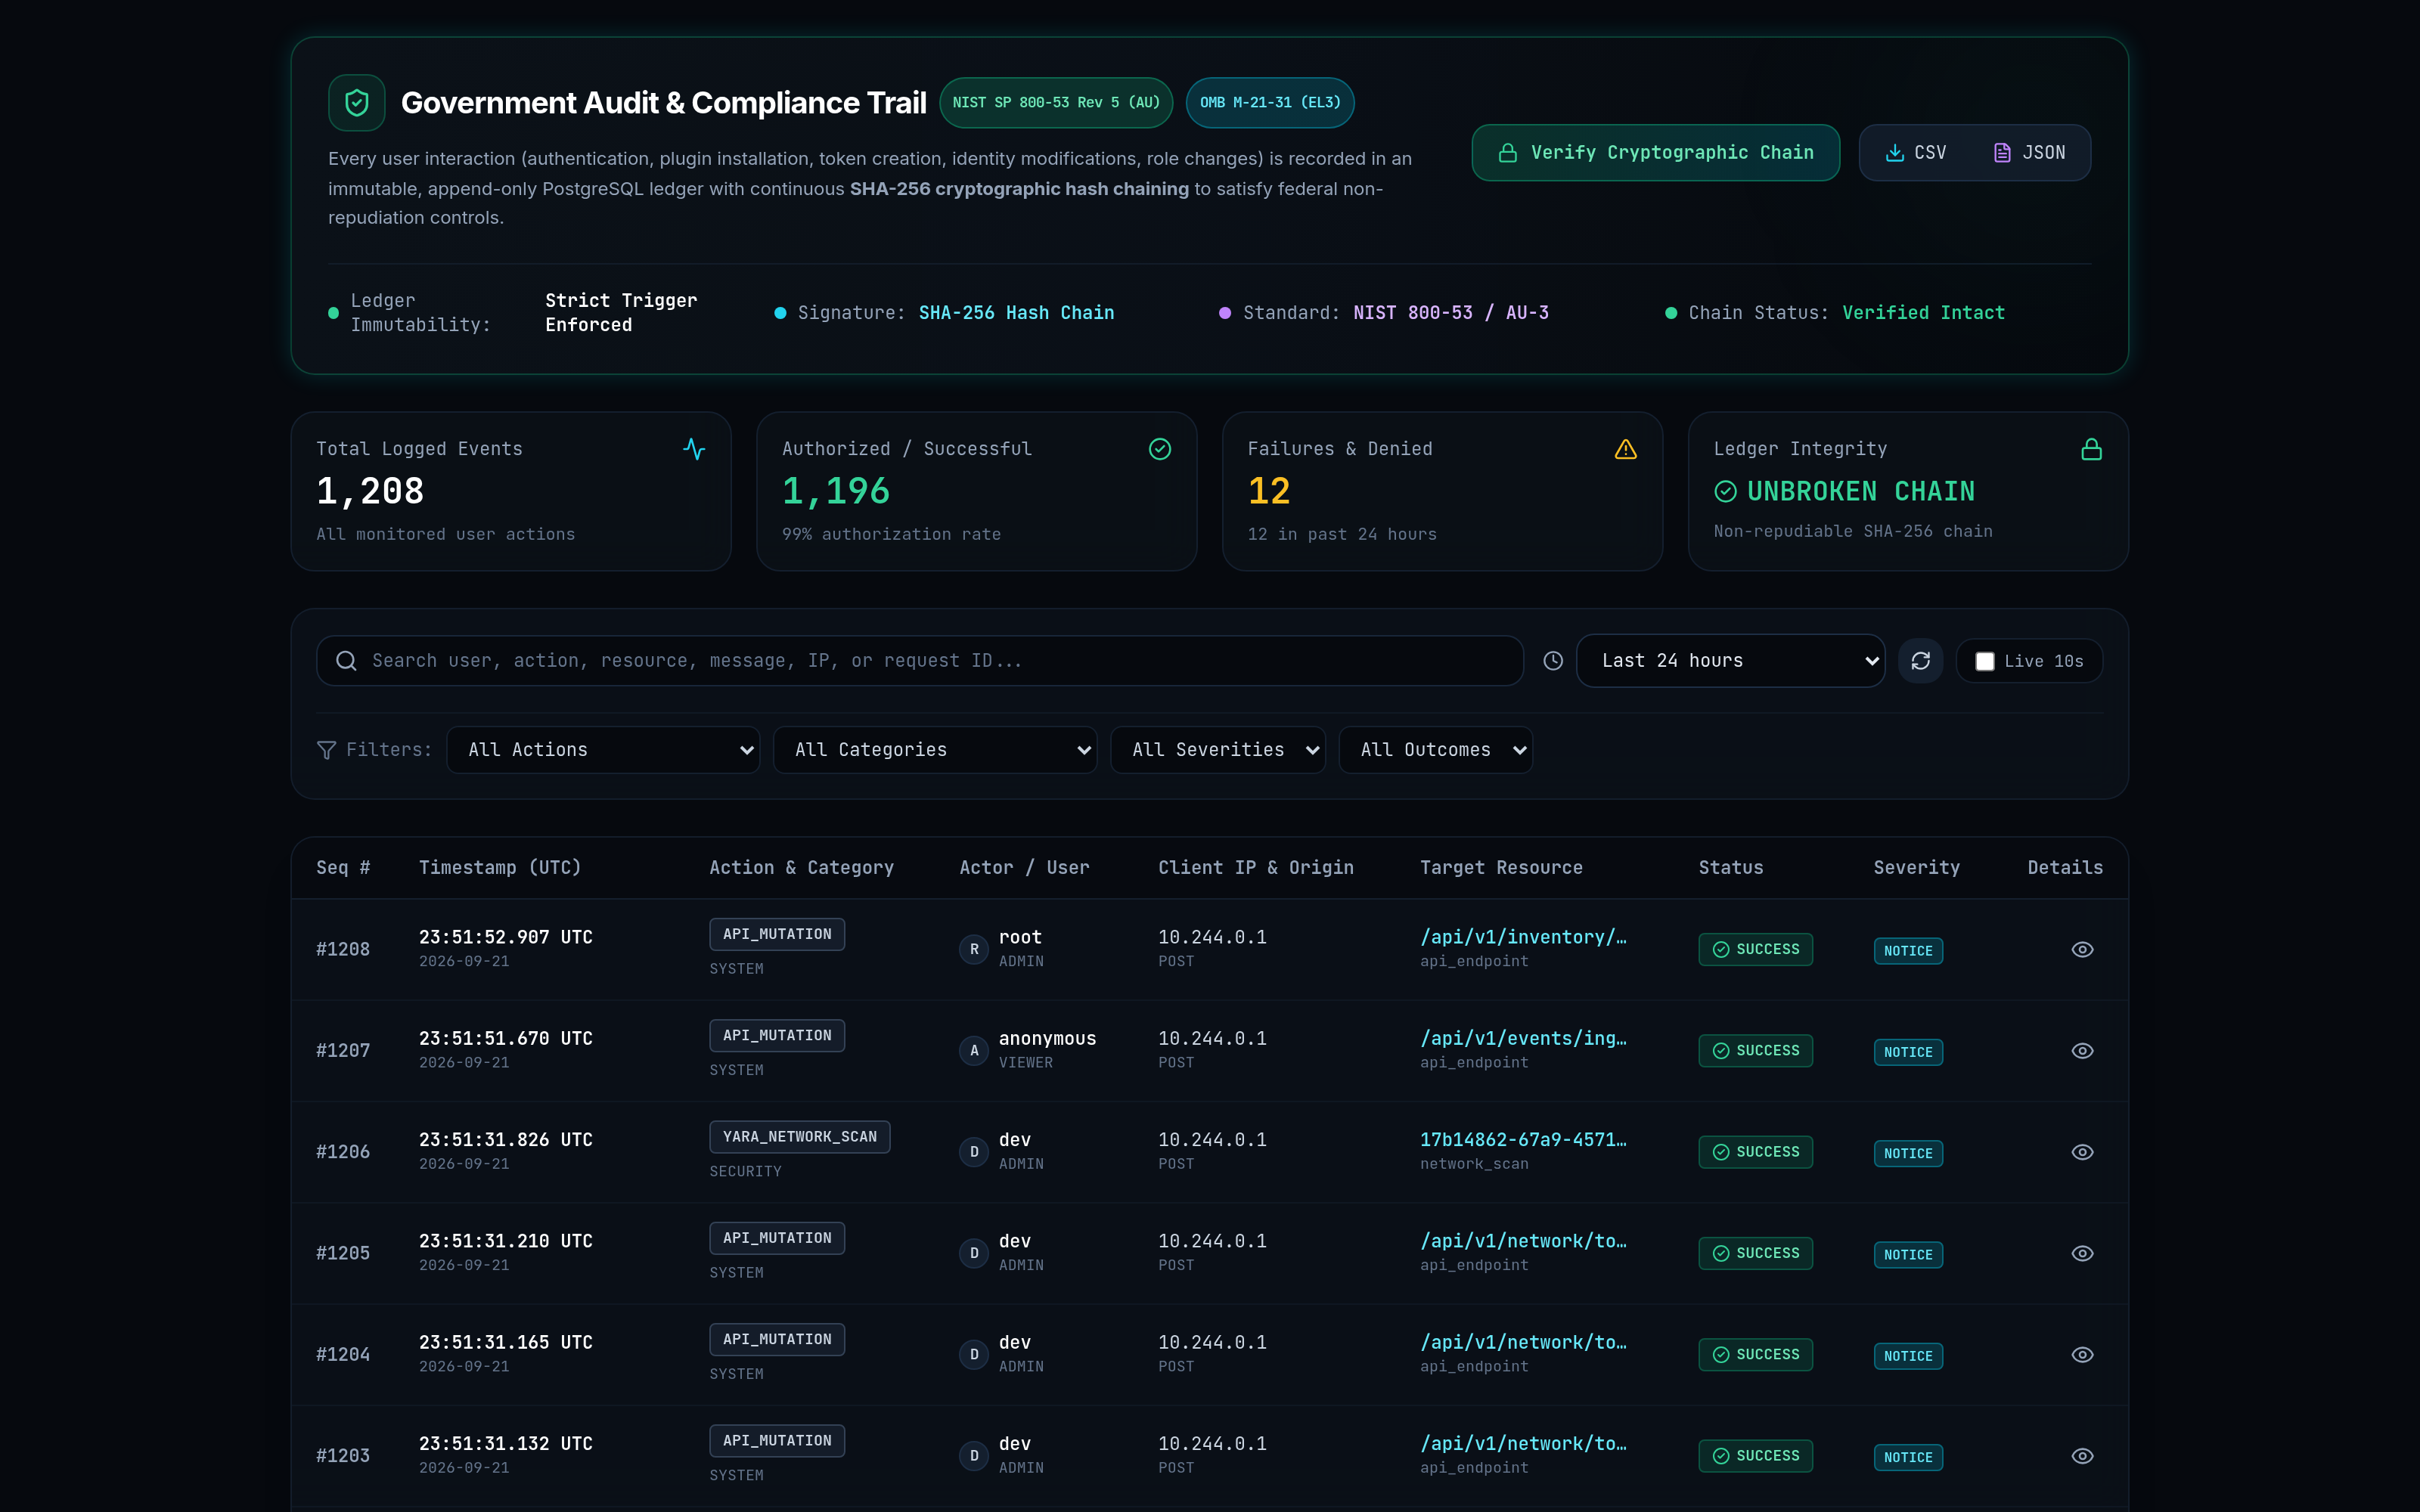
GryphOps Cryptographic Audit Trail and AU Controls
Immutable Sequence Hashes & Comprehensive Administrative Logs

Meet stringent NIST SP 800-53 AU-2/AU-3 auditing requirements. GryphOps cryptographically records every user login, policy dispatch, terminal session initiation, and configuration change into an append-only, tamper-evident audit log with SHA-256 sequence chaining.

NIST SP 800-53SHA-256 ChainingTamper-Evident LogsForensic Attribution
KEY CAPABILITIES & ARCHITECTURE
NIST AU-2 / AU-3 compliant event recording
Cryptographic hash chaining preventing retro-active tampering
Actor, IP address, timestamp, and target attribute attribution
Forensic search and SIEM forwarding integration
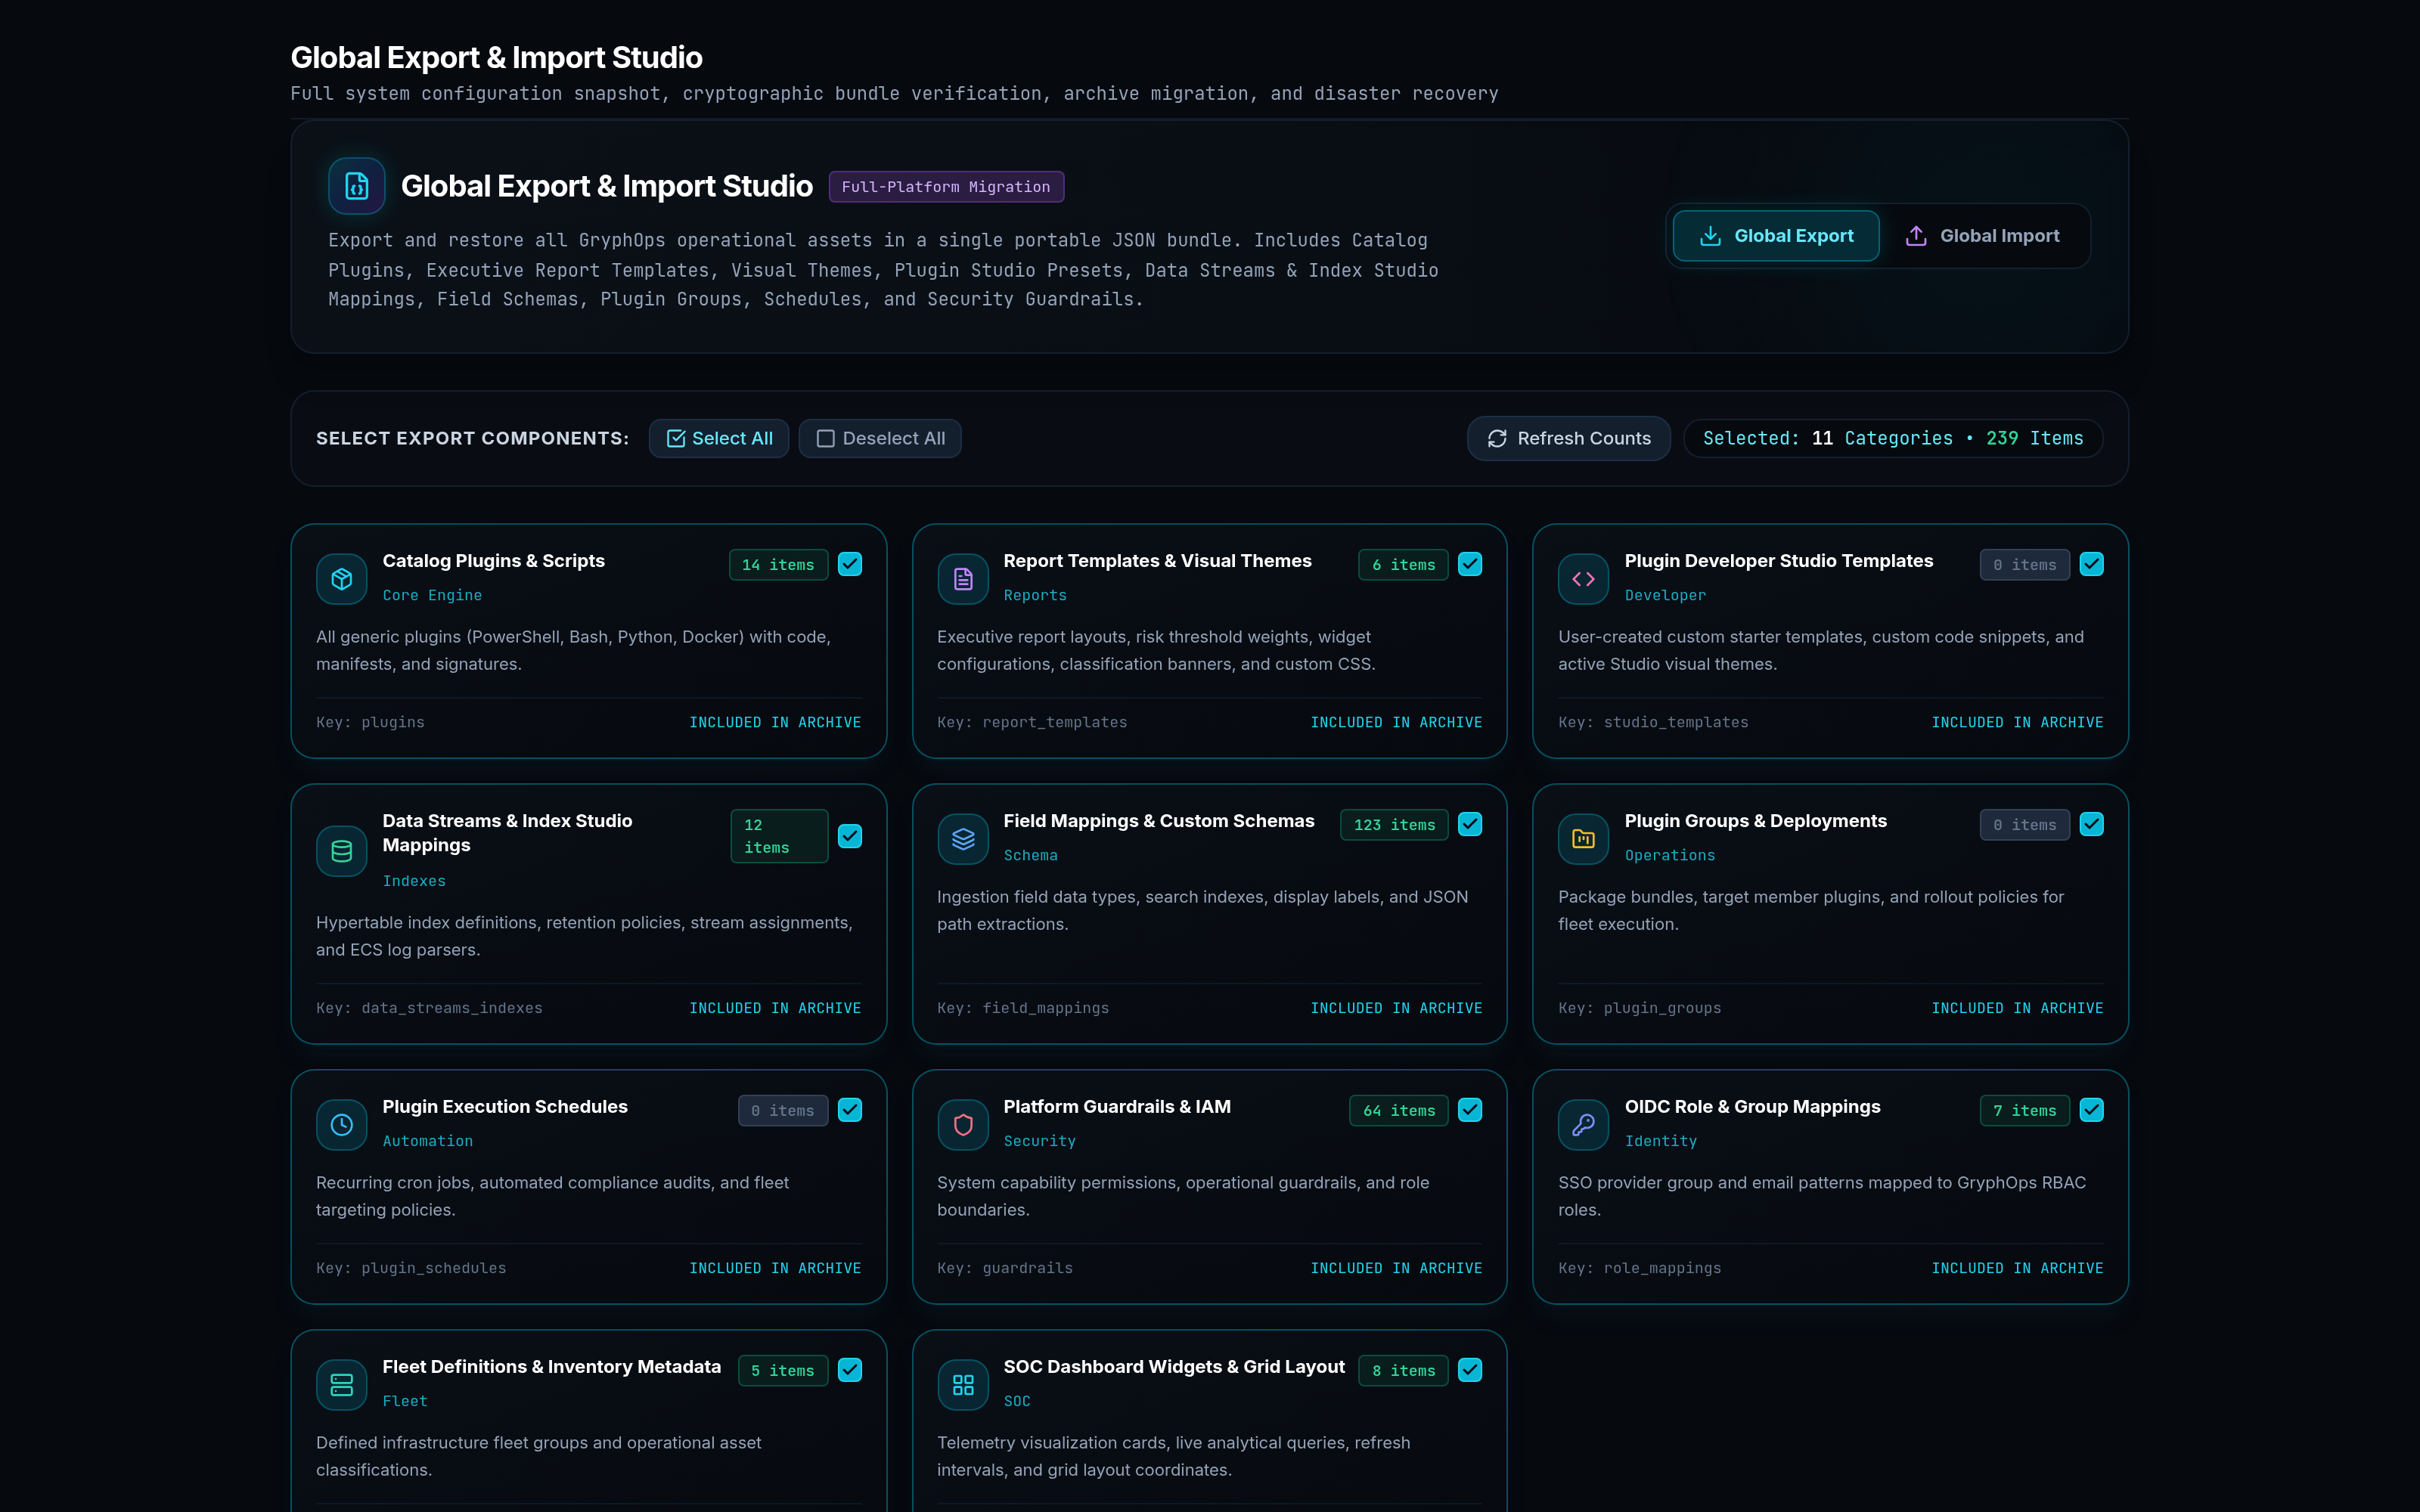
GryphOps Sovereign Air-Gap Backup and Migration Studio
Encrypted Snapshot Archives & Sovereign Enclave Migration

Ensure operational resilience in isolated, sovereign, or tactical edge deployments. Export full platform snapshots—including user credentials, RBAC policies, plugin scripts, telemetry schemas, and report templates—into encrypted, verifiable archive bundles ready for air-gapped restoration.

AES-256 EncryptionAir-Gap PortabilityDisaster RecoveryZero Cloud Lock-in
KEY CAPABILITIES & ARCHITECTURE
AES-256 encrypted complete platform snapshot bundles
Granular export: schemas, plugins, reports, users, or full DB
One-click disaster recovery restoration with checksum checks
Zero external cloud dependencies for 100% sovereign enclaves
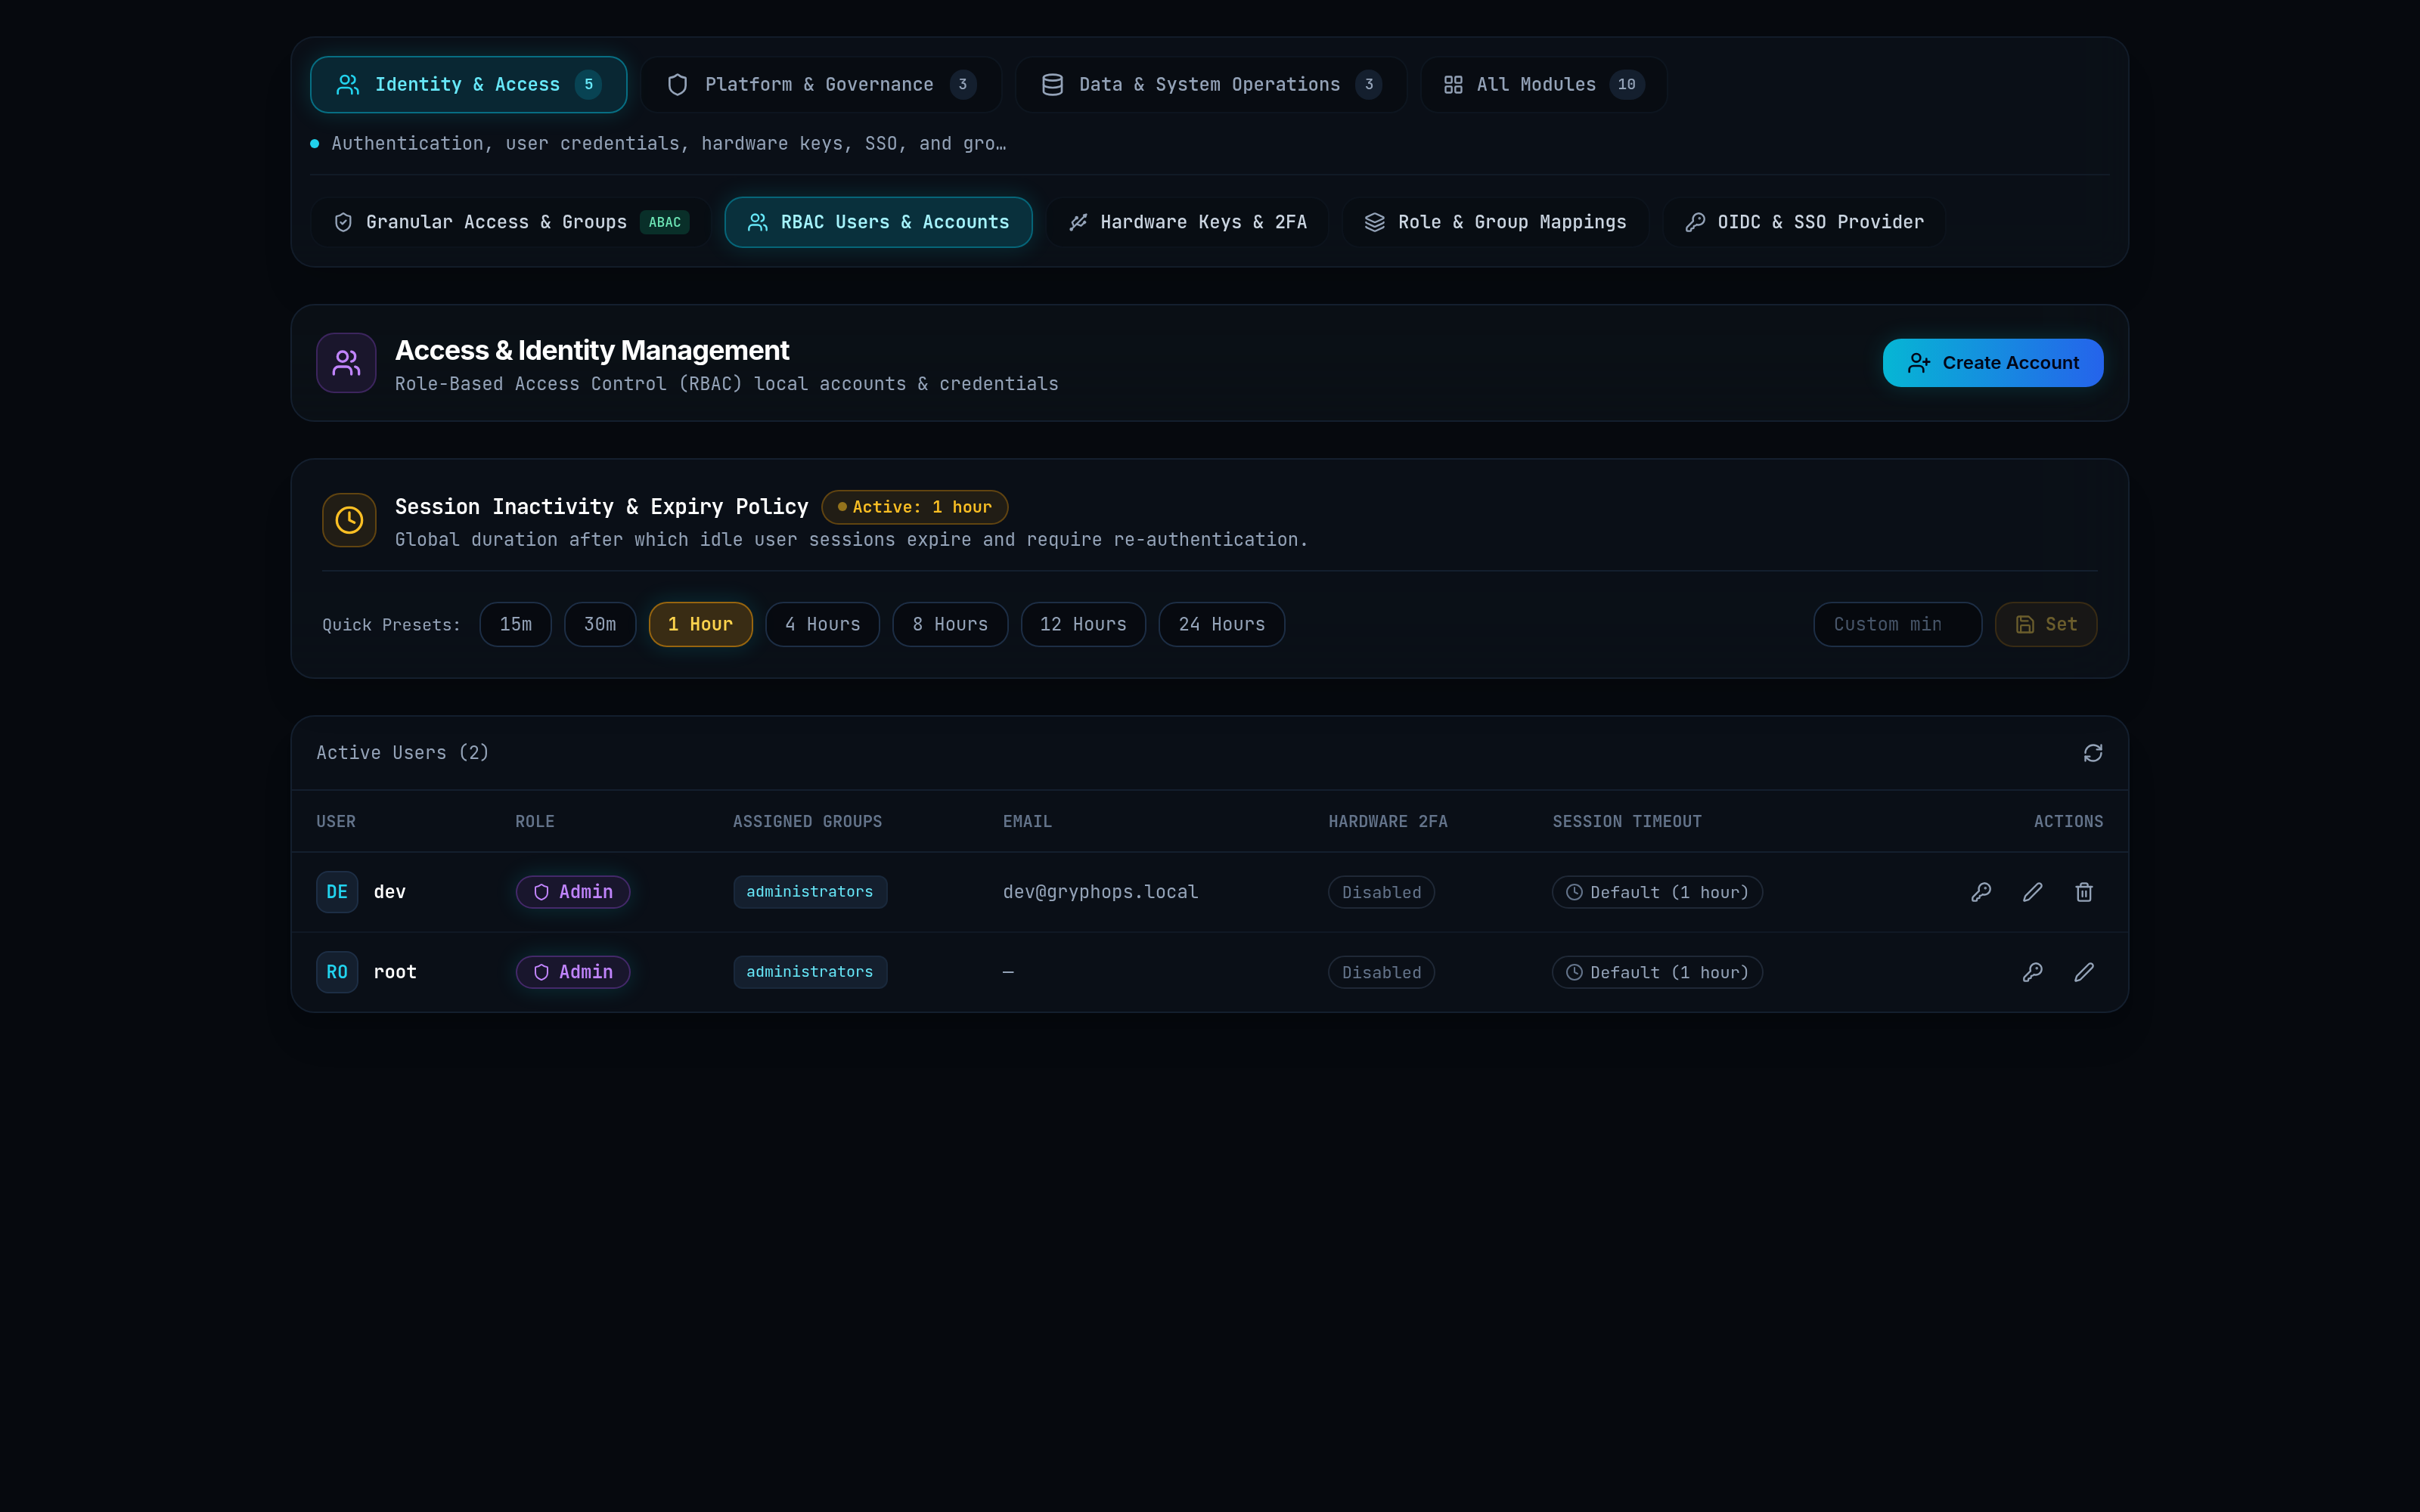
GryphOps Zero-Trust IAM and Hardware Key 2FA
Keycloak OIDC Integration, Granular RBAC & FIDO2 Hardware 2FA

Enforce rigorous Zero-Trust identity and access management. Integrate with enterprise Identity Providers (Keycloak, Okta, Microsoft Entra ID) via OpenID Connect, enforce granular per-feature RBAC permissions, and require hardware-backed WebAuthn/FIDO2 biometric keys for administrative actions.

Keycloak OIDC SSOCapability RBACFIDO2 / WebAuthnSession Guardrails
KEY CAPABILITIES & ARCHITECTURE
OIDC / OAuth2 enterprise SSO integration (Keycloak & Okta)
Fine-grained capability-based RBAC permission matrices
FIDO2 / WebAuthn hardware security key biometric MFA
Configurable session timeouts and strict IP allowlisting
OPERATIONS & FLEETSOC Command Center

Dual-Spectrum Wire & Host Engine

Unified hypertable ingestion correlating live eBPF wire traffic with endpoint OS audit events with sub-millisecond precision.

Military-Grade RBAC & mTLS

End-to-end mutual cryptographic verification, Keycloak OIDC authentication, and FIDO2/WebAuthn hardware key biometric protection.

Automated ML Threat Hunting

Isolation Forest anomaly detection models scoring millions of host and wire security events to uncover lateral movement in real-time.

Sovereign Air-Gapped Deployment

Single-command Helm deployment into isolated Kubernetes enclaves with zero external cloud dependencies or telemetry leaks.

CONSULTING & ENGINEERING SERVICES

Specialized Operational Capabilities

CORE DOCTRINE

Defensive Cyber Operations (DCO)

Strategic adversary hunting and real-time killchain disruption built on 19+ years of joint military cyber operations. We intercept intrusions before data exfiltration or operational paralysis can occur.

  • 24/7 active threat monitoring & tactical containment
  • Memory-level payload & exploit neutralization
  • Automated micro-segmentation enclaves
  • Continuous forensic attribution analysis
Engage Principal Architect
ARCHITECTURE

Zero-Trust & Network Fortification

Architecting sovereign, hardened network topologies with strict identity verification, micro-segmentation, and zero-implicit trust across all cloud, on-prem, and air-gapped enclaves.

  • Air-gapped enclave design & segmentation strategy
  • Mutual TLS & cryptographic access boundary control
  • BGP routing security & DDoS kinetic mitigation
  • Ephemeral credential management systems
Engage Principal Architect
INTELLIGENCE

Threat Intelligence & Adversary Profiling

Equipping security teams with proactive intelligence briefings. We decode state-sponsored APT campaign methodologies and anticipate adversary moves.

  • APT killchain threat mapping
  • SIGINT-informed early warning alerts
  • Adversary infrastructure attribution
  • Executive threat intelligence briefings
Engage Principal Architect
ENGINEERING

Tailored Software & Automated Tooling

Custom-built security tooling, automated workflows, and bespoke defensive software platforms designed around your specific operational needs.

  • Custom security operations dashboards
  • Automated quarantine & containment bots
  • SIEM/SOAR workflow custom integrations
  • Zero-trust API gateway security filters
Engage Principal Architect
ASSESSMENT

Security Assessments & Red Teaming

Comprehensive security posture evaluations and black-box penetration testing that uncover critical vulnerabilities across your entire digital ecosystem.

  • Full-scope penetration testing & red team exercises
  • Cloud architecture vulnerability analysis
  • Compliance verification (NIST / CMMC / ISO)
  • Actionable remediation roadmaps with principal debriefs
Engage Principal Architect
ADVISORY

Executive Advisory & Cyber Governance

Direct strategic partnership for CISOs, technology executives, and boards of directors. We translate technical posture into executive risk governance.

  • CISO strategic advisory & board briefings
  • Crisis management & incident governance playbooks
  • Cyber risk quantification & cyber insurance audit
  • Defense-in-depth posture roadmapping
Engage Principal Architect

Ready to Fortify Your Infrastructure?

Consult directly with Principal Consultants G. Grau for a comprehensive tactical scope.